CompTIA Security+ SY0-801 Practice Exam
CompTIA Security+ SY0-801
The CompTIA Security+ SY0-801 certification validates the core skills needed to secure networks, endpoints, cloud services and AI-enabled environments. The exam covers five domains: General Security Concepts (16%), Threats, Vulnerabilities, and Attacks (24%), Security Architecture (19%), Security Operations (27%) and Security Program Management and Oversight (14%). Candidates demonstrate knowledge of control types, cryptography, threat actors, AI usage threats, indicators of malicious activity, zero trust, identity and access management, incident response and governance, risk and compliance. This practice exam mirrors that style with single-answer, multiple-answer, drag and drop and exhibit-based questions.
Exam version: V8
998 questions in the bank
Question bank updated : questions, answers, explanations and chapters.
Certification Overview
- Exam name: Security+ SY0-801
- Vendor: CompTIA
- Exam code: SY0-801
- Duration: 90 minutes
- Total questions: about 90
- Official passing score: 750 on a scale of 100-900 (source)
- Our practice exam pass mark: 75%
Who Should Take This Exam?
Security Administrator, Systems Administrator, Network Administrator, Security Analyst, SOC Analyst, Security Specialist, Junior IT Auditor, Junior Penetration Tester
Prerequisites
No formal prerequisite. CompTIA recommends two years of hands-on experience as a security administrator.
Topics Covered
- General Security Concepts
- Threats, Vulnerabilities, and Attacks
- Security Architecture
- Security Operations
- Security Program Management and Oversight
Question Types
- Multiple Choice (Single Answer)
- Multiple Choice (Multiple Answers)
- Drag and Drop
- Scenario-Based
Security+ SY0-801 Practice Questions
Our question bank contains 998+ practice questions for this certification. Sample questions from each exam chapter. Expand a question to see the answer choices. With full access, you get unlimited practice exams with randomized questions from our full question bank.
General Security Concepts
A company runs mandatory phishing-awareness training for all employees. Which control category does this program fall under?
- A. Technical
- B. Operational Correct answer
- C. Physical
- D. Managerial
Option B is correct because security awareness training is an operational control, carried out by people as a routine process. Technical controls run in systems, physical controls protect facilities, and managerial controls cover planning, risk and policy.
Which control type is intended to discourage a potential attacker from attempting an intrusion, for example by displaying a warning sign?
- A. Compensating
- B. Corrective
- C. Directive
- D. Deterrent Correct answer
Option D is correct because deterrent controls, such as warning signs, are meant to discourage an attacker from trying. Compensating controls substitute for a missing control, corrective controls fix damage afterwards, and directive controls instruct behavior.
Which element of the CIA triad ensures that data has not been altered by an unauthorized party?
- A. Integrity Correct answer
- B. Confidentiality
- C. Availability
- D. Non-repudiation
Option A is correct because integrity means data has not been altered without authorization. Confidentiality limits who can read it, availability keeps it accessible, and non-repudiation prevents denying an action.
Which TWO of the following are technical controls? (Choose two)
- A. Host-based firewall Correct answer
- B. Full-disk encryption Correct answer
- C. Security guard
- D. Security awareness training
- E. Acceptable use policy
Options A and B are correct because a host-based firewall and full-disk encryption are implemented in technology, so they are technical controls. A security guard is physical, awareness training is operational, and an acceptable use policy is managerial.
Threats, Vulnerabilities, and Attacks
Why does an access vestibule prevent tailgating better than a single badge-controlled door?
- A. Only one door can be open at a time, so a second person cannot slip through unnoticed Correct answer
- B. It requires a badge on both entry and exit, which creates a complete audit trail
- C. It uses a stronger encryption standard on the badge credential than a single door
- D. It lets a guard verify identity at the outer door before the inner one unlocks
Option A is correct because an access vestibule lets only one door open at a time, so a second person cannot follow through unnoticed. Audit trails, badge encryption and guard checks are separate features that do not stop tailgating in the same way.
Which class of cryptographic algorithms is most directly threatened by a sufficiently large quantum computer running Shor's algorithm?
- A. Symmetric block ciphers such as AES-256
- B. Cryptographic hash functions such as SHA-256
- C. Password-based key stretching functions
- D. Asymmetric algorithms such as RSA and ECC Correct answer
Option D is correct because Shor's algorithm breaks RSA and ECC because it efficiently factors integers and solves discrete logarithms. Symmetric ciphers, hashes and key stretching are only weakened, not broken.
Which TWO physical measures directly prevent tailgating through a controlled entrance? (Choose two)
- A. Access vestibule Correct answer
- B. Turnstile Correct answer
- C. Bollards
- D. Fence around the parking lot
- E. Security camera at the entrance
Options A and B are correct because a vestibule and a turnstile admit one person at a time. Bollards stop vehicles, a fence protects a lot, and a camera only records.
Based on the log shown, which statement best describes the activity from 203.0.113.45?
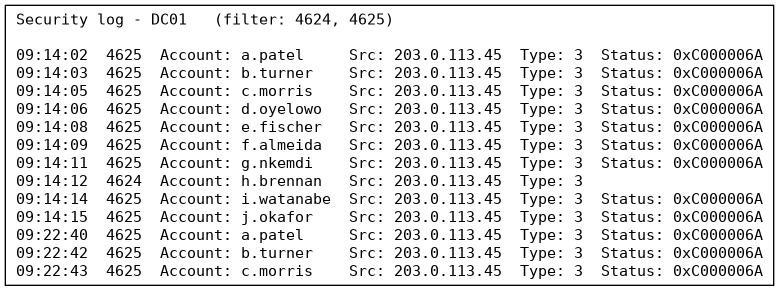
- A. A single password was tried across many accounts, and h.brennan authenticated successfully Correct answer
- B. Users mistyped passwords after a scheduled password reset across the domain
- C. A service account failed repeatedly because its stored password had expired
- D. Many passwords were tried against a.patel until that account was locked out
Option A is correct because the same source fails against many different accounts and one login, h.brennan, succeeds, which is password spraying. Trying many passwords against one account would show repeated failures for a.patel only, and a password reset or expired service account would not produce failures across many users.
Security Architecture
A system evaluates device posture, location and recent behavior on every request instead of trusting a login made hours earlier. Which zero trust concept is this?
- A. Implicit trust
- B. Perimeter defense
- C. Static role assignment
- D. Adaptive identity Correct answer
Option D is correct because adaptive identity re-evaluates trust from context such as device posture, location and behavior on every request. Implicit trust and perimeter defense rely on earlier trust, and static roles do not adapt.
A payment system replaces stored card numbers with random surrogate values while the real numbers are kept in a separate secure vault. What is this technique?
- A. Hashing
- B. Data masking
- C. Key stretching
- D. Tokenization Correct answer
Option D is correct because tokenization replaces sensitive values with surrogate tokens while the real data sits in a vault. Hashing and masking do not keep a retrievable original in a vault, and key stretching slows hashing.
Which TWO controls protect data at rest? (Choose two)
- A. Full-disk encryption Correct answer
- B. Transparent database encryption Correct answer
- C. TLS
- D. IPsec tunnel mode
- E. SSH tunnel
Options A and B are correct because full-disk encryption and transparent database encryption protect stored data. TLS, IPsec tunnel mode and SSH tunnels protect data in transit.
Which device can drop a malicious packet that FW1 has already permitted?
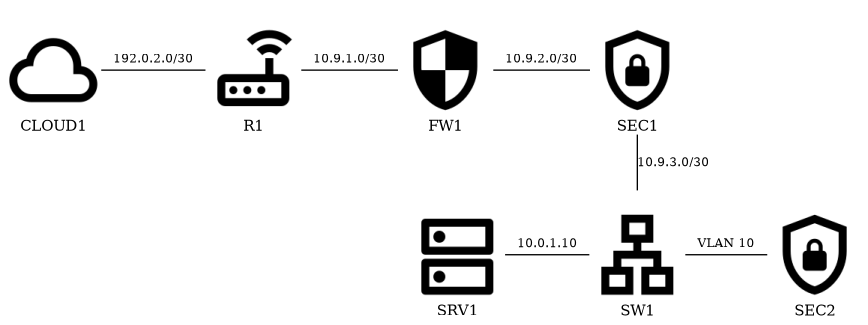
- A. SEC2
- B. SEC1 Correct answer
- C. SW1
- D. R1
Option B is correct because SEC1 sits inline between FW1 and SW1, so it can drop traffic FW1 allowed. SEC2 hangs off the switch and cannot block, and R1 is before the firewall.
Security Operations
A team places a decoy spreadsheet named payroll_backup.xlsx on a file server and configures an alert if anyone opens it. Which deception technique is this?
- A. Honeynet
- B. Honeyfile Correct answer
- C. Honeytoken
- D. Sinkhole
Option B is correct because a decoy file that alerts when opened is a honeyfile. A honeynet is a network of decoys and a honeytoken is fake data or credentials, while a sinkhole redirects malicious traffic.
A team seeds a code repository with fake cloud API keys that generate an alert whenever they are used. Which deception technique is this?
- A. Honeyfile
- B. Honeypot
- C. Honeytoken Correct answer
- D. Honeynet
Option C is correct because fake credentials or keys that alert when used are honeytokens. A honeyfile is a decoy file, a honeypot is a decoy system, and a honeynet is a decoy network.
Which TWO are deception technologies? (Choose two)
- A. Honeypot Correct answer
- B. Honeytoken Correct answer
- C. Jump server
- D. Network access control
- E. Data loss prevention agent
Options A and B are correct because honeypots and honeytokens are decoys that attract and detect attackers. A jump server, NAC and DLP are not deception tools.
Refer to the scan output shown. Which host's finding count is the least reliable indicator of how well it is patched?
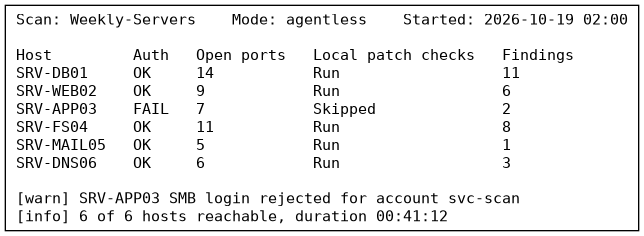
- A. SRV-APP03 Correct answer
- B. SRV-DNS06
- C. SRV-MAIL05
- D. SRV-WEB02
Option A, SRV-APP03, is correct because the scan shows an authentication FAIL and local patch checks Skipped, so its low count of 2 reflects missing credentialed checks rather than good patching. The other hosts authenticated and ran local patch checks, so their counts are more reliable.
Security Program Management and Oversight
An organization compares its current security posture with the requirements of a chosen framework to identify what is missing. What is this activity called?
- A. Penetration test
- B. Business impact analysis
- C. Gap analysis Correct answer
- D. Threat hunting
Option C is correct because gap analysis compares the current state with a desired framework or standard to find what is missing. Penetration tests, business impact analysis and threat hunting have different purposes.
After a major outage, which factor decides the order in which essential functions are brought back?
- A. Headcount of the department running them
- B. Purchase cost of the supporting systems
- C. Criticality from the business impact analysis Correct answer
- D. Age of the supporting hardware in the inventory
Option C is correct because the business impact analysis rates how critical each function is, and recovery priority follows that criticality. Department headcount, purchase cost and hardware age do not reflect the impact of the function being unavailable.
Which TWO are types of governance documents that specify requirements or instructions? (Choose two)
- A. Standard Correct answer
- B. Procedure Correct answer
- C. Invoice
- D. Purchase order
- E. Guideline
Options A and B are correct because standards and procedures specify requirements and instructions. Invoices, purchase orders and advisory guidelines do not.
Based on the register shown, which risk most urgently needs escalation?
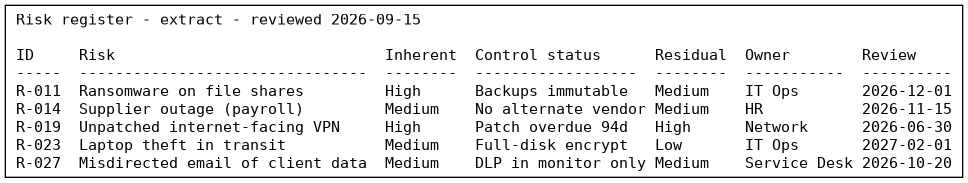
- A. R-019, because the residual rating is still High and the review date has passed Correct answer
- B. R-011, because ransomware carries the highest inherent rating
- C. R-027, because the DLP control is not yet blocking anything
- D. R-014, because no alternate supplier has been arranged
Option A is correct because R-019 is an internet-facing VPN with a patch overdue by 94 days, a residual rating still High, and a review date of 2026-06-30 that has already passed. The other risks have a Medium or Low residual rating and are still within their review dates.
Free Study Guide
Read the free CompTIA Security+ SY0-801 study guide: every exam topic explained in plain English, with diagrams, exam tips and the mistakes to avoid.
More CompTIA Practice Exams
Practice with realistic mock exams to prepare for your CompTIA certification.