CompTIA PenTest+ PT0-003 Practice Exam
CompTIA PenTest+ PT0-003
The CompTIA PenTest+ PT0-003 certification validates the skills needed to plan and scope a penetration test, perform reconnaissance and vulnerability discovery, execute attacks and exploits, and report findings with remediation guidance. The exam covers five domains: engagement management, reconnaissance and enumeration, vulnerability discovery and analysis, attacks and exploits, and post-exploitation and lateral movement. Candidates demonstrate hands-on skills with tools such as Nmap, Nikto, Burp Suite and hashcat, analyze scan output and shell sessions, exploit web, network, cloud and host targets, escalate privileges and pivot through segmented networks, and communicate results to stakeholders. The exam has a maximum of 90 questions over 165 minutes.
Exam version: V3
715 questions in the bank
Question bank updated : questions, answers, explanations and chapters.
Certification Overview
- Exam name: PenTest+ PT0-003
- Vendor: CompTIA
- Exam code: PT0-003
- Duration: 165 minutes
- Total questions: about 90
- Official passing score: 750 on a scale of 100-900 (source)
- Our practice exam pass mark: 75%
Who Should Take This Exam?
Penetration Tester, Security Consultant, Red Team Operator, Vulnerability Analyst, Application Security Specialist, Network Security Engineer
Prerequisites
No formal prerequisite. CompTIA recommends Network+ and Security+ or equivalent knowledge, plus 3-4 years of hands-on penetration testing or offensive security experience.
Topics Covered
- Engagement Management
- Reconnaissance and Enumeration
- Vulnerability Discovery and Analysis
- Attacks and Exploits
- Post-Exploitation and Lateral Movement
Question Types
- Multiple Choice (Single Answer)
- Multiple Choice (Multiple Answers)
- Drag and Drop
- Scenario-Based
PenTest+ PT0-003 Practice Questions
Our question bank contains 715+ practice questions for this certification. Sample questions from each exam chapter. Expand a question to see the answer choices. With full access, you get unlimited practice exams with randomized questions from our full question bank.
Engagement Management
In a penetration test's rules of engagement, what is the testing window primarily used to define?
- A. The billing rate that was agreed upon for the engagement overall
- B. The set of employees permitted to observe the test taking place on-site
- C. The list of tools the tester is authorized to install on the network
- D. The dates and times during which testing activities are authorized to occur Correct answer
Option D is correct because the testing window is precisely the dates and times during which testing activities are authorized, so anything outside it is unauthorized access. Option C (tool list) belongs in the scope or rules of engagement, not the window; Option B (on-site observers) and Option A (billing rate) are unrelated administrative details.
During scoping, what does target selection determine for a penetration test?
- A. The license tier of the vulnerability scanner that will be used
- B. The billing schedule the client will follow across the engagement
- C. The specific systems and networks that are authorized for testing Correct answer
- D. The formatting template the tester must follow for the report
Option C is correct because target selection during scoping is what fixes which systems and networks the tester may legally touch. Option B (billing schedule), Option D (report template), and Option A (scanner license tier) are all logistics that don't define authorization.
Which document authorizes a tester to perform activities that would otherwise be unauthorized access, and must be signed before testing starts?
- A. A vulnerability scan report left over from a prior engagement
- B. An invoice that estimates the total cost of the engagement
- C. The signed rules of engagement or scoping agreement for this test Correct answer
- D. A non-disclosure agreement that covers only the tester's own employer
Option C is correct because the signed rules of engagement or scoping agreement is the document that turns otherwise-unauthorized access into authorized testing. An invoice, an old scan report, or an NDA covering only the tester's employer provide no legal authorization to test.
Which TWO items should be explicitly documented in a penetration test's rules of engagement before testing begins? (Choose two)
- A. The authorized testing window and any blackout periods Correct answer
- B. The vendor logo to be used on the client's next product release
- C. The client's internal marketing budget for the following quarter
- D. The IP ranges and hosts that are explicitly in scope Correct answer
- E. The tester's personal home address for delivery of hardware
Options A and D are correct because the authorized testing window (with any blackout periods) and the explicit IP ranges and hosts in scope are exactly what the rules of engagement must document before testing begins. The remaining options - marketing budget, a tester's home address, and a vendor logo - have nothing to do with authorization or scope.
Reconnaissance and Enumeration
What is the defining characteristic of passive reconnaissance?
- A. A vulnerability scanner is pointed directly at the target's open ports
- B. The tester connects to the target's VPN using previously stolen credentials
- C. Crafted packets are sent to each host on the range to observe how it responds
- D. Information is gathered without directly interacting with the target's systems Correct answer
Option D is correct because passive reconnaissance is defined by gathering information without directly interacting with the target's systems. Sending packets, connecting with stolen credentials, or scanning open ports are all forms of active interaction.
What does the acronym OSINT stand for in the context of reconnaissance?
- A. Operational security incident notification sent to the target's admins
- B. On-site scanning of internal traffic captured from a switch port
- C. Open-source intelligence gathered from publicly available sources Correct answer
- D. Outbound session interception performed at the network perimeter
Option C is correct because OSINT stands for open-source intelligence gathered from publicly available sources. The other options invent unrelated meanings that don't correspond to any real reconnaissance term.
Which TWO of the following are examples of passive reconnaissance? (Choose two)
- A. Reviewing WHOIS records returned by a third-party lookup service Correct answer
- B. Searching certificate transparency logs for a target's subdomains Correct answer
- C. Connecting to a target's web server to view its HTTP response headers
- D. Running a port scan against a range of target IP addresses
- E. Sending crafted packets directly to a target host to observe its response
Options A and B are correct because reviewing WHOIS records and searching certificate transparency logs both gather information without directly touching the target's systems. Sending crafted packets, connecting to view headers, and running a port scan are all active interaction.
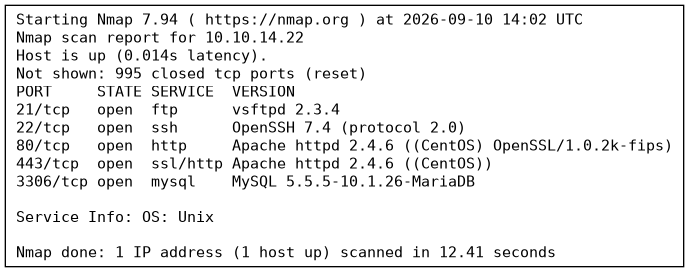
Examine the output shown. Which service on this host is running a version with a well-documented backdoor that allows unauthenticated remote command execution?
- A. The SSH service running OpenSSH 7.4
- B. The HTTP service running Apache httpd 2.4.6
- C. The FTP service running vsftpd 2.3.4 Correct answer
- D. The MySQL service running MariaDB 5.5.5-10.1.26
Option C is correct because vsftpd 2.3.4 has a well-documented backdoor (CVE-2011-2523) that allows unauthenticated remote command execution. The Apache, OpenSSH, and MariaDB versions shown in the scan carry no such backdoor.
Vulnerability Discovery and Analysis
What is the key difference between an authenticated and an unauthenticated vulnerability scan?
- A. An unauthenticated scan requires a signed API token issued by the scanner vendor
- B. An authenticated scan logs in with valid credentials to check internal configuration Correct answer
- C. An unauthenticated scan can only be launched from inside the target's own network
- D. An authenticated scan skips host discovery and jumps straight to exploitation
Option B is correct because an authenticated scan logs in with valid credentials to check internal configuration, which is the defining difference from an unauthenticated scan. An unauthenticated scan isn't limited to internal launch points, doesn't skip straight to exploitation, and doesn't require a vendor-signed token.
What does the acronym SAST stand for in the context of vulnerability discovery?
- A. System access security tracking performed at the network layer
- B. Session-aware sandboxed testing conducted inside a container runtime
- C. Static application security testing performed against source or binaries Correct answer
- D. Sequential authentication scanning technique used against login forms
Option C is correct because SAST stands for static application security testing, performed against source code or binaries without running the application. The other options invent unrelated terms with no standing in vulnerability discovery.
Which TWO characteristics distinguish an authenticated vulnerability scan from an unauthenticated one? (Choose two)
- A. It skips the TCP handshake, making it faster over slow links
- B. It requires no plugin feed to be current before running
- C. It logs in with valid credentials to inspect internal configuration Correct answer
- D. It only supports scanning a single target host per scan job
- E. It can directly query installed software and patch levels Correct answer
Options C and E are correct because an authenticated scan logs in with valid credentials to inspect internal configuration and can directly query installed software and patch levels. It doesn't skip the TCP handshake, isn't limited to a single host per job, and does still need a current plugin feed.
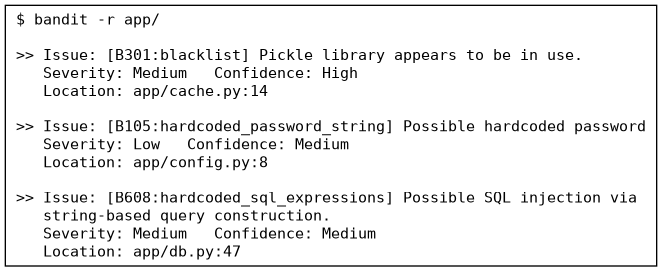
Refer to the Bandit output shown. Which finding most directly indicates the codebase is vulnerable to a classic web application injection attack?
- A. The B301 finding in app/cache.py, which flags use of the pickle library
- B. The confidence rating attached to the B608 finding, which is Medium rather than High
- C. The B105 finding in app/config.py, which flags a hardcoded password string
- D. The B608 finding in app/db.py, which flags string-based SQL query construction Correct answer
Option D is correct because the B608 finding flags string-based SQL query construction in app/db.py, which is the classic mechanism behind SQL injection. B301 flags an unrelated deserialization risk (pickle), B105 flags a hardcoded password rather than an injection flaw, and the confidence rating on B608 doesn't change what vulnerability class it represents.
Attacks and Exploits
What is VLAN hopping?
- A. A denial-of-service technique aimed directly at a DHCP relay agent
- B. A technique used to gain access to VLANs other than the attacker's assigned one Correct answer
- C. A technique for cracking the passphrase on a WPA2 wireless network
- D. A method for cloning the MAC address of a switch's uplink port
Option B is correct because VLAN hopping is defined as a technique for gaining access to VLANs other than the attacker's own assigned VLAN. It isn't a DHCP relay DoS, a switch MAC clone, or a Wi-Fi passphrase attack.
What is the goal of an on-path, or man-in-the-middle, attack?
- A. To register a domain name that closely resembles the target's own brand
- B. To brute-force the login page of a target's web application
- C. To flood a target host with malformed packets until it stops responding
- D. To intercept and potentially alter traffic between two communicating parties Correct answer
Option D is correct because an on-path (man-in-the-middle) attack aims to intercept and potentially alter traffic between two communicating parties. It isn't registering a lookalike domain, flooding a host, or brute-forcing a login page.
Which TWO VLAN hopping techniques are recognized methods for gaining access to a VLAN other than the attacker's assigned one? (Choose two)
- A. MAC flooding, overwhelming the switch's content-addressable memory table
- B. ARP spoofing, associating an attacker's MAC with a victim's IP
- C. Switch spoofing, negotiating a trunk link directly with the switch Correct answer
- D. Double tagging, exploiting a native VLAN mismatch Correct answer
- E. DHCP starvation, exhausting the pool of available lease addresses
Options C and D are correct because switch spoofing (negotiating a trunk directly) and double tagging (exploiting a native VLAN mismatch) are both recognized VLAN hopping techniques. MAC flooding, DHCP starvation, and ARP spoofing are real attacks but none of them is a VLAN hopping method.
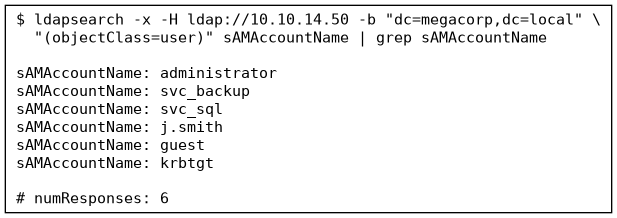
Examine the output shown. Which account is most likely a service account worth targeting for a Kerberoasting attempt?
- A. j.smith, since human user accounts are the most common Kerberoasting targets
- B. administrator, since it holds the highest privilege level in the domain
- C. svc_sql, since its naming convention matches a service account likely to hold a registered SPN Correct answer
- D. guest, since it is enabled by default in most domain builds
Option C is correct because svc_sql's naming convention marks it as a likely service account, which is exactly the kind of account that holds a registered SPN worth Kerberoasting. administrator, guest, and j.smith are either too high-value to target this way, a default account, or an ordinary human user account less likely to carry an SPN.
Post-Exploitation and Lateral Movement
Which party typically defines the data handling and destruction requirements a tester must follow after an engagement ends?
- A. The professional body that issues the tester's certification
- B. The company that publishes the vulnerability scanning tool used
- C. Whichever employee happens to be interviewed during the engagement
- D. The client organization, as documented in the contract or scope agreement Correct answer
Option D is correct because the client organization, through its contract or scope agreement, is what defines post-engagement data handling and destruction requirements - not the scanner vendor, a certification body, or whichever employee happens to be asked.
What is the primary purpose of establishing persistence on a compromised host?
- A. To maintain access even after a reboot or if the initial exploit vector closes Correct answer
- B. To automatically patch the vulnerability that was originally exploited
- C. To register the host with a new, unauthorized DNS domain name
- D. To increase the host's available disk space for later staging of tools
Option A is correct because establishing persistence exists to maintain access even after a reboot or if the initial exploit vector closes. It isn't about increasing disk space, patching the original vulnerability, or registering a new DNS domain.
Which TWO purposes does establishing persistence on a compromised host serve during a penetration test? (Choose two)
- A. Increasing the host's available disk space for later tool staging
- B. Registering the host with a new, unauthorized DNS domain name
- C. Maintaining access after a reboot of the compromised host Correct answer
- D. Automatically patching the vulnerability that was originally exploited
- E. Maintaining access if the initial exploit vector is later patched Correct answer
Options C and E are correct because persistence maintains access after a reboot of the host and if the initial exploit vector is later patched. It doesn't increase disk space, patch the original vulnerability, or register a new unauthorized DNS domain.
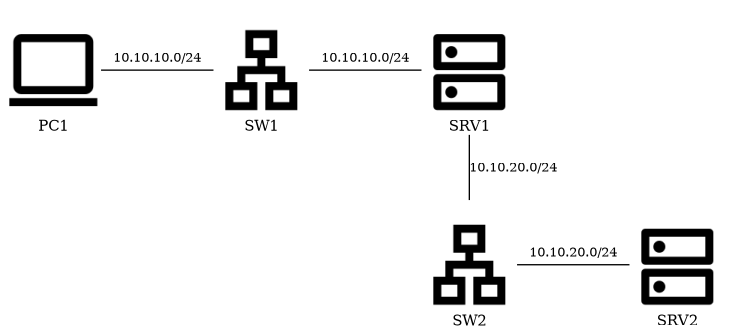
A tester has a foothold on PC1. Based on the diagram shown, which host provides the pivot point needed to reach SRV2?
- A. PC1, since it is the tester's own already-compromised starting point
- B. SW1, since it is the first switch the traffic from PC1 passes through
- C. SRV1, since it is the only device with an interface on both subnets Correct answer
- D. SW2, since it is directly connected to SRV2 itself
Option C is correct because SRV1 is the only device shown with an interface on both the 10.10.10.0/24 and 10.10.20.0/24 segments, making it the pivot point to reach SRV2. SW1 and SW2 are switches on a single segment each, and PC1 is the attacker's own starting host.
Free Study Guide
Read the free CompTIA PenTest+ PT0-003 study guide: every exam topic explained in plain English, with diagrams, exam tips and the mistakes to avoid.
More CompTIA Practice Exams
Practice with realistic mock exams to prepare for your CompTIA certification.