CompTIA SecurityX CAS-005 Practice Exam
CompTIA SecurityX CAS-005
The CompTIA SecurityX CAS-005 certification (formerly CASP+) validates the advanced skills senior security professionals use to architect, engineer, and operate enterprise security solutions. The exam covers four domains: governance, risk, and compliance; security architecture; security engineering; and security operations. Candidates demonstrate expert-level judgment in zero trust and hybrid cloud architecture, IAM federation, cryptographic solutions, incident response, and risk management, analyzing exhibits such as network diagrams, IAM policies, IaC snippets, and audit findings to make defensible architectural and governance decisions. The exam has a maximum of 90 questions over 165 minutes.
Exam version: V5
689 questions in the bank
Question bank updated : questions, answers, explanations and chapters.
Certification Overview
- Exam name: SecurityX CAS-005
- Vendor: CompTIA
- Exam code: CAS-005
- Duration: 165 minutes
- Total questions: about 90
- Official passing score: Pass/fail only, no scaled score (source)
- Our practice exam pass mark: 75%
Who Should Take This Exam?
Security Architect, Senior Security Engineer, Security Analyst, Security Consultant, SOC Manager, Security Engineer, Cloud Security Architect
Prerequisites
No formal prerequisite. CompTIA recommends Security+, CySA+ and PenTest+ or equivalent knowledge, plus 10 years of general IT experience including 5 years of security experience.
Topics Covered
- Governance, Risk, and Compliance
- Security Architecture
- Security Engineering
- Security Operations
Question Types
- Multiple Choice (Single Answer)
- Multiple Choice (Multiple Answers)
- Drag and Drop
- Scenario-Based
SecurityX CAS-005 Practice Questions
Our question bank contains 689+ practice questions for this certification. Sample questions from each exam chapter. Expand a question to see the answer choices. With full access, you get unlimited practice exams with randomized questions from our full question bank.
Governance, Risk, and Compliance
Which TWO governance documents work together to define mandatory technical baselines and the step-by-step instructions for applying them? (Choose two)
- A. Memoranda of understanding
- B. Procedures Correct answer
- C. Policies
- D. Guidelines
- E. Standards Correct answer
Options B and E are correct because standards set the mandatory, specific technical baselines an organization must meet, while procedures provide the step-by-step instructions for actually applying them. Option C (policies) states high-level intent rather than technical baselines, and Option D (guidelines) offers optional recommendations rather than mandatory requirements. Option A (memoranda of understanding) is an inter-organizational agreement, not an internal governance document pair like this.
Examine the risk register extract shown. Which entry applies a treatment strategy that shifts the financial impact of the risk to a third party without reducing the underlying threat?
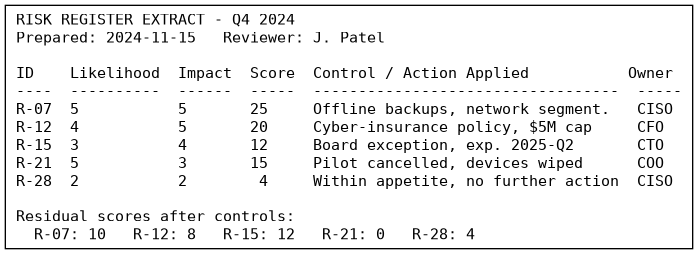
- A. R-07, because the offline backups and network segmentation reduce the likelihood and impact of the ransomware scenario to a manageable residual score
- B. R-15, because the board-approved exception formally documents that the organization tolerates the current risk level until the exception expiry date
- C. R-12, because the insurance policy allocates the monetary consequences of the risk to the insurer while the underlying threat itself remains unchanged Correct answer
- D. R-21, because canceling the pilot program and wiping all devices eliminates the risk scenario entirely by removing the vulnerable asset from the environment
Option C is correct because R-12's cyber-insurance policy shifts the monetary consequences of the risk to the insurer while the underlying ransomware threat itself is unchanged, which is textbook risk transference. Option A (R-07) reduces the risk through backups and segmentation, which is mitigation, not transfer, and Option B (R-15) is a board-approved exception, which is acceptance of the existing risk level. Option D (R-21) eliminates the risk scenario entirely by removing the asset, which is avoidance, not a shift of financial impact.
An enterprise is formalizing how security investment decisions are made. Which body approves the information security strategy and sets funding priorities across business units?
- A. Security steering committee, chaired by executives who set direction and funding Correct answer
- B. Incident response team, which coordinates containment and recovery during breaches
- C. Change advisory board, which evaluates production changes and schedules release windows
- D. Internal audit committee, which validates control effectiveness and reports findings
Option A is correct because a security steering committee, made up of business and IT executives, is the governance body responsible for approving strategy and allocating funding across the enterprise. Option B (incident response team) handles operational breach response, not strategic funding decisions. Options C (change advisory board) and D (internal audit committee) oversee change management and control assurance respectively, not investment prioritization.
At the enterprise level, which term expresses the total amount of risk leadership is willing to accept in pursuit of business objectives?
- A. Residual risk
- B. Risk appetite Correct answer
- C. Risk capacity
- D. Risk tolerance
Option B is correct because risk appetite defines the overall amount of risk an organization is willing to accept in pursuit of its objectives, set at the enterprise level. Option A (residual risk) is the risk remaining after controls are applied, not a target level. Options C (risk capacity) and D (risk tolerance) refer to the maximum risk an organization can absorb and the acceptable variation around a specific objective, respectively - narrower concepts than appetite.
Legal counsel asks which concept establishes that information stored in a particular country falls under that country's laws and courts. Which term applies?
- A. Data localization
- B. Data minimization
- C. Data sovereignty Correct answer
- D. Data residency
Option C is correct because data sovereignty holds that data is subject to the laws and legal jurisdiction of the country in which it is stored. Option D (data residency) only addresses the physical location of data, not the legal authority over it. Options A (data localization) is a regulatory requirement to keep data within a country, and B (data minimization) is a privacy principle about collecting only necessary data - neither concerns legal jurisdiction.
Security Architecture
A security governance review finds that several departments created their own shadow IT procurement channels. Which TWO governance controls together prevent future shadow IT purchases? (Choose two)
- A. An annual physical security audit of server rooms
- B. Quarterly rotation of IT support staff
- C. A centralized cloud access security broker (CASB) that discovers unsanctioned SaaS usage Correct answer
- D. A company-wide password-complexity standard
- E. A mandatory security review gate in the procurement approval workflow Correct answer
Options C and E are correct because a CASB that discovers unsanctioned SaaS usage catches shadow IT already in use, while a mandatory security review gate in procurement stops new shadow IT purchases before they happen, together addressing the problem from both directions. Option A (physical security audit) and D (password-complexity standard) address unrelated security domains, and Option B (rotating IT support staff) has no bearing on procurement governance.
Examine the network topology shown. Which benefit does routing Unit A, Unit B, and Unit C traffic through FW1 rather than peering each unit directly to the other two provide?
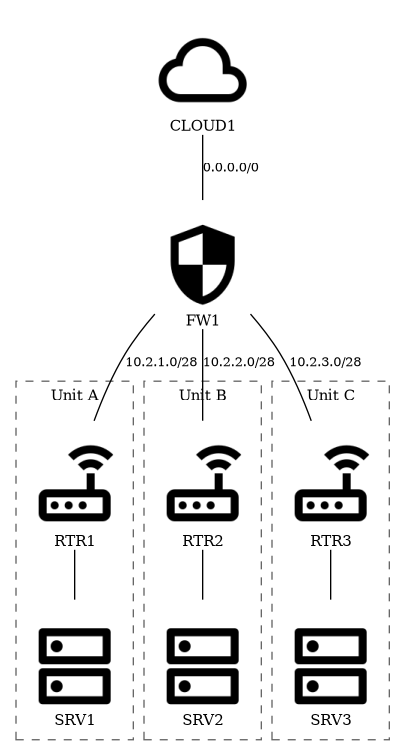
- A. Traffic between Unit A and Unit B is encrypted end-to-end in a way that FW1 is unable to inspect the payload
- B. Every unit's outbound and inter-unit traffic passes through one point where inspection policy is applied and maintained once, instead of being duplicated across multiple peering links Correct answer
- C. The design removes the need to assign non-overlapping IP address ranges to each unit's subnet
- D. Each unit gains a dedicated, redundant physical path to the internet that continues functioning even if FW1 fails
Option B is correct because routing all three units' traffic through FW1, as the diagram shows, means inspection policy is written and maintained once at that single choke point instead of being duplicated across three separate peering relationships. Option A is wrong since a single inspection point can still see plaintext or terminate TLS as designed, option C misattributes an addressing benefit to a topology change, and option D is the opposite of what the diagram shows, since FW1 is a single path, not a redundant one.
An API gateway accepts OIDC access tokens from the corporate authorization server. A review finds that a token minted for a low-value internal application is accepted by the finance API. Which validation step is missing at the gateway?
- A. Verifying that the signature validates against the current key in the JWKS endpoint.
- B. Verifying that the exp claim has not passed relative to the gateway's system clock.
- C. Verifying that the iss claim matches the authorization server's metadata.
- D. Verifying that the aud claim names the finance API's own resource identifier. Correct answer
Option D is correct because the aud (audience) claim identifies which resource server a token was issued for, and failing to check it lets a token minted for one API be replayed against another that trusts the same authorization server. Options A, B, and C describe legitimate validation steps (signature, expiration, issuer) that don't address confused-deputy token reuse across audiences.
When an employee is terminated in the HR system, the account stays usable in three SaaS applications for up to 24 hours. The identity provider is the SCIM source of truth for all three. Which change closes the gap most directly?
- A. Trigger SCIM deprovisioning from the HR termination event rather than the nightly batch push. Correct answer
- B. Move the three SaaS applications behind SAML single sign-on so authentication is centralized.
- C. Enable just-in-time provisioning at the SaaS applications so accounts are created on first login.
- D. Shorten the SaaS refresh token lifetime so user sessions expire sooner after termination.
Option A is correct because triggering SCIM deprovisioning directly from the HR termination event removes the 24-hour lag inherent in a nightly batch push, closing the account off immediately. Option B centralizes authentication but doesn't stop an already-issued SaaS session or local account from remaining active; option C addresses provisioning, not deprovisioning; and option D only shortens the window rather than closing it.
After an acquisition, an external forest trust is created. Users from the acquired forest log on to resource-forest servers successfully but are denied on shares whose permissions were granted through a universal group from their home forest. Which trust behavior explains this?
- A. Selective authentication requires the Allowed to Authenticate right on each server.
- B. SID filtering on the trust discards SIDs that are not from the trusted domain. Correct answer
- C. Name suffix routing excludes the acquired forest's alternate UPN suffix.
- D. The trust is non-transitive, so users from child domains are not authenticated.
Option B is correct because SID filtering (quarantining) on the trust strips out any SID in a user's authorization data that doesn't belong to the trusted domain's own namespace, which drops membership in a universal group defined back in the user's home forest even though direct logon still succeeds. Option A would block logon entirely rather than just resource access, option C affects UPN routing rather than group-based authorization, and option D would prevent authentication altogether rather than allowing logon but denying share access.
Security Engineering
An organization wants to implement multi-factor authentication for remote VPN access. Which TWO factor categories, when combined, constitute true MFA? (Choose two)
- A. A hardware FIDO2 security key (something you have) Correct answer
- B. A PIN that is the same as the password (something you know)
- C. A second password stored in the same password manager entry
- D. The username typed on the login form
- E. A memorized password (something you know) Correct answer
Options A and E are correct because a hardware FIDO2 key is something you have and a memorized password is something you know, and combining two different factor categories is what makes authentication genuinely multi-factor. Option B is really the same something-you-know category as the password and duplicates it rather than adding a second category, and option C and D are just another stored secret and the username, neither of which is a distinct authentication factor at all.
Refer to the network access control design shown. PC1 fails 802.1X authentication and times out onto its assigned VLAN. Based on the diagram, which resource can PC1 still reach?
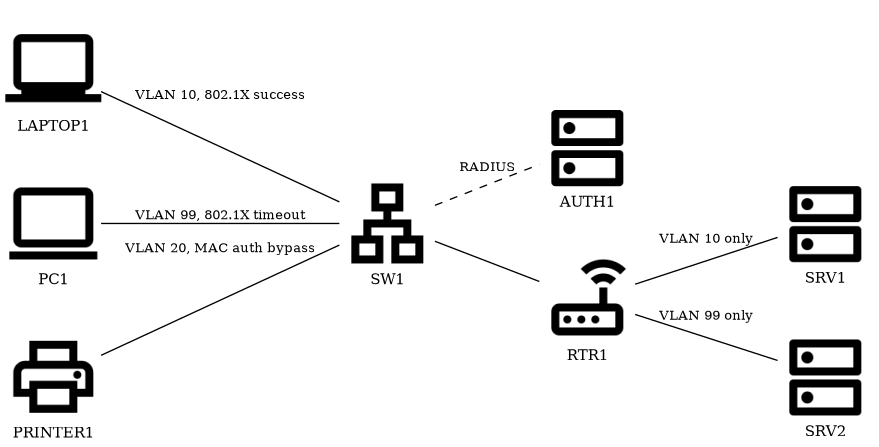
- A. SRV1, because a failed 802.1X attempt still assigns PC1 to the same VLAN as LAPTOP1
- B. Both SRV1 and SRV2, because SW1 grants access to every VLAN until authentication explicitly fails rather than times out
- C. SRV2, because PC1's fallback VLAN is the one RTR1 forwards to SRV2 Correct answer
- D. AUTH1, because PC1's RADIUS session remains open until the timeout is manually cleared
Option C is correct because the diagram shows PC1 times out onto VLAN 99 after a failed 802.1X attempt, and RTR1 forwards VLAN 99 traffic only to SRV2, so that's the resource PC1's fallback VLAN can reach. Option A confuses PC1's fallback VLAN with LAPTOP1's successful VLAN 10, option B overstates access beyond what the diagram's VLAN-scoped forwarding rules allow, and option D misreads AUTH1's role, which only handles the RADIUS exchange, not ongoing reachability.
Domain-joined workstations begin returning KRB_AP_ERR_SKEW during logon after a time source change. What is the default maximum clock difference Kerberos tolerates before it rejects an authenticator?
- A. Sixty minutes, after which the KDC treats the authenticator as a possible replay.
- B. Thirty seconds, after which the KDC treats the authenticator as a possible replay.
- C. Five minutes, after which the KDC treats the authenticator as a possible replay. Correct answer
- D. Fifteen minutes, after which the KDC treats the authenticator as a possible replay.
Option C is correct because Kerberos's default maximum clock skew tolerance (MaxClockSkew) is five minutes; authenticators outside that window are treated as possible replay attempts and rejected with KRB_AP_ERR_SKEW. Options A, B, and D name skew values that don't match the Kerberos protocol's default policy, whether in Active Directory or MIT Kerberos.
Users complete authentication at the identity provider, but the service provider now rejects every SAML response with an invalid signature error, although the same federation worked last week. What is the most likely cause?
- A. The IdP began issuing the NameID in transient format rather than the persistent format expected.
- B. The IdP's token-signing certificate was rotated and the SP still holds the previous public key. Correct answer
- C. The SP's assertion consumer service URL was changed to a path the IdP does not have registered.
- D. The clock on the SP drifted past the assertion's NotOnOrAfter condition window by a few minutes.
Option B is correct because SAML relies on the IdP's signing certificate to validate assertions; when that certificate is rotated but the SP's trust store isn't updated with the new public key, every subsequent assertion fails signature validation even though the federation worked previously. Option A would produce a NameID format mismatch error rather than a signature failure, option C would cause the IdP to reject the request before a response is even returned, and option D would produce an expired-assertion error, not an invalid-signature error.
A claims-aware web front end must reach a SQL back end as the requesting user. Impersonation succeeds for users who obtain a Kerberos ticket at logon but fails for users who authenticate with smart cards through a federation endpoint. Which delegation design resolves the failing path?
- A. Unconstrained delegation, which caches the user's forwardable TGT in the front end's LSASS memory.
- B. Constrained delegation with protocol transition, using S4U2Self to obtain a ticket for the user. Correct answer
- C. Kerberos-only constrained delegation, which requires the user to present a forwardable service ticket.
- D. Resource-based constrained delegation configured on the front end rather than on the SQL back end.
Option B is correct because constrained delegation with protocol transition uses S4U2Self to let the front end obtain a Kerberos ticket on behalf of a user who didn't authenticate with Kerberos in the first place, such as a smart-card user coming through a federation endpoint. Option A (unconstrained delegation) only works when the user already holds a forwardable TGT, option C still requires a Kerberos-only path, and option D changes where delegation is configured but doesn't solve the protocol-transition problem.
Security Operations
A CISO is building a security metrics program for board-level reporting. Which TWO metrics provide the board with actionable insight into the organization's risk posture? (Choose two)
- A. Mean time to remediate high-severity vulnerabilities (MTTR) Correct answer
- B. Total storage capacity used by the SIEM archive
- C. Total number of firewall rules across all network segments
- D. Percentage of critical assets with current risk assessments Correct answer
- E. Number of VPN tunnels configured across all sites
Options A and D are correct because mean time to remediate high-severity vulnerabilities and the percentage of critical assets with current risk assessments both give the board actionable insight into how exposed the organization is and how quickly it responds. Options B (SIEM storage capacity), C (total firewall rule count), and E (VPN tunnel count) are operational infrastructure statistics that don't communicate risk posture in a way a board can act on.
Which TWO cloud-native security services work together to detect misconfigurations and monitor runtime threats across IaaS workloads? (Choose two)
- A. A content delivery network (CDN) caching static assets
- B. A DNS registrar managing domain name records
- C. Cloud workload protection platform (CWPP) providing runtime threat detection on instances Correct answer
- D. Cloud security posture management (CSPM) scanning for configuration drift Correct answer
- E. A code repository hosting service
Options C and D are correct because a cloud workload protection platform detects runtime threats on running instances while cloud security posture management scans for configuration drift, and together they cover both the runtime and configuration sides of IaaS security monitoring. Option A, B, and E describe content delivery, DNS registration, and code hosting services that don't detect misconfigurations or runtime threats at all.
Within a SOC data pipeline, what does the log normalization stage produce?
- A. A reduced event stream in which duplicate and low-value records are dropped
- B. A common field schema so events from different sources can be correlated Correct answer
- C. A cryptographic digest of each event used to prove the log was not altered
- D. A compressed archive of raw events moved to lower-cost long-term storage
Option B is correct because normalization maps fields from different log sources into a common schema, which is what lets a SIEM correlate events across those sources. Option A describes deduplication or filtering, not normalization. Option C describes log integrity hashing, and option D describes archival or tiering, neither of which is what the normalization stage produces.
A SOC ingests recursive DNS resolver logs alongside proxy logs and wants to surface hosts resolving algorithmically generated domains. Which feature computed over the DNS data best supports that detection?
- A. Mean TTL of the returned A records compared with the zone's SOA minimum value
- B. Count of distinct resolvers the host queried relative to the subnet's baseline
- C. Shannon entropy of the queried label combined with the NXDOMAIN response rate Correct answer
- D. Ratio of AAAA to A queries issued by the host over a rolling one-hour window
Option C is correct because algorithmically generated domains typically have high-entropy labels and drive a high NXDOMAIN rate as malware cycles through unregistered names looking for its active C2 domain. Option A (TTL) and option D (AAAA/A ratio) don't target the randomness that defines DGA output, and option B (resolver diversity) measures something unrelated to domain generation.
Refer to the SIEM notable events shown. Which login pair represents an actual account-compromise indicator rather than a benign impossible-travel false positive?
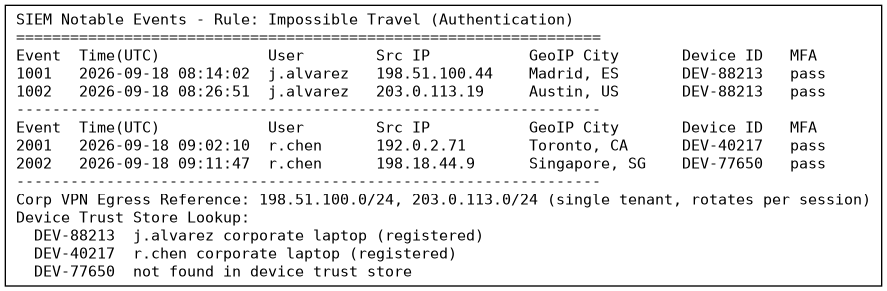
- A. The j.alvarez pair, because two logins eleven minutes apart from different countries do not fit a single legitimate session over a corporate VPN connection
- B. The r.chen pair, because Toronto and Singapore sit farther apart than Madrid and Austin, making the travel time between them more clearly impossible
- C. The j.alvarez pair, because the registered device ID stayed the same between logins while the reported source city changed twice within the same hour
- D. The r.chen pair, because the second login used DEV-77650, a device absent from the trust store, from an IP outside the VPN egress ranges Correct answer
Option D is correct because r.chen's second login used DEV-77650, a device that isn't in the trust store, from an IP address outside the corporate VPN's egress ranges, which is what actually distinguishes a real compromise from a benign geolocation artifact. Options A and C both flag j.alvarez, but that pair's two source IPs both fall within the referenced VPN egress ranges that rotate apparent location per session, and the device ID stayed the same trusted laptop throughout, so it's the expected false-positive pattern. Option B correctly identifies r.chen but for the wrong reason: raw geographic distance between login cities doesn't distinguish a compromise from a false positive the way the untrusted device and out-of-range IP do.
Free Study Guide
Read the free CompTIA SecurityX CAS-005 study guide: every exam topic explained in plain English, with diagrams, exam tips and the mistakes to avoid.
More CompTIA Practice Exams
Practice with realistic mock exams to prepare for your CompTIA certification.