Cisco CCNP 300-410 ENARSI Practice Exam
Cisco Certified Network Professional Enterprise Advanced Routing and Services 300-410
The Cisco CCNP 300-410 ENARSI certification validates skills in implementing and troubleshooting advanced enterprise routing and services. The exam covers Layer 3 technologies, VPN technologies, infrastructure security, and infrastructure services. Candidates demonstrate knowledge of EIGRP, OSPF, BGP, redistribution, route maps, policy-based routing, VRF-Lite, BFD, MPLS, MPLS Layer 3 VPN, DMVPN, AAA, ACLs, uRPF, CoPP, IPv6 first-hop security, SNMP, syslog, DHCP, IP SLA, NetFlow, and Catalyst Center Assurance. The exam consists of 100 questions over 90 minutes, with an 80% passing score.
Exam version: v1.1
874 questions in the bank
Question bank updated : questions, answers, explanations and chapters.
Certification Overview
- Exam name: CCNP 300-410 ENARSI
- Vendor: Cisco
- Exam code: 300-410
- Duration: 90 minutes
- Total questions: about 100
- Our practice exam pass mark: 80%
Who Should Take This Exam?
Network Engineer, Network Administrator, Network Support Engineer, Systems Engineer, Network Consultant, NOC Engineer, Enterprise Network Engineer, Network Security Engineer
Prerequisites
Valid Cisco Certified Network Associate (CCNA) certification or equivalent enterprise networking experience with routing, switching, and IP services.
Topics Covered
- Layer 3 Technologies
- VPN Technologies
- Infrastructure Security
- Infrastructure Services
Question Types
- Multiple Choice (Single Answer)
- Multiple Choice (Multiple Answers)
- Drag and Drop
- Scenario-Based
CCNP 300-410 ENARSI Practice Questions
Our question bank contains 874+ practice questions for this certification. Sample questions from each exam chapter. Expand a question to see the answer choices. With full access, you get unlimited practice exams with randomized questions from our full question bank.
Layer 3 Technologies
An engineer set up routing between several OSPF domains and created a routing loop that led to network instability. What action will fix the issue?
- A. Set a tag using the redistribute command toward a domain and deny inbound in the other domain by a matching tag. Correct answer
- B. Set a tag using the redistribute command toward a different domain and deny the matching tag when exiting from that domain.
- C. Set a tag using the network command in a domain and use the route-map command to deny the matching tag when exiting toward a different domain.
- D. Set a tag using the network command in a domain and use the route-map command to deny the matching tag when entering into a different domain.
When routes are redistributed between OSPF domains, routing loops occur when Domain B redistributes a route back into Domain A that originally came from Domain A. The fix is to tag routes as they leave Domain A (using a route-map with 'set tag'), then deny routes with that tag when they re-enter Domain A from Domain B (using a route-map matching the tag on the inbound redistribute). Tags are carried in LSAs and can be matched in distribute-lists or route-maps.
Network operations report problems with getting too many external routes, leading to CPU spikes on routers with less memory. What action will fix this?
- A. Configure the area range command when redistributing on ASBR.
- B. Configure the summary-address command when redistributing on ABR.
- C. Configure the area range command when redistributing on ABR.
- D. Configure the summary-address command when redistributing on ASBR. Correct answer
External route summarization in OSPF is performed on the ASBR using the 'summary-address' command (not 'area range', which is for inter-area summarization on ABRs). When too many external routes flood the network, summarizing on the ASBR reduces the number of Type 5 LSAs flooded throughout all non-stub areas, reducing CPU load on routers with limited resources.
What failure detection method is used for BFD?
- A. consistent rate Correct answer
- B. Layer 2 protocol failure
- C. variable rate
- D. routing protocol failure
BFD (Bidirectional Forwarding Detection) sends control packets at a fixed, consistent rate negotiated between peers. Failure is detected when a configured number of consecutive packets are missed. This consistent-rate detection is faster and more deterministic than routing protocol hello timers, which vary by protocol and are measured in seconds.
Which of the following OSPF Link State Advertisements (LSAs) were designed for IPv6 and are not applicable to IPv4 OSPF networks?
- A. Link LSA (Type 8) Correct answer
- B. Summary LSA (Type 3)
- C. Router LSA (Type 1)
- D. Intra-Area Prefix LSA (Type 9) Correct answer
- E. Opaque LSA (Type 9)
Link LSA (Type 8) and Intra-Area Prefix LSA (Type 9) are OSPFv3-specific LSAs that have no equivalent in OSPFv2. Link LSA carries a router's link-local address and IPv6 prefixes on a link. Intra-Area Prefix LSA carries IPv6 prefix information associated with a router or network LSA. These LSA types were introduced in OSPFv3 to handle IPv6 addressing separately from topology information.
PC1 cannot reach SRV1, and R5 has no OSPF routes learned from Area 0. Based on the exhibit, which change restores the missing inter-area routes?
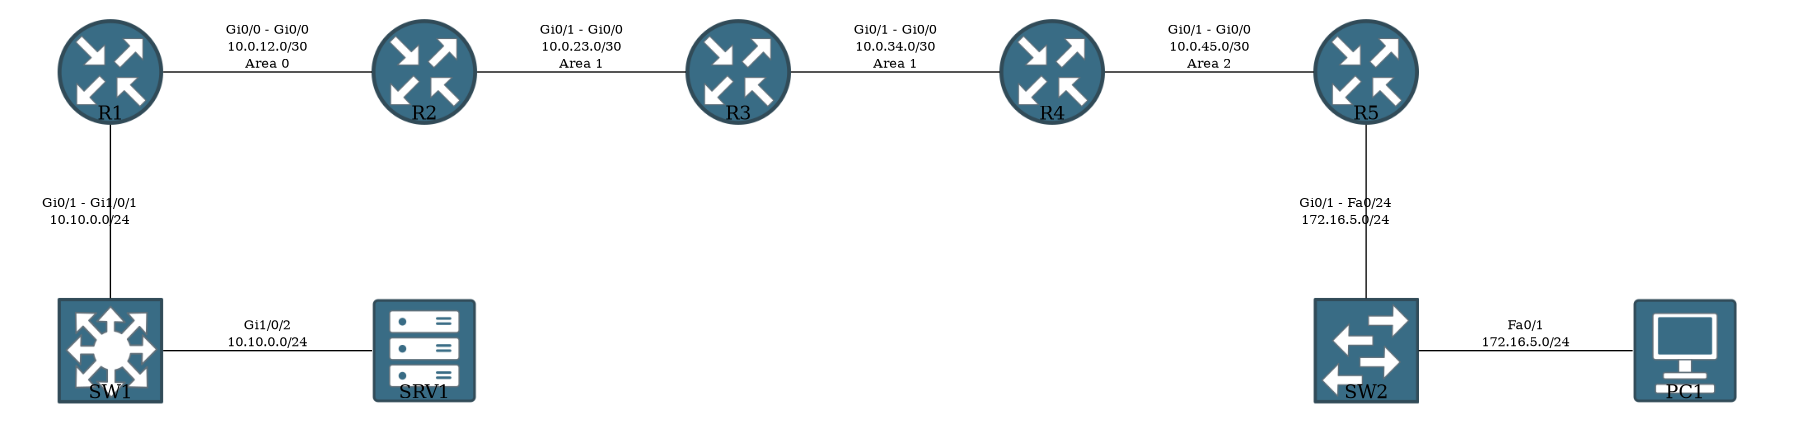
- A. Configure a virtual link between R1 and R4 that uses Area 1 as the transit area.
- B. Move the link between R3 and R4 into Area 0.
- C. Configure a virtual link between R2 and R4 that uses Area 1 as the transit area. Correct answer
- D. Configure a virtual link between R4 and R5 that uses Area 2 as the transit area.
Option C is correct because R4 sits between Area 1 (R3-R4) and Area 2 (R4-R5) and has no interface in Area 0, so Area 2 is cut off from the backbone. R2 is the ABR with Area 0 (toward R1) and Area 1 (toward R3), so a virtual link between R2 and R4 across transit Area 1 logically extends Area 0 to R4, which then advertises the inter-area routes into Area 2 and on to R5. A transit through Area 2 (A) or a virtual link to R1 (D) fails because R5 and R1 have no interface in the required transit area, and moving R3-R4 into Area 0 (B) would leave Area 0 split into two pieces.
VPN Technologies
What is the function of an OSPF sham-link?
- A. to allow inter-area routing when OSPF is used as the PE-CE connection protocol in an MPLS VPN network
- B. to allow intra-area routing when OSPF is used as the PE-CE connection protocol in an MPLS VPN network
- C. to correct OSPF backdoor routing when OSPF is used as the PE-CE connection protocol in an MPLS VPN network Correct answer
- D. to correct OSPF backdoor routing when OSPF is used as the PE-PE connection protocol in an MPLS VPN network
An OSPF sham-link corrects a routing problem that occurs when two VPN sites share a backdoor link in addition to their MPLS VPN connection. OSPF prefers the backdoor link because routes through it appear as intra-area (Type 1/2 LSAs) while routes via MPLS VPN appear as inter-area (Type 3 LSAs) or external, regardless of actual path cost. The sham-link makes the MPLS VPN path appear as intra-area, enabling proper OSPF metric comparison and preventing the backdoor link from always being preferred.
Which MPLS value is merged with the IP prefix to change it into a VPNv4 prefix?
- A. 8-byte Route Distinguisher Correct answer
- B. 8-byte Route Target
- C. 16-byte Route Target
- D. 16-byte Route Distinguisher
A VPNv4 prefix is created by prepending an 8-byte (64-bit) Route Distinguisher to a standard IPv4 prefix. For example, 10.1.1.0/24 with RD 1:1 becomes 1:1:10.1.1.0/88 as a VPNv4 address. This 8-byte extension ensures that overlapping IPv4 addresses from different customers become globally unique in the MP-BGP control plane. Route Targets are also 8 bytes but serve a different purpose (controlling import/export, not making prefixes unique).
customer is using an mGRE DMVPN tunnel over WAN infrastructure between hub and spoke sites. The current setup lets NHRP automatically add spoke routers to the multicast NHRP mappings. The customer is moving the network from IPv4 to IPv6 addressing for spokes' routers that support IPv6 and can run DMVPN tunnels over the IPv6 network. What configuration should be applied to support both IPv4 and IPv6 DMVPN tunnels on spoke routers?
- A. tunnel mode ipv6ip 6to4
- B. tunnel mode ipv6ip auto-tunnel Correct answer
- C. tunnel mode ipv6ip 6rd
- D. tunnel mode ipv6ip isatap
For spoke routers that need to support both IPv4 and IPv6 DMVPN tunnels, 'tunnel mode ipv6ip auto-tunnel' enables automatic IPv6-over-IPv4 tunneling. This creates tunnels where IPv6 addresses are automatically derived from the IPv4 address of the tunnel endpoint, allowing the spoke to participate in IPv6 DMVPN without manual tunnel endpoint configuration. This is the transition mode that supports the dual IPv4/IPv6 operation described in the scenario.
Which of the following are correct fields in an MPLS header?
- A. Label Correct answer
- B. Sequence Number
- C. Experimental (Exp) Correct answer
- D. Bottom of Stack (BoS) Correct answer
- E. Time to Live (TTL) Correct answer
- F. Checksum
The MPLS header contains four fields: Label (20 bits - the forwarding identifier), Experimental/TC (3 bits - used for QoS class marking, now called Traffic Class), Bottom of Stack (1 bit - set to 1 for the innermost label in a label stack, 0 for all others), and TTL (8 bits - Time To Live, prevents forwarding loops). Sequence Numbers and Checksums are NOT part of the MPLS header - those appear in higher-layer protocols.
A DMVPN uses tunnel subnet 172.16.0.0/24, with the router attached to SW1 as the only hub and spoke-to-spoke tunnels enabled. PC1 sends its first packet to LAP1. Based on the exhibit, what happens to that traffic?
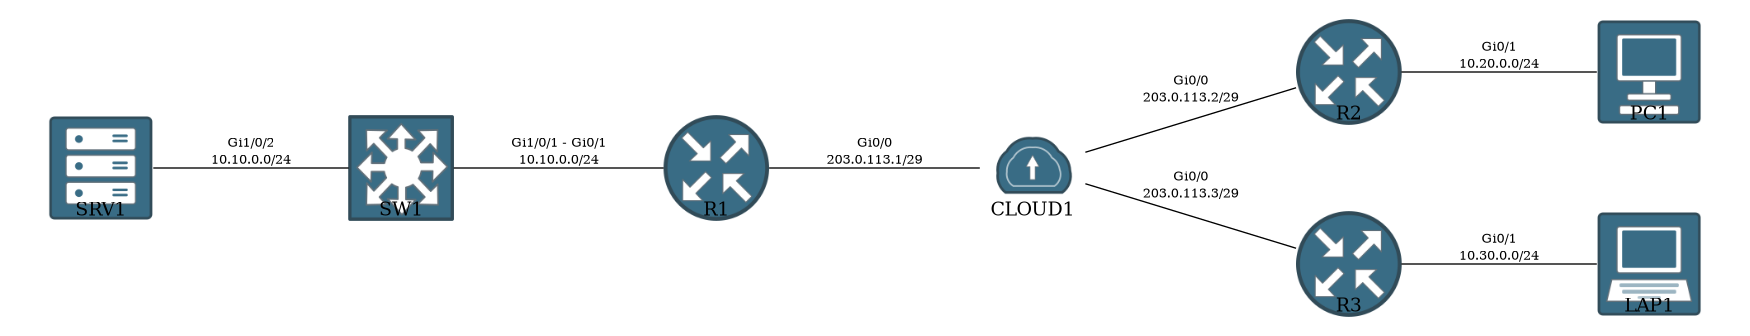
- A. All traffic always crosses R1, because spokes never build tunnels to each other.
- B. R2 sends it directly to R3 immediately, using a static NHRP mapping on R2.
- C. R2 forwards it unencrypted through CLOUD1, outside the tunnel network.
- D. It first crosses the hub, then NHRP resolves the remote public address and a direct R2-R3 tunnel is built. Correct answer
Option D is correct because in a DMVPN with spoke-to-spoke tunnels enabled, R2 initially has no NBMA address for LAP1's spoke R3, so the first packet follows the hub (R1) path. NHRP then resolves R3's public address (203.0.113.3) so R2 and R3 build a direct tunnel for subsequent traffic. R2 does not have a static mapping to R3 (B), spokes can build tunnels to each other (C), and the traffic stays inside the tunnel network 172.16.0.0/24 rather than being sent unencrypted (D).
Infrastructure Security
The IPv6 network is being attacked by an unknown source that isn't in the binding table or learned via neighbor discovery. Which feature helps stop the attack?
- A. IPv6 Destination Guard
- B. IPv6 Prefix Guard Correct answer
- C. IPv6 Router Advertisement Guard
- D. IPv6 Snooping
IPv6 Prefix Guard is specifically designed to block traffic from sources whose addresses don't belong to any delegated/authorized IPv6 prefix. When an attacker sends traffic from a spoofed or unknown source address that is neither in the binding table nor learned via Neighbor Discovery (making it untrackable by Source Guard alone), Prefix Guard blocks it by validating that the source address falls within a known delegated prefix. IPv6 Source Guard uses the binding table; IPv6 RA Guard blocks unauthorized router advertisements; IPv6 Snooping is the passive tracking mechanism.
The network administrator needs to deploy IPv6 in the network to permit only devices that have registered IP addresses and are connecting from designated locations. Which security feature should be implemented?
- A. IPv6 Snooping
- B. IPv6 Destination Guard
- C. IPv6 Router Advertisement Guard
- D. IPv6 Prefix Guard Correct answer
IPv6 Prefix Guard enforces that network devices can only source traffic from IP addresses that belong to prefixes delegated/registered to their specific location. It validates that each source IPv6 address is within an authorized prefix range associated with the network segment the packet arrived from. This allows the administrator to restrict communication to only those devices with 'registered IP addresses connecting from designated locations.' IPv6 Snooping builds the binding table; Destination Guard validates destinations; RA Guard blocks rogue advertisements.
The network administrator needs to set up R1 to authenticate telnet connections using Cisco ISE with RADIUS. ISE is set up with IP address 192.168.1.5 and has a network device pointing to R1 (192.168.1.1) with a shared secret password of Cisco123. If ISE is unavailable, the admin should be able to connect using the local database with the username and password admin/cisco123. The administrator has configured the following on R1: aaa new-model ! username admin password cisco123 ! radius server ISE1 address ipv4 192.168.1.5 key Cisco123 ! aaa group server tacacs+ RAD-SERV server name ISE1 ! aaa authentication login RAD-LOCAL group RAD-SERV Which two configuration changes will resolve the issue?
- A. aaa authentication login RAD-SERV group RAD-LOCAL local
- B. aaa authentication login RAD-LOCAL group RAD-SERV local Correct answer
- C. line vty 0 4 login authentication RAD-LOCAL Correct answer
- D. line vty 0 4 login authentication default
- E. line vty 0 4 login authentication RAD-SERV
Two issues in the configuration: (1) The method list 'RAD-LOCAL' is configured as 'group RAD-SERV' without a local fallback - the fix adds 'local' at the end: 'aaa authentication login RAD-LOCAL group RAD-SERV local', enabling local database authentication when ISE is unavailable. (2) VTY lines are not configured to use RAD-LOCAL - without 'login authentication RAD-LOCAL' on 'line vty 0 4', the default method list is used and the custom RAD-LOCAL list never applies to Telnet/SSH connections.
What does the IPv6 DHCP Guard feature do for DHCP messages?
- A. If the device is configured as a DHCP server, no message is switched.
- B. All client messages are always switched regardless of the device role. Correct answer
- C. It blocks only DHCP request messages.
- D. Only access lists are supported for matching traffic.
IPv6 DHCP Guard controls DHCP message flow based on the device's configured role (server or client). A key behavior: all DHCP client messages (DHCP Solicit, Request, Renew, Decline, Release) are ALWAYS forwarded regardless of the port's DHCP Guard role - client messages originate from hosts and must reach the server. Only DHCP server and relay messages (DHCP Advertise, Reply) are filtered based on whether the receiving port is trusted (configured as server-facing). Access lists are not the only matching method; the device role is the primary selector.
An extended ACL must block HTTP from 10.1.1.0/24 to SRV1 while permitting all other traffic, and it must stop this traffic as close to its source as possible. Based on the exhibit, where should the ACL be applied?
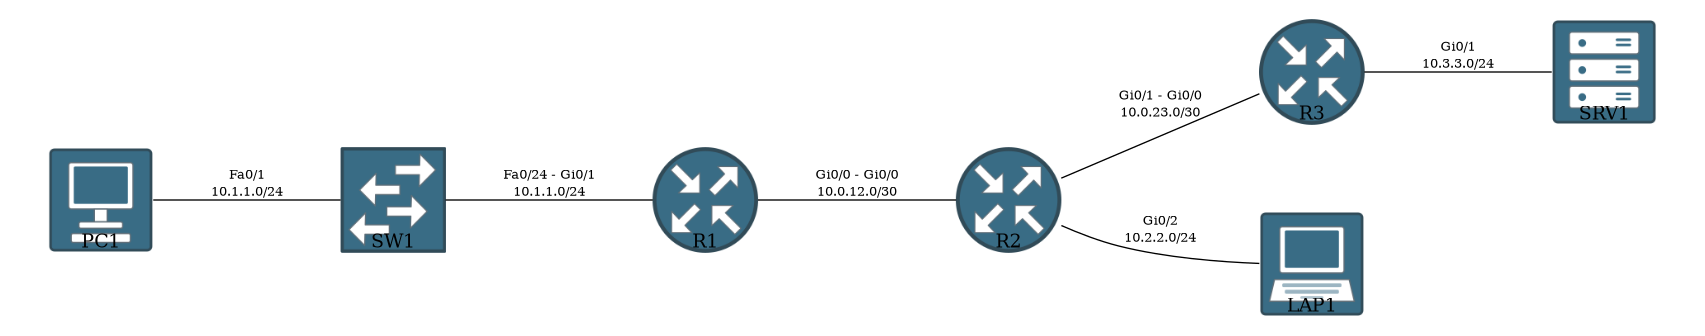
- A. Inbound on R1 Gi0/0.
- B. Inbound on R1 Gi0/1. Correct answer
- C. Outbound on R3 Gi0/1.
- D. Inbound on R2 Gi0/0.
Option B is correct because the traffic to be blocked originates in 10.1.1.0/24, which enters R1 on Gi0/1 from SW1, and an extended ACL should be placed as close to the source as possible. Applying it inbound on Gi0/1 stops the HTTP traffic to SRV1 (10.3.3.0/24) at the first router without letting it cross the network. Gi0/0 (A) faces R2, and R2 Gi0/0 (D) and R3 Gi0/1 (C) are farther from the source, where the ACL would waste bandwidth and could also block other traffic.
Infrastructure Services
What are the four steps of obtaining an IP address from a DHCP server that match the acronym DORA?
- A. Discover, Offer, Release, Addressing
- B. Discover, Obtain, Request, Acknowledge
- C. Determine, Offer, Release, Acknowledge
- D. Discover, Offer, Request, Acknowledge Correct answer
The DHCP process follows four steps summarized by the acronym DORA: (1) Discover - the client broadcasts a DHCP Discover message to find available DHCP servers; (2) Offer - a DHCP server responds with an IP address lease offer; (3) Request - the client broadcasts a DHCP Request to accept the offered address (also informs other DHCP servers their offers were not accepted); (4) Acknowledge - the server sends a DHCP Acknowledge confirming the lease. 'Release' is a separate DHCP message (not part of DORA), and 'Determine' and 'Obtain' are not DHCP message types.
SNMPv2 has been used across a network to manage all network devices. You have been requested to switch to an SNMPv3 solution instead. What is the main advantage of moving from SNMPv2 to SNMPv3?
- A. Enhanced security, including encryption of passwords Correct answer
- B. Enhanced performance, supporting more messages per minute.
- C. Enhanced scaling, supporting thousands more devices per network segment than SNMPv2.
- D. Using a push model instead of pull. SNMPv3 uses telemetry to push data to SNMP management stations in real time.
SNMPv3 adds two critical security enhancements over SNMPv2c: (1) Authentication - verifies that SNMP messages originate from legitimate sources using HMAC-MD5 or HMAC-SHA algorithms; (2) Privacy/Encryption - encrypts the SNMP payload using DES or AES to protect data in transit, including community strings (which SNMPv2c sends as cleartext). SNMPv2c added bulk retrieval (GET-BULK) and inform messages but has no security beyond cleartext community strings. SNMPv3 performance, scale, and message model are similar to SNMPv2c - security is the primary motivation for upgrading.
You are setting up NetFlow on different network devices to see the types of traffic being used. How many export destinations can this network data be sent to?
- A. Up to 2 Correct answer
- B. Up to 4
- C. Up to 8
- D. There is no limitation on the number of flow data export destinations.
Cisco's traditional NetFlow (versions 1-9) on a router supports a maximum of 2 simultaneous flow export destinations. This means NetFlow data can be sent to up to two NetFlow collectors simultaneously. If more collectors are needed, an intermediate flow broker/aggregator is required. Flexible NetFlow (FNF) may allow different configurations, but the traditional limitation for standard NetFlow export is 2 destinations. Planning NetFlow deployments must account for this constraint.
Which of the following are valid DHCP options that DHCP servers can set for DHCP clients when offering a lease?
- A. DHCP Option 1: subnet mask Correct answer
- B. DHCP Option 3: Lease Duration
- C. DHCP Option 4: Client host name
- D. DHCP Option 6: DNS servers Correct answer
DHCP option numbers are standardized in RFC 2132. Key options: Option 1 = Subnet Mask (the netmask for the assigned IP address); Option 3 = Router (default gateway, NOT lease duration); Option 6 = Domain Name Server (DNS server addresses); Option 12 = Host Name (client hostname, NOT option 4); Option 15 = Domain Name; Option 51 = IP Address Lease Time (lease duration, NOT option 3); Option 66 = TFTP Server Name. Options 1 and 6 are the two correct answers.
SRV1 at 10.9.9.10 is the DHCP server, and clients on 10.1.1.0/24 receive no addresses. Based on the exhibit, which configuration on R1 lets the clients obtain addresses from SRV1?
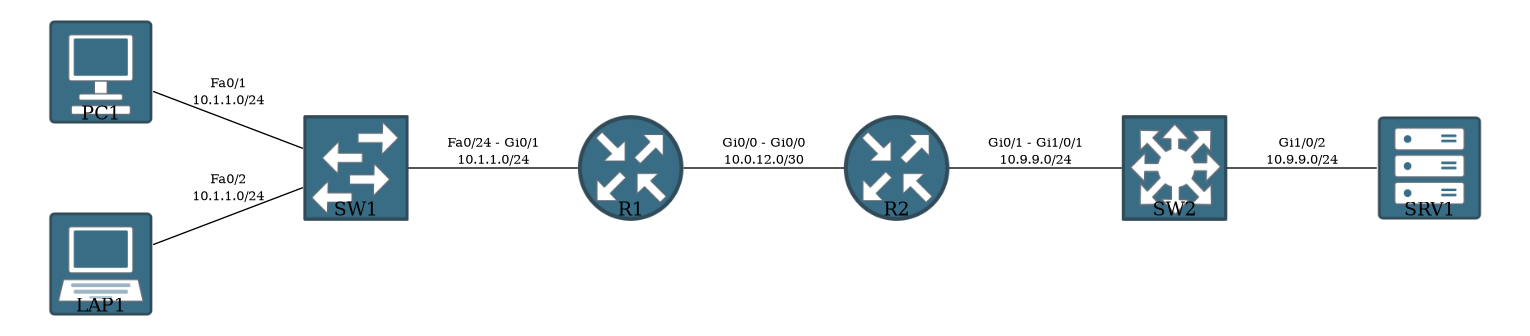
- A. ip helper-address 10.9.9.10 on Gi0/1. Correct answer
- B. ip dhcp relay information option on Gi0/1.
- C. ip helper-address 10.1.1.1 on Gi0/0.
- D. ip helper-address 10.9.9.10 on Gi0/0.
Option A is correct because the DHCP clients (PC1 and LAP1) reach R1 on Gi0/1 (10.1.1.0/24), and DHCP discovers are broadcasts that R1 will not route. ip helper-address 10.9.9.10 on the client-facing Gi0/1 makes R1 forward them as unicast to SRV1, reachable via R2. Placing it on Gi0/0 (D) is on the wrong interface, since there are no clients there, pointing the helper at the local gateway (C) is wrong, and relay information option (B) does not forward DHCP requests.
Free Study Guide
Read the free Cisco CCNP 300-410 ENARSI study guide: every exam topic explained in plain English, with diagrams, exam tips and the mistakes to avoid.
More Cisco Practice Exams
- Cisco CCST 100-150 Networking Practice Exam
- Cisco CCST 100-160 Cybersecurity Practice Exam
- Cisco CCNA 200-201 CCNACBR Practice Exam
- Cisco CCNA 200-301 Practice Exam
- Cisco CCNA 200-901 CCNAAUTO Practice Exam
- Cisco CCNP 300-710 SNCF Practice Exam
- Cisco CCNP 300-715 SISE Practice Exam
- Cisco CCNP 350-401 ENCOR Practice Exam
- Cisco CCNP 350-501 SPCOR Practice Exam
- Cisco CCNP 350-701 SCOR Practice Exam
Practice with realistic mock exams to prepare for your Cisco certification.