Capabilities of Microsoft Security Solutions · Topic 4 of 5
Microsoft Sentinel
SC-900 Microsoft Sentinel: SIEM and SOAR defined, data connectors, analytics rules, incidents, hunting, workbooks and playbooks for automated response.
- 5 min
- Includes a diagram
- Sentinel is a cloud native SIEM and SOAR.
- It collects data from many sources with data connectors, into a Log Analytics workspace.
- Analytics rules detect threats and generate alerts, which are grouped into incidents.
What it is
Microsoft Sentinel is a cloud native security tool for security operations teams. It is a SIEM and a SOAR.
- SIEM, security information and event management, collects security data from across the organisation, looks for threats in it, and raises alerts.
- SOAR, security orchestration, automation and response, automates how those alerts are handled, so common tasks run without a person.
Sentinel runs in the cloud, so there is no server to build, and it scales as the amount of data grows.
How it works
Collect
Sentinel gathers data using data connectors. There are connectors for Microsoft services such as Microsoft Entra ID, Microsoft 365 and Defender products, for Azure resources, and for third party systems such as firewalls, other clouds and other security tools. The data is stored in a Log Analytics workspace, and you query it with Kusto Query Language (KQL).
Detect
Analytics rules run queries over the data on a schedule or in near real time. When a rule's query finds a match, it generates an alert. Sentinel comes with many built in rule templates, and you can write your own. It can also use machine learning and user behaviour analytics to find unusual activity.
Related alerts are grouped into an incident, so an analyst sees one case for an attack instead of a flood of separate alerts.
Investigate
Analysts open an incident to see the alerts, the entities involved, such as accounts, hosts and addresses, and a timeline. They can hunt for threats proactively by running queries over the data before any alert fires. Workbooks are dashboards that visualise the data, for example sign in activity by location.
Respond
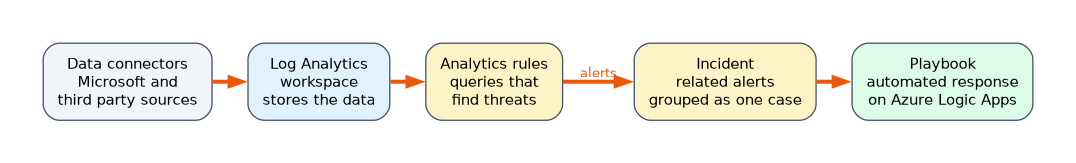 Automation rules and playbooks handle response. A playbook is a set of steps built on Azure Logic Apps, for example: when a high severity incident appears, post a message to a team channel, add the suspicious address to a block list and open a ticket. Automation reduces the load on analysts and speeds up the reaction.
Sentinel compared with other products
| Microsoft Sentinel | Defender for Cloud | Azure Monitor | |
|---|---|---|---|
| Main purpose | Detect and respond to threats across the whole organisation | Improve and protect the security of cloud workloads | Track performance and availability of resources |
| Data sources | Many, including other vendors | Cloud and server resources | Azure resources and applications |
| Gives | Incidents, hunting, playbooks | Recommendations, secure score, alerts | Metrics, logs, alerts |
A worked scenario
A company sends sign in logs from Microsoft Entra ID, firewall logs and alerts from Defender for Endpoint into Sentinel. An analytics rule notices that one account signed in from two countries within ten minutes and raises an alert. Sentinel groups this with a related malware alert from a laptop, and creates one incident. The analyst investigates the timeline, then a playbook disables the account and notifies the security team. Later the team hunts across the data for the same pattern in other accounts.
Setting up Sentinel in steps
- Create or choose a Log Analytics workspace.
- Add Microsoft Sentinel to the workspace.
- Connect data sources with data connectors.
- Turn on analytics rules from the built in templates.
- Build or adopt playbooks and automation rules for the common responses.
Sentinel is billed mainly for the amount of data ingested and stored, so teams choose carefully which logs are worth collecting.
A simple query
Analysts search the data with Kusto Query Language. This query counts failed sign ins by user.
SigninLogs
| where ResultType != 0
| summarize FailedSignIns = count() by UserPrincipalName
| order by FailedSignIns desc
A rule built on a query like this one could raise an alert when one account has an unusually high number of failures, which suggests a password guessing attack.
More features
- User and entity behaviour analytics learns what is normal for each account and device, and flags unusual activity.
- Threat intelligence lets Sentinel compare your data with lists of known malicious addresses and domains.
- Content hub offers ready made solutions, with connectors, rules and workbooks for particular products.
Sentinel and the Defender products
Alerts from the Defender products can flow into Sentinel, and Sentinel can add data from sources outside Microsoft. Defender XDR focuses on Microsoft's own products. Sentinel is the broader place to combine everything.
What to remember for the exam
- Sentinel is a cloud native SIEM and SOAR.
- It collects data from many sources with data connectors, into a Log Analytics workspace.
- Analytics rules detect threats and generate alerts, which are grouped into incidents.
- Hunting is proactive. Workbooks visualise data. Playbooks automate response.
- Playbooks are built on Azure Logic Apps.
"Collect and correlate data from many sources" or "SIEM and SOAR" always means Sentinel.
How the exam asks about this
- "Which service is a cloud native SIEM?" Microsoft Sentinel.
- "Automate the response to an incident." A playbook.
- "Search the data for threats before an alert exists." Hunting.
- "What happens when an analytics rule finds a match?" An alert is generated, which may become an incident.
Common mistakes
Confusing Sentinel with Defender for Cloud. Sentinel correlates data across the organisation. Defender for Cloud improves workload security.
Thinking Sentinel only reads Microsoft data. It also takes data from other vendors and clouds.
Mixing up alert and incident. An incident groups related alerts into one case.
Believing Sentinel blocks attacks directly. It detects and orchestrates. Blocking happens through playbooks and other tools.
Check yourself
What do the letters SIEM and SOAR stand for?
Security information and event management, and security orchestration, automation and response.
What is a playbook in Sentinel?
An automated set of response steps, built on Azure Logic Apps.
What groups related alerts into one case?
An incident.
Topic 4 of 5 in Capabilities of Microsoft Security Solutions
Test yourself on Capabilities of Microsoft Security Solutions
The full Microsoft SC-900 question bank has 503 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.