Capabilities of Microsoft Entra · Topic 4 of 4
Identity Governance, PIM and ID Protection
SC-900 identity governance: entitlement management, access reviews, lifecycle workflows, Privileged Identity Management and Entra ID Protection risk.
- 6 min
- Includes a diagram
- Entitlement management uses access packages, with approval and expiry.
- Access reviews prevent access creep.
- Lifecycle workflows automate joiner, mover and leaver tasks.
What it is
Giving access is not the end of the job. People change roles, projects end and accounts get attacked. Three groups of Entra features deal with this. Identity governance makes sure the right people keep the right access. Privileged Identity Management limits powerful roles to the time they are needed. ID Protection detects risky sign ins and risky users.
How it works
Microsoft Entra ID Governance
Governance tools automate the access lifecycle, from joining the company to leaving it.
- Entitlement management bundles the resources a person needs into access packages, such as groups, apps and sites. People request a package, an approver says yes or no, and the access can expire on its own.
- Access reviews ask owners or the users themselves to confirm regularly that access is still needed. Access that is not confirmed can be removed automatically.
- Lifecycle workflows run tasks at the key moments of an employee's time: joiner tasks such as creating accounts and sending welcome messages, mover tasks when someone changes teams, and leaver tasks such as removing group membership and disabling the account.
- Terms of use make users accept terms before they gain access.
These features need Microsoft Entra ID Governance, or an Entra ID P2 licence for some of them.
Access reviews in practice
A manager might set up a quarterly review of the members of a sensitive group. Each member's manager is asked "does this person still need access?" Those who are approved stay. Those denied, or not answered, are removed. This prevents access creep, where people collect permissions over the years that they no longer need.
Privileged Identity Management (PIM)
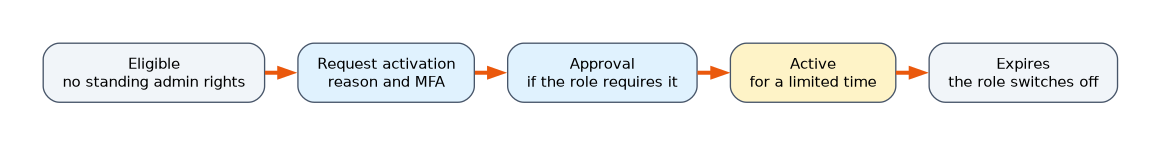 PIM manages, controls and monitors access to important roles. It needs Entra ID P2. Instead of making someone a permanent Global Administrator, PIM lets them be eligible for the role.
| Feature | What it does |
|---|---|
| Just in time access | The role is active only when the person needs it |
| Time bound access | The role switches off after a set number of hours |
| Approval | Activating a sensitive role can require someone to approve it |
| Justification and MFA | The user explains why and proves identity on activation |
| Alerts and audit history | Activations are recorded and unusual use raises alerts |
PIM follows least privilege and shrinks the time an attacker could use a stolen admin account.
Microsoft Entra ID Protection
ID Protection uses signals from Microsoft's large view of attacks to find identity risk. It needs Entra ID P2. It reports two kinds of risk.
- Sign in risk: how likely it is that a particular sign in is not by the real owner, for example from an unusual location or an anonymous network.
- User risk: how likely it is that an account is compromised, for example because its credentials appear in a leak.
It protects user accounts, including guests, and also workload identities such as application service principals. Risk can be fed into Conditional Access, so a policy can require MFA for a risky sign in or force a password change for a risky user. Administrators can see the risky users and sign ins in reports, and investigate.
Choosing the right feature
| The need | Feature |
|---|---|
| Give a new hire a bundle of resources with approval | Entitlement management |
| Check each quarter that group members still need access | Access reviews |
| Disable accounts and remove groups when someone leaves | Lifecycle workflows |
| Let an admin hold a role only while working | Privileged Identity Management |
| Detect a sign in from an impossible location | ID Protection |
A worked scenario
A software company has contractors who need access to several tools for three months. An access package bundles the tools, requires a manager's approval and expires after 90 days. Every quarter, an access review asks managers to confirm who still needs the admin group. Administrators hold the Global Administrator role through PIM and activate it for two hours when needed, with MFA. Meanwhile, ID Protection flags a sign in from an anonymous network, and a Conditional Access policy responds by requiring MFA.
Activating a role in PIM
- An administrator who is eligible for the role opens Privileged Identity Management.
- They choose to activate the role and give a reason.
- They prove their identity with multifactor authentication.
- If the role needs approval, an approver reviews and agrees.
- The role becomes active for a limited time, then switches off by itself.
Between activations, the person holds no standing admin rights. A stolen account is therefore far less useful to an attacker.
Risk levels and automatic responses
ID Protection rates risk as low, medium or high. Conditional Access can use these ratings.
| Policy type | Typical response |
|---|---|
| Sign in risk policy | Require multifactor authentication when a sign in looks risky |
| User risk policy | Require a secure password change when an account looks compromised |
Examples of risk detections are sign ins from anonymous networks, travel between distant places in an impossible time, and credentials found in a leak.
Licences at a glance
| Feature | Licence |
|---|---|
| Conditional Access | Entra ID P1 |
| Identity Protection | Entra ID P2 |
| Privileged Identity Management | Entra ID P2 |
| Access packages, lifecycle workflows | Entra ID Governance |
| Access reviews | Entra ID P2 or Entra ID Governance |
What to remember for the exam
- Entitlement management uses access packages, with approval and expiry.
- Access reviews prevent access creep.
- Lifecycle workflows automate joiner, mover and leaver tasks.
- PIM provides just in time, time bound, approved access to privileged roles.
- ID Protection detects risky users and risky sign ins, and feeds Conditional Access.
"Eligible" and "activate" point to PIM. "Risky" points to ID Protection. "Review" points to access reviews.
How the exam asks about this
- "Admins should have the role only when they need it." Privileged Identity Management.
- "Regularly confirm that people still need access." Access reviews.
- "Which feature detects a leaked credential?" ID Protection.
- "A task that disables the account of a leaver." A lifecycle workflow.
Common mistakes
Confusing PIM with Conditional Access. PIM controls when a role is held. Conditional Access controls sign in conditions.
Thinking access reviews only add access. Their purpose is to remove access that is no longer needed.
Assuming ID Protection only covers users. It also covers workload identities.
Forgetting licences. PIM and ID Protection need P2, and governance features need ID Governance or P2.
Check yourself
Which feature gives a person an eligible role that is active only for a limited time?
Privileged Identity Management.
What are access reviews used for?
Regularly confirming that people still need their access, and removing it if not.
Which two risks does ID Protection report?
Sign in risk and user risk.
Topic 4 of 4 in Capabilities of Microsoft Entra
Test yourself on Capabilities of Microsoft Entra
The full Microsoft SC-900 question bank has 503 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.