Manage Identity, Access, and Governance · Topic 1 of 3
Securing Access with Microsoft Entra ID
SC-500 identity: Privileged Identity Management, Conditional Access, MFA and passwordless methods, app registrations, consent settings and managed identities.
- 4 min
- Includes a diagram
- PIM: eligible versus active assignments, activation requirements, access reviews.
- Conditional Access: assignments, conditions, grant and session controls; report-only mode; exclude break-glass accounts.
- Phishing-resistant methods: passkeys (FIDO2), Windows Hello for Business, certificate-based authentication (multifactor).
What it is
Microsoft Entra ID is the identity service for Azure and Microsoft 365. SC-500 tests how to use it to secure access: grant powerful roles only when needed with Privileged Identity Management (PIM), apply Conditional Access policies, require strong authentication methods, control applications and consent, and give Azure resources managed identities instead of secrets.
How it works
Privileged Identity Management
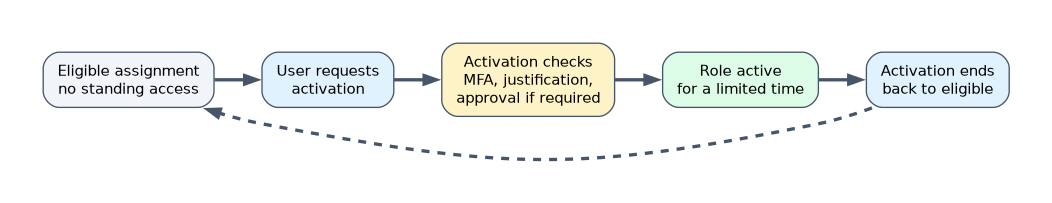
| Feature | Purpose |
|---|---|
| Eligible assignment | The user can activate the role when needed instead of holding it permanently |
| Active assignment | The role is always active |
| Activation settings | Require MFA (or a Conditional Access authentication context), a justification, ticket information or approval to activate; set a maximum activation duration of 1 to 24 hours |
| Access reviews | Periodically confirm that people still need their roles |
| Alerts and audit history | Show risky configurations and who activated what |
PIM works for Microsoft Entra roles, Azure resource roles and PIM for Groups.
Conditional Access
A Conditional Access policy says: if these conditions apply (assignments), then enforce these controls.
| Part | Examples |
|---|---|
| Users and workload identities | All users, a group, admin roles; exclude break-glass accounts |
| Target resources | All cloud apps or specific apps |
| Conditions | Sign-in risk, user risk, device platform, locations, client apps |
| Grant controls | Block, or require MFA, authentication strength, a compliant or hybrid-joined device |
| Session controls | Sign-in frequency, app enforced restrictions |
Use report-only mode to test a policy's impact before enforcing it. Always exclude emergency access accounts so you cannot lock everyone out.
Authentication methods
- Enable methods in the Authentication methods policy, for all users or for groups.
- Phishing-resistant methods include passkeys (FIDO2), Windows Hello for Business and certificate-based authentication configured as multifactor.
- Authentication strengths in Conditional Access require specific method combinations. The built-in strengths are multifactor authentication, passwordless MFA and phishing-resistant MFA; you can also create custom strengths.
- Microsoft Authenticator supports push notifications with number matching and passwordless phone sign-in.
Identity for applications
| Object | Meaning |
|---|---|
| App registration | The application's definition in its home tenant: client ID, redirect URIs, credentials, API permissions |
| Enterprise application (service principal) | The app's instance in a tenant, where you assign users, configure single sign-on and review consent |
| Credentials | Prefer certificates or federated credentials over client secrets |
OAuth permissions and consent
- Delegated permissions let an app act as a signed-in user; application permissions let it act as itself.
- User consent settings decide whether users can consent to apps, for example only to apps from verified publishers (or registered in your tenant) and only for permissions you classify as low impact. Changing the setting doesn't remove existing grants.
- The admin consent workflow lets users request apps that need an administrator's approval.
- Review and revoke excessive grants in the enterprise application's permissions.
Managed identities
| Type | Lifecycle |
|---|---|
| System-assigned | Created with a resource and deleted with it; used by that resource only |
| User-assigned | A standalone resource that can be attached to several resources |
Grant the identity an RBAC role on the target, such as Key Vault Secrets User, and the code uses it with no secret to store or rotate.
"Admins should have no standing access" points to PIM eligible assignments. "Require phishing-resistant MFA for admins" points to a Conditional Access policy with an authentication strength.
How the exam asks about this
- "Global Administrator should be activated only when needed, with approval." PIM eligible assignment with approval.
- "Test a new Conditional Access policy without blocking anyone." Report-only mode.
- "Stop users consenting to unverified apps." Configure user consent settings and the admin consent workflow.
What to remember for the exam
- PIM: eligible versus active assignments, activation requirements, access reviews.
- Conditional Access: assignments, conditions, grant and session controls; report-only mode; exclude break-glass accounts.
- Phishing-resistant methods: passkeys (FIDO2), Windows Hello for Business, certificate-based authentication (multifactor).
- App registration defines the app; enterprise application is its instance in a tenant.
- Managed identities: system-assigned per resource, user-assigned shareable.
Do not apply a block policy to all users without excluding emergency access accounts.
Common mistakes
Giving admins permanent roles. Use PIM eligibility.
Using client secrets where a managed identity works. Managed identities need no secret.
Letting users consent to any app. Restrict consent and use the admin consent workflow.
Check yourself
What is the difference between an eligible and an active PIM assignment?
An eligible assignment must be activated before use; an active assignment is always in effect.
How can you see a Conditional Access policy's effect before enforcing it?
Turn it on in report-only mode.
When should you choose a user-assigned managed identity?
When the same identity must be shared by several resources or must outlive a single resource.
Topic 1 of 3 in Manage Identity, Access, and Governance
Test yourself on Manage Identity, Access, and Governance
The full Microsoft SC-500 question bank has 650 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.