Plan and Implement Workload Identities · Topic 2 of 4
Enterprise Applications and Application Proxy
SC-300 enterprise apps: SAML single sign on, assignment, app roles, user and admin consent, app collections and Application Proxy for on premises apps.
- 6 min
- Includes a diagram
- SAML gallery setup: identifier and reply URL in Basic SAML Configuration, and give the vendor the federation metadata.
- Assignment required controls who can sign in. Group assignment needs P1.
- Consent settings: none, verified publishers for selected permissions, or all. The admin consent workflow handles requests.
What it is
An enterprise application is an application that your tenant uses, with its own settings for sign in, access and consent. It is the service principal that represents the app in your tenant. You can add software as a service apps from the gallery, apps you build, and on premises web apps published through Application Proxy.
Managing enterprise applications means setting up single sign on, deciding who can use the app, controlling consent, and organising apps for users.
How it works
Single sign on methods
| Method | How it works |
|---|---|
| SAML | Entra issues a signed assertion to the app, the most common for enterprise SaaS |
| OpenID Connect and OAuth | Modern token based sign in, common for apps that register themselves |
| Password based | Entra stores and fills the credentials for apps with a sign in page but no federation |
| Linked | A shortcut to a sign in page, without Entra handling the sign in |
| Disabled | No single sign on |
Configuring SAML for a gallery app
Adding a gallery app and enabling SAML involves the following.
- In Basic SAML Configuration, enter the vendor's Identifier (Entity ID) and the Reply URL, also called the assertion consumer service URL. A sign on URL and relay state are optional.
- Review Attributes and claims, which decide what information goes in the token, such as email or group claims.
- Take the SAML signing certificate details and the Federation Metadata XML, and give them to the vendor so it trusts Entra ID.
- Assign users and groups, then test the sign in.
The vendor's identifier and reply URL go into Basic SAML Configuration. The federation metadata goes to the vendor. Creating an app registration is not part of configuring a gallery SAML app.
Controlling who can use the app
- Assignment required? When set to Yes, only users and groups assigned to the app can sign in. When No, any user in the tenant can.
- Users and groups. Assign a user or group, and for apps that define app roles, choose the role. Assigning groups to an application needs Entra ID P1.
- Visible to users. Decides whether the app appears in My Apps.
- Owners can manage the app without being administrators.
Two administrator roles manage enterprise apps. The Cloud Application Administrator manages them but cannot manage Application Proxy settings. The Application Administrator can also manage Application Proxy.
User consent and admin consent
When an application asks for permission to access data, a user or an administrator may need to consent. In Consent and permissions you choose the policy.
| Setting | Meaning |
|---|---|
| Do not allow user consent | Only administrators can consent |
| Allow user consent for apps from verified publishers, for selected permissions | Users may consent to low risk permissions that you classify |
| Allow user consent for all apps | The least restrictive, and not recommended |
- An admin consent workflow lets users request consent when they cannot give it, and designated reviewers approve or deny.
- Grant admin consent for the tenant approves the permissions for everyone.
- Permission classifications mark permissions as low impact, so users may consent to them under the middle setting.
- Users can register applications, in User settings, is a different setting. It controls whether ordinary users may create app registrations. Turn it off to stop that.
Application collections
In My Apps, users see their applications. An administrator can create collections that group apps, for example Finance or HR, so users find them easily. Collections can be assigned to specific users and groups.
Microsoft Entra Application Proxy
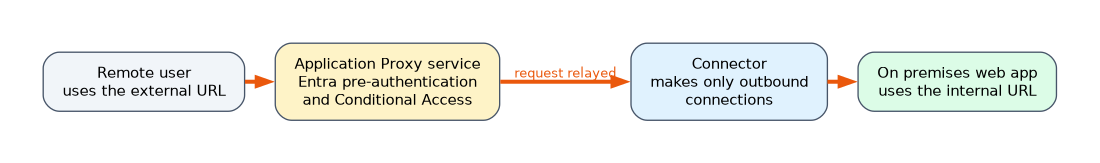 Application Proxy publishes an on premises web application to remote users without a VPN or a firewall opening for inbound connections.
- A connector is a small agent installed on a Windows server in the corporate network. It makes only outbound connections, over ports 80 and 443, to the Application Proxy service.
- Connectors are placed in connector groups to serve different apps, sites or regions.
- You set an internal URL, which the connector uses, and an external URL, which users use.
- Pre-authentication can be Microsoft Entra ID, where users sign in first and Conditional Access applies, or Passthrough, where the app handles it.
- Single sign on to the on premises app can use Kerberos constrained delegation for integrated Windows authentication, header based methods or password based.
Application Proxy needs Microsoft Entra ID P1. It suits apps such as internal portals and SharePoint on premises. It is not needed for a SaaS app that supports SAML.
Automatic provisioning
Many gallery apps support provisioning, using the SCIM standard, so Entra creates, updates and removes users in the app automatically. The Provisioning logs show what happened.
Choosing the approach
| The need | Choice |
|---|---|
| A SAML SaaS app from the gallery | Basic SAML Configuration, metadata to the vendor |
| Only some people may use an app | Assignment required, assign groups |
| Stop users approving app permissions themselves | Do not allow user consent, enable the admin consent workflow |
| Reach an on premises web app with no VPN | Application Proxy |
| Group apps by department in My Apps | Application collections |
A worked scenario
A company adds a SAML gallery app for expenses. The admin enters the vendor's identifier and reply URL in Basic SAML Configuration, downloads the federation metadata for the vendor, sets Assignment required to Yes and assigns the Finance group. Under consent settings, user consent is limited to verified publishers for low risk permissions, and an admin consent workflow lets users ask for more. An internal HR portal is published with Application Proxy, using two connectors in a connector group and Entra pre-authentication, so Conditional Access applies. Both apps are placed in an HR collection in My Apps.
What to remember for the exam
- SAML gallery setup: identifier and reply URL in Basic SAML Configuration, and give the vendor the federation metadata.
- Assignment required controls who can sign in. Group assignment needs P1.
- Consent settings: none, verified publishers for selected permissions, or all. The admin consent workflow handles requests.
- Application Proxy connectors only connect outbound and sit in connector groups. It needs P1.
- Application Administrator can manage Application Proxy. Cloud Application Administrator cannot.
Stopping ordinary users from creating app registrations is the "Users can register applications" user setting, not a consent setting.
How the exam asks about this
- "Which two actions configure a gallery SAML app?" Enter the vendor's identifier and reply URL, and give the vendor the federation metadata.
- "Stop users consenting to apps themselves." Do not allow user consent, with an admin consent workflow.
- "Publish an on premises app without a VPN." Application Proxy.
- "Which role manages Application Proxy?" Application Administrator.
Common mistakes
Creating an app registration for a gallery SAML app. It is not needed.
Opening inbound firewall ports for the connector. It connects outbound only.
Mixing up the consent setting and the register applications setting. They control different things.
Forgetting to assign users when assignment is required. Nobody can sign in.
Check yourself
Where do you enter the vendor's entity ID and reply URL for a SAML app?
In the Basic SAML Configuration section of the enterprise application's single sign on settings.
What does Application Proxy let you do?
Publish on premises web apps to remote users without a VPN, through outbound connectors.
Which setting decides whether only assigned users can sign in?
Assignment required.
Topic 2 of 4 in Plan and Implement Workload Identities
Test yourself on Plan and Implement Workload Identities
The full Microsoft SC-300 question bank has 650 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.