Plan and Automate Identity Governance · Topic 3 of 4
Privileged Identity Management
SC-300 PIM: eligible and active roles, activation settings, approval, PIM for Entra roles, Azure resources and Groups, and emergency access accounts.
- 6 min
- Includes a diagram
- Eligible means can activate. Active means holds the role now. Activation can be time limited from 1 to 24 hours.
- Activation can require MFA, justification, ticket information and approval.
- PIM covers Entra roles, Azure resources and Groups. Role assignable groups cannot be dynamic.
What it is
Powerful roles are a prime target for attackers, so they should not be held all the time. Microsoft Entra Privileged Identity Management (PIM) provides just in time, time bound and approved access to privileged roles. A person is eligible for a role and activates it only when they need it, for a limited time, often with MFA and a reason.
PIM needs Microsoft Entra ID Governance, or Entra ID P2. It supports Microsoft Entra roles, Azure resource roles and Groups.
How it works
Eligible and active assignments
| Assignment | Meaning |
|---|---|
| Eligible | The person can activate the role but does not have its permissions yet |
| Active | The person holds the role now, either permanently or until a set end time |
You can make assignments time bound, with start and end dates, for example eligible for three months. Active assignments can also be limited, and PIM can require MFA and a justification even to make an active assignment.
Role settings
Each role has settings that control activation.
| Setting | Effect |
|---|---|
| Activation maximum duration | How long an activation lasts, from 1 to 24 hours |
| Require MFA on activation | The user proves identity again |
| Require justification | The user explains why |
| Require ticket information | A ticket number must be given |
| Require approval | One or more approvers must approve the activation |
| Notifications | Email to administrators or the role holders when activated |
| Authentication context | Require a Conditional Access authentication context on activation |
| Assignment settings | Whether permanent eligible or active assignments are allowed, and when eligible assignments expire |
The three PIM scopes
| Scope | What you manage |
|---|---|
| Microsoft Entra roles | Directory roles such as Global Administrator or Exchange Administrator |
| Azure resources | Roles on management groups, subscriptions, resource groups and resources |
| Groups | Just in time membership or ownership of a group, including role assignable groups, so a person can activate several roles together |
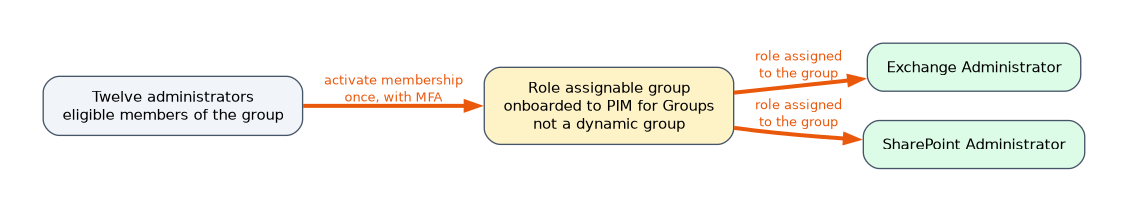
PIM for Groups helps when several roles should be activated in one request. Roles can only be assigned to a role assignable group, and a dynamic group cannot be role assignable. So create a role assignable group, give both roles to it, onboard the group to PIM, and make each administrator an eligible member of the group. They then activate their membership once, and receive both roles.
The request and approval process
When a role needs approval:
- The user requests activation, giving a justification and, if required, a ticket number.
- The approvers are notified and review the request in PIM.
- If approved, the role becomes active for the duration, and the user is notified.
- If it is not approved in time, the request expires.
Audit and reports
PIM keeps an audit history of every assignment and activation, so you can see who held which role and when, and why. Alerts warn about risky situations, such as too many Global Administrators or roles that are never used. Access reviews in PIM re certify who still needs eligible or active roles.
Emergency access accounts
An emergency access account, or break glass account, is used when normal administrators cannot sign in, for example if Conditional Access is misconfigured or MFA is unavailable. Follow these rules.
- Create two or more accounts.
- Make them cloud only, using the
.onmicrosoft.comdomain, and not synchronised from on premises. - Give them a permanent Global Administrator assignment, outside PIM, so they never depend on activation.
- Exclude them from Conditional Access policies that block or restrict sign in, so a policy mistake cannot lock them out.
- Protect them with a phishing resistant method such as a FIDO2 key or certificate, and store the credentials safely.
- Monitor their sign ins and raise an alert whenever one is used.
Choosing the setting
| The need | Setting |
|---|---|
| An admin should hold a role only when needed | Eligible assignment, with activation |
| A sensitive role needs a second person | Require approval |
| A stolen admin session should not last | A short activation maximum duration |
| Activate two roles in one request | PIM for Groups with a role assignable group |
| Lock out protection if a policy goes wrong | Emergency access accounts |
A worked scenario
A company removes standing Global Administrator rights. Administrators are eligible for the role, activate it for up to two hours with MFA and a justification, and Global Administrator activations also need approval. Twelve administrators need Exchange Administrator and SharePoint Administrator together, so a role assignable group is created, both roles are assigned to it, and each person is an eligible member through PIM for Groups. The company keeps two cloud only emergency accounts with FIDO2 keys, excluded from blocking policies, and an alert fires whenever one is used.
What to remember for the exam
- Eligible means can activate. Active means holds the role now. Activation can be time limited from 1 to 24 hours.
- Activation can require MFA, justification, ticket information and approval.
- PIM covers Entra roles, Azure resources and Groups. Role assignable groups cannot be dynamic.
- Emergency accounts: two or more, cloud only, permanent Global Administrator, excluded from Conditional Access blocks, phishing resistant sign in, monitored.
- PIM needs Entra ID Governance or P2.
"Activate two roles together, as eligible" is a role assignable group onboarded to PIM for Groups.
How the exam asks about this
- "Admins should hold the role only while working." Eligible assignments with activation.
- "Twelve admins in a dynamic group need two roles, as eligible." Create a role assignable group, assign the roles, onboard it to PIM and make members eligible.
- "Where do you see who activated a role and why?" The PIM audit history.
- "Emergency access accounts and Conditional Access." Exclude them from policies that could block them.
Common mistakes
Assigning roles to a dynamic group. Only role assignable groups can hold roles, and they cannot be dynamic.
Putting emergency accounts under PIM. They should be permanent so they work in an emergency.
Leaving long activation durations. A short duration limits exposure.
Having only one emergency account. Two or more are recommended.
Check yourself
What is the difference between eligible and active?
Eligible means the person can activate the role when needed. Active means they hold its permissions now.
Why create a role assignable group for PIM?
Roles can only be assigned to a role assignable group, so the group can hold several roles activated together.
Which Conditional Access rule applies to emergency access accounts?
They are excluded from policies that block or restrict sign in.
Topic 3 of 4 in Plan and Automate Identity Governance
Test yourself on Plan and Automate Identity Governance
The full Microsoft SC-300 question bank has 650 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.