Digital Forensics · Topic 2 of 11
Windows Artifacts, Event Logs, TSK and Timelines
Windows file analysis, metadata, ShellBags, LNK files, Jump Lists, event logs, Sleuth Kit commands and timeline analysis with key event IDs, for CHFI v11.
- 6 min
- Includes a diagram
- Event logs are
.evtxinSystem32\winevt\Logs. 4624 success, 4625 failure, 1102 log cleared. - ShellBags are in NTUSER.DAT and UsrClass.dat. LNK files are in the Recent folder.
- Jump Lists have AutomaticDestinations and CustomDestinations.
What it is
Windows records a great deal of user and system activity as a side effect of normal use. These artifacts show what ran, which files and folders were opened, who logged on and when.
This page covers the main Windows artifact locations, file metadata, ShellBags, LNK files and Jump Lists, event logs, The Sleuth Kit and timeline building. The exam asks where an artifact lives and what it shows.
How it works
Windows file analysis
| Artifact | Location | Shows |
|---|---|---|
| Registry hives | C:\Windows\System32\config (SAM, SYSTEM, SOFTWARE, SECURITY, DEFAULT) | Accounts, devices, installed software |
| User hives | NTUSER.DAT and AppData\Local\Microsoft\Windows\UsrClass.dat in the profile | Per user activity, ShellBags, UserAssist |
| Prefetch | C:\Windows\Prefetch\*.pf | Program name, run count, last run times |
| Recent items | AppData\Roaming\Microsoft\Windows\Recent | LNK files for opened documents |
| Pagefile and hibernation | pagefile.sys, hiberfil.sys | Memory remnants |
| Thumbnail cache | AppData\Local\Microsoft\Windows\Explorer | Thumbnails of images that may have been deleted |
| Amcache and ShimCache | Amcache.hve; AppCompatCache in the SYSTEM hive | Evidence that an executable existed on the system and, in some cases, ran |
UserAssist, in NTUSER.DAT, stores program launch counts and times with ROT13 encoded names. Prefetch is often disabled on servers, so its absence needs context.
Metadata investigation
Metadata is data about data. It often outlives the content and can tie a file to a person, device or time.
| Source | Typical metadata |
|---|---|
| NTFS timestamps | Created, modified, accessed, MFT entry changed (MACB) |
| Office documents | Author, last saved by, company, created and revised times, template |
| JPEG (EXIF) | Camera make and model, date taken, GPS coordinates, software |
| Author, producer, creation and modification dates |
ExifTool reads metadata from many formats, for example exiftool photo.jpg. A file copied to another NTFS volume keeps its modified time but gets a new created time, which is a classic clue to copying.
Windows ShellBags
ShellBags record how a user views folders in Explorer: size, position and view settings. They show that a folder was viewed in Explorer, even after the folder, USB drive or network share is gone.
They live in NTUSER.DAT and UsrClass.dat under the Shell\BagMRU and Shell\Bags keys. Parse them with ShellBags Explorer or SBECmd.
Analyze LNK files and Jump Lists
Windows creates a shortcut (.lnk) in the Recent folder when a user opens a file. The LNK holds the target path, the target's MAC times and size, the volume label and serial number, the drive type, and information about the host system.
Jump Lists show recently and frequently used items per application. AutomaticDestinations holds .automaticDestinations-ms files made by the system, and CustomDestinations holds .customDestinations-ms files made by applications. Tools include LECmd, JLECmd and Jump List Explorer.
Event logs
Modern logs are .evtx files in C:\Windows\System32\winevt\Logs. The three classic logs are Security, System and Application.
| Event ID | Log | Meaning |
|---|---|---|
| 4624 | Security | Successful logon |
| 4625 | Security | Failed logon |
| 4634 | Security | Logoff |
| 4648 | Security | Logon with explicit credentials |
| 4672 | Security | Special privileges assigned |
| 4688 | Security | Process created (if auditing is on) |
| 4720 | Security | User account created |
| 4698 | Security | Scheduled task created |
| 1102 | Security | Audit log cleared |
| 104 | System | A log was cleared |
| 7045 | System | Service installed |
Logon type 2 is interactive, 3 is network, and 10 is remote interactive such as RDP. Tools include Event Viewer, Log Parser and EvtxECmd.
File system analysis using The Sleuth Kit (TSK)
TSK is a command line library and toolset that reads file systems without mounting them, so it does not alter the evidence. Autopsy is its graphical front end.
| Command | Purpose |
|---|---|
mmls | Show the partition layout of an image |
fsstat | File system details |
fls | List files and directories, including deleted ones (-r recursive, -d deleted only) |
istat | Metadata of one inode or MFT entry |
icat | Output a file's content by inode number |
blkls | Output unallocated blocks, for carving |
mactime | Build a timeline from a body file |
Typical use is mmls image.dd to find the partition start sector, then fls -r -o 2048 image.dd to list files at that offset.
Perform timeline analysis
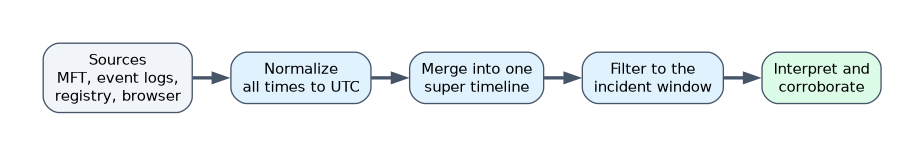 A timeline places events from many sources in one time ordered view. Sources include file system times, event logs, registry keys, browser history and LNK files.
Two common paths are the TSK body file route and Plaso. fls -r -m C: -o 2048 image.dd > body.txt creates a body file, and mactime -b body.txt -d > timeline.csv turns it into a CSV. Plaso (log2timeline with psort) builds a "super timeline" from many artifact types. Check time zones and clock skew before drawing conclusions.
A worked example
A company suspects data theft before an employee resigned. The investigator finds LNK files for 30 documents opened from drive E:, all with the same volume serial number. ShellBags show the user browsed folder E:\Client Lists, and USB records in the SYSTEM hive show a storage device connected that evening.
Event ID 4624 with logon type 2 is consistent with the user being at the keyboard. A timeline places the USB connection, the file opens and the logoff within one evening.
How the exam asks about this
- "Which Windows artifact shows a folder was browsed even after it was deleted?" -> ShellBags.
- "Which event ID records a failed logon?" -> 4625.
- "Which TSK command lists files, including deleted ones?" ->
fls.
What to remember for the exam
- Event logs are
.evtxinSystem32\winevt\Logs. 4624 success, 4625 failure, 1102 log cleared. - ShellBags are in NTUSER.DAT and UsrClass.dat. LNK files are in the Recent folder.
- Jump Lists have AutomaticDestinations and CustomDestinations.
mmlsshows partitions,flslists files,icatextracts content,mactimebuilds timelines.- Timelines merge many sources, so time zone and clock accuracy matter.
Timestamps change in predictable ways when files are copied, moved or opened. Never state a "created" or "accessed" time as the time of user action without checking how the time was set.
Common mistakes
Mixing up ShellBags and LNK files. ShellBags record folders viewed. LNK files record files opened.
Treating Prefetch as always present. It may be disabled, so a missing prefetch file does not prove a program never ran.
Reading one event in isolation. A single 4624 means little. Read it with the logon type, source address and surrounding events.
Check yourself
Which Jump List folder holds lists created automatically by the system?
AutomaticDestinations.What does Event ID 1102 indicate?
The Security audit log was cleared.
Why use TSK instead of mounting an image and browsing it?
TSK reads the file system directly and read only, so evidence is not modified and deleted entries can be listed.
Topic 2 of 11 in Digital Forensics
Test yourself on Digital Forensics
The full EC-Council 312-49 question bank has 900 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.