Security Operations · Topic 10 of 14
Identity Lifecycle, Federation and Account Types
Security+ identity management: provisioning, permissions, identity proofing, federation, SSO with SAML, LDAP and OAuth, and user and privileged accounts.
- 5 min
- Includes a diagram
- Provisioning creates accounts. Deprovisioning removes access as soon as it is no longer needed.
- Permissions have implications, and privilege creep builds up without reviews.
- Identity proofing verifies a person before an account is issued.
What it is
Identity and access management (IAM) is the set of processes and tools that decide who a user is and what that user may do. The identity lifecycle follows an account from creation to removal.
Federation and single sign-on (SSO) let one trusted identity work across many systems. This page covers the lifecycle, permissions, identity proofing, federation, the SSO protocols and the account types.
How it works
Provisioning and deprovisioning user accounts
Provisioning creates an account and grants the access the role needs. Deprovisioning disables or removes accounts and access when a person leaves or no longer needs them.
Delays in deprovisioning leave live accounts for people who have gone, which is a common source of insider incidents and account takeover. Automation linked to human resources systems shortens the gap.
Permissions assignments and implications
Permissions should follow the person's role and be reviewed when the role changes. Each permission has implications: write access to a share lets a user change or delete everything in it, and membership in an administrators group grants rights on every system the group controls.
Over time, people collect more access than they need, a problem known as privilege creep. Assign permissions to groups rather than to individuals, and remove old rights when someone moves role.
Identity proofing
Identity proofing confirms that a person is who they claim before an account or credential is issued. Examples include checking a government ID document, confirming details with human resources or verifying a person in person. Weak proofing lets an attacker obtain a real account in someone else's name.
Federation and single sign-on
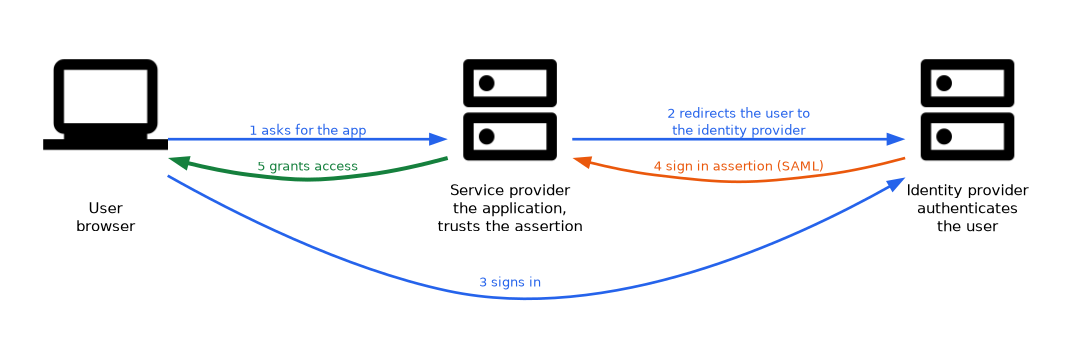 SSO lets a user sign in once and reach several applications. Federation extends trust across organizations or domains, so a user from one organization can sign in to another's service using their home identity.
| Protocol | Purpose |
|---|---|
| Security Assertion Markup Language (SAML) | An Extensible Markup Language (XML) based standard that passes sign in assertions from an identity provider to a service provider |
| Lightweight Directory Access Protocol (LDAP) | A protocol to query and manage a directory of users and groups, which many applications use to check credentials |
| Open Authorization (OAuth) | A framework for delegating access, where an application gets a token to act for a user without learning the password |
The identity provider (IdP) authenticates the user. The service provider (SP) trusts the assertion and grants access.
OAuth is about authorization, not login. A common case is a calendar tool asking for limited access to your email account with a token you approve. LDAP should be protected with Transport Layer Security (TLS), known as LDAPS, so credentials are not sent in clear text.
| Benefit of SSO | Risk of SSO |
|---|---|
| Fewer passwords to remember | A compromised SSO account opens many systems |
| Central control and logging | The identity provider becomes a critical target |
| Easier deprovisioning | Outage of the provider can block access |
Account types
| Type | Description | Key control |
|---|---|---|
| User | A normal account for one person's daily work | Least privilege, MFA |
| Privileged: global | Administrative rights across a whole domain, directory or cloud tenant | Very few holders, MFA, monitoring, just-in-time use |
| Privileged: local | Administrative rights on one machine only | Unique password per machine, no shared reuse |
| Service | Used by an application or process, not a person | No interactive sign in, minimum rights, managed credentials |
| Third-party | Used by a vendor, contractor or partner | Time limits, narrow scope, review and remove when work ends |
| Emergency access | A break glass account for use when normal sign in fails | Stored securely, monitored, alert on every use |
Admins should use a normal user account for email and browsing, and a separate privileged account only for administration. A local administrator password reused on every machine lets one stolen password open them all.
How the exam asks about this
- "An app needs access to a user's files without being given the password." -> OAuth.
- "Staff sign in once with the company identity provider to reach a partner's web portal." -> Federation using SAML.
- "Admins need a way in when the identity provider is down." -> An emergency access account, monitored and tightly stored.
What to remember for the exam
- Provisioning creates accounts. Deprovisioning removes access as soon as it is no longer needed.
- Permissions have implications, and privilege creep builds up without reviews.
- Identity proofing verifies a person before an account is issued.
- Federation extends trust between organizations. SSO is one sign in for many apps.
- SAML passes assertions from IdP to SP. LDAP queries a directory. OAuth delegates access with tokens.
- Privileged accounts are global or local, and both need extra control.
- Service, third-party and emergency access accounts each need their own limits and monitoring.
When the question asks which protocol lets an app access your data without your password, the answer is OAuth. When it asks for web sign in across organizations, think SAML.
Common mistakes
Calling OAuth an authentication protocol. It authorizes access through tokens.
Slow deprovisioning. An account that stays active after someone leaves is a risk.
Confusing federation with SSO. SSO is one sign in for many applications, while federation extends trust between organizations.
Letting service accounts sign in interactively. They should run only the process they serve.
Leaving vendor accounts open after the contract. Third-party accounts need an end date.
Disable accounts immediately when employment ends. Do not wait for a batch process.
Check yourself
What is privilege creep?
The gradual build up of permissions beyond what a person's current role needs.
Which protocol delegates access with a token and does not share the user's password?
OAuth.
What is an emergency access account?
A break glass account used only when normal sign in fails, stored securely and monitored on every use.
Topic 10 of 14 in Security Operations
Test yourself on Security Operations
The full CompTIA Security+ SY0-801 question bank has 998 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by CompTIA. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.