AI-assisted Security · Topic 1 of 4
AI-enabled Security Tools and MCP Servers
Compare AI-enabled security tools: IDE, browser and CLI plug-ins, chatbots, personal assistants and Model Context Protocol servers, with risks of each.
- 6 min
- Includes a diagram
- IDE plug-ins help with code, browser plug-ins with web content, CLI plug-ins with commands and scripts.
- Chatbots and personal assistants answer and draft; personal assistants often have broad access to email and files.
- MCP connects AI applications to tools and data through servers that offer tools, resources and prompts.
What it is
Tools enabled by artificial intelligence (AI) put a model where security people already work: in the code editor, the browser, the terminal or a chat window. They answer questions, write drafts and, increasingly, take actions through connected systems.
Each tool type has a different reach. The exam asks which tool suits a task and what risk it introduces, because a tool that can read code, browse pages or run commands also widens the attack surface.
How it works
Tool types
| Tool | Where it runs | Security tasks | Main risks |
|---|---|---|---|
| Integrated development environment (IDE) plug-ins | Inside the code editor | Suggest secure code, explain flaws, write tests, flag risky patterns as you type | Insecure or invented code suggestions, source code sent to an outside service |
| Browser plug-ins | In the web browser | Summarise pages and reports, explain phishing emails, check links | Reading every page the user visits, including sensitive ones; indirect prompt injection from web content |
| Command-line interface (CLI) plug-ins | In the terminal | Turn plain language into commands, explain output, draft scripts | Running a suggested command without understanding it, destructive commands |
| Chatbots | Web or app chat | Answer policy questions, guide users through reporting, explain alerts | Data pasted into unapproved services, hallucinated answers |
| Personal assistants | Across email, calendar and documents | Triage inbox, prepare briefings, draft responses | Broad access to personal data, actions taken on the user's behalf |
| Model Context Protocol (MCP) server | A service that connects an AI application to tools and data | Give an assistant controlled access to a ticketing system, log store or scanner | Over-permissioned servers, malicious or tampered servers, injection through tool output |
Model Context Protocol
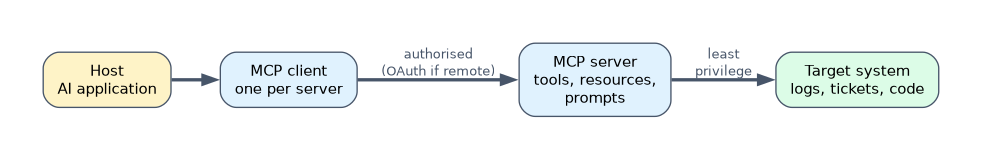 MCP is an open protocol, introduced by Anthropic in 2024, that standardises how AI applications connect to external tools and data. Instead of building a custom connector for every pair of assistant and system, a system is wrapped once in an MCP server and any compatible AI application can use it.
The AI application, the host, runs an MCP client for each server it connects to. A server can offer tools (actions the model can call), resources (data the model can read) and prompts (reusable templates).
Servers can run locally on the user's machine or remotely over the network. Remote servers should require proper authorisation, and the protocol defines an authorisation approach based on Open Authorization (OAuth) for that purpose.
Securing MCP servers
| Risk | Control |
|---|---|
| Server from an untrusted source | Use an approved list of vetted servers; review code and publisher |
| Server holds broad credentials | Least privilege: scope its credentials to the tasks, read-only where possible |
| Tool descriptions or tool output contain hidden instructions | Treat descriptions and output as untrusted input; review tool definitions; alert if they change after approval |
| Model calls a destructive tool | Require user confirmation for high-impact tools; log every call |
| Local server runs with the user's full rights | Run it in a container or sandbox with limited file and network access |
Choosing a tool for the task
The deciding factors are where the work happens, what data the tool will see and whether it only advises or also acts. An advisory tool needs data controls; an acting tool needs data controls plus least privilege and approval steps.
- Code review while writing: an IDE plug-in from an approved provider, with secure coding rules.
- Explaining a suspicious email or web page: a browser plug-in or approved chatbot, using a copy rather than live credentials.
- Building a one-off log query or script: a CLI plug-in, with the analyst reading the command before running it.
- Letting an assistant open and update tickets: an MCP server that exposes only the ticket tools needed, with logging.
A worked example
A security operations centre (SOC) wants its approved assistant to look up alerts in the security information and event management (SIEM) system and add notes to incident tickets. Previously analysts copied alert text by hand into a chatbot.
The team deploys an internal MCP server with two tools: a read-only alert search and a ticket comment tool. It runs under a dedicated account, every call is logged, and adding comments asks the analyst to confirm.
How the exam asks about this
- "A team wants several AI assistants to use the same ticketing system through one standard interface without writing a connector for each. Which of the following should it deploy?" An MCP server for the ticketing system.
- "Developers want inline warnings about insecure code patterns while they type. Which of the following tools is most appropriate?" An AI-enabled IDE plug-in.
- "An analyst uses an AI terminal assistant that suggests a command to clear several directories. Which of the following is the best practice?" Review and understand the command before running it, and never run suggestions with elevated rights unchecked.
What to remember for the exam
- IDE plug-ins help with code, browser plug-ins with web content, CLI plug-ins with commands and scripts.
- Chatbots and personal assistants answer and draft; personal assistants often have broad access to email and files.
- MCP connects AI applications to tools and data through servers that offer tools, resources and prompts.
- Secure MCP servers with vetted sources, least privilege credentials, logging and confirmation for high-impact tools.
- AI tools that can act need stronger controls than tools that only advise.
Anything an MCP server can do, a prompt injection can ask the model to do. Scope every server's credentials as if the model will eventually be tricked.
Common mistakes
Treating an MCP server as just a connector. It is a privileged integration point. Vet it, scope it and log it like any service account.
Pasting sensitive data into an unapproved chatbot. Use the organisation's approved tools, and sanitise logs and code before sharing them.
Running AI-suggested commands blindly. A CLI assistant can suggest commands that delete data or weaken settings. The analyst stays responsible for what runs.
Check yourself
What three kinds of capability can an MCP server offer?
Tools the model can call, resources it can read and prompts that act as reusable templates.
Why is a browser plug-in exposed to indirect prompt injection?
It reads web content, and instructions hidden in a page can steer the model.
What control should apply when an AI tool can take actions rather than only advise?
Least privilege on its access plus human confirmation and logging for high-impact actions.
Topic 1 of 4 in AI-assisted Security
Test yourself on AI-assisted Security
The full CompTIA SecAI+ CY0-001 question bank has 654 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by CompTIA. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.