Snowflake Gen AI Governance · Topic 3 of 15
Data Safety - Cross-Region Inference and Guardrails
Data safety for Cortex AI: the CORTEX_ENABLED_CROSS_REGION parameter, where data goes, Cortex Guard on AI_COMPLETE and Cortex AI Guardrails.
- 4 min
- Includes a diagram
CORTEX_ENABLED_CROSS_REGIONis account level, set by ACCOUNTADMIN;DISABLEDmeans home region only.- Data is stored at home only; payloads are encrypted and not persisted elsewhere; credits bill to the requesting region.
- Cortex Guard is
'guardrails': TRUEin AI_COMPLETE model_parameters, default FALSE, extra input token cost.
What it is
Data safety for Gen AI covers two questions. Where is my prompt processed, and what stops harmful input or output? Cross-region inference answers the first: it lets Cortex run a model in another region when your home region does not host it. Guardrails answer the second: they filter unsafe model output or detect attacks such as prompt injection.
All Cortex LLMs are deployed within the Snowflake service perimeter, so prompts are not sent to the model provider's own public service. The settings below control how far that processing can travel and how it is screened.
How it works
Cross-region inference
The account parameter CORTEX_ENABLED_CROSS_REGION decides where requests may be processed. Only ACCOUNTADMIN can set it, with ALTER ACCOUNT. It cannot be set at user or session level, and ORGADMIN cannot set it.
| Scope | Values |
|---|---|
| Global | ANY_REGION |
| Cloud specific | AWS_GLOBAL, AZURE_GLOBAL, GCP_GLOBAL |
| Regional | AWS_US, AWS_EU, AWS_APJ, AWS_JP, AWS_AU, AZURE_US, AZURE_EU, GCP_US |
| Off | DISABLED (home region only) |
Comma-separated combinations are allowed. Check the value in effect with SHOW PARAMETERS; the value column is the effective one.
USE ROLE ACCOUNTADMIN;
ALTER ACCOUNT SET CORTEX_ENABLED_CROSS_REGION = 'AWS_US';
SHOW PARAMETERS LIKE 'CORTEX_ENABLED_CROSS_REGION' IN ACCOUNT;
ALTER ACCOUNT SET CORTEX_ENABLED_CROSS_REGION = 'DISABLED';
Defaults. New commercial organizations created after 9 March 2026 default to ANY_REGION. Other commercial accounts in supported regions inherit a same-cloud geography value, such as AWS_US or AZURE_EU. If you have data residency requirements, set the value yourself.
What happens to the data
- Customer data stays stored only in the home region.
- The prompt and response pass through the processing region temporarily and are not persisted there.
- Data in transit is always encrypted.
- Within one cloud provider, traffic stays on the provider's private backbone. Across providers it uses the public internet protected by mutual TLS.
- Credits are charged to the requesting region, and there are no data egress charges.
- Latency can rise; test your use case with the setting on.
A residency rule such as "data must not leave the EU" means set AWS_EU or AZURE_EU, not leave the default. DISABLED keeps everything at home but some models and the full Cortex AI suite then may not be available.
Guardrail option 1: Cortex Guard on AI_COMPLETE
Cortex Guard filters possibly unsafe or harmful model responses before they come back. It is built with Meta's Llama Guard 3 and covers categories such as violent crimes, hate, sexual content and self-harm. You turn it on per request in model_parameters.
SELECT AI_COMPLETE(
  model => 'llama3.1-70b',
  prompt => 'Summarize this ticket',
  model_parameters => {'guardrails': TRUE});
The default is FALSE. It costs extra: compute is billed on input tokens processed for the guard, in addition to the AI_COMPLETE charge.
Guardrail option 2: account-level Cortex AI Guardrails
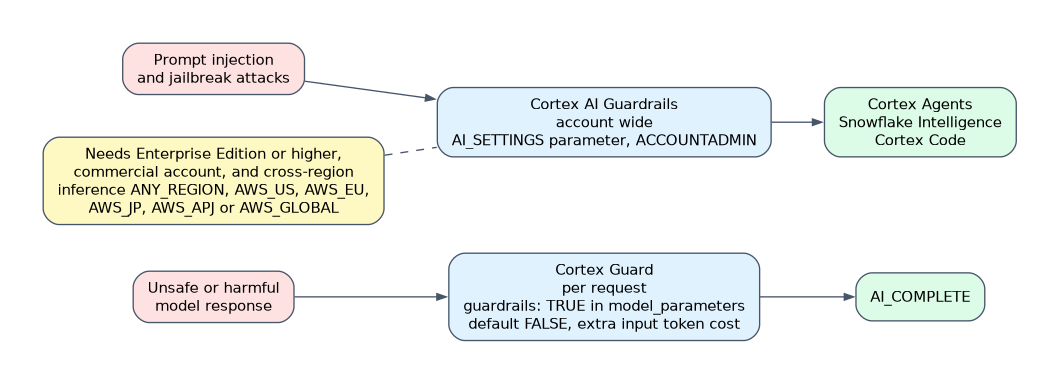 These give run-time protection against prompt injection and jailbreak attacks for Cortex Agents, Snowflake Intelligence (called Snowflake CoWork in current docs) and Cortex Code. They are enabled once for the account through the
AI_SETTINGS parameter by ACCOUNTADMIN.
ALTER ACCOUNT SET AI_SETTINGS = $$
  guardrails:
    advanced_prompt_injection:
      - enabled: true
$$;
SHOW PARAMETERS LIKE 'AI_SETTINGS' IN ACCOUNT;
ALTER ACCOUNT UNSET AI_SETTINGS;
Requirements: Enterprise Edition or higher, a commercial account, and cross-region inference set to ANY_REGION, AWS_US, AWS_EU, AWS_JP, AWS_APJ or AWS_GLOBAL. Scans are billed by tokens scanned and logged in SNOWFLAKE.ACCOUNT_USAGE.CORTEX_AI_GUARDRAILS_USAGE_HISTORY, where GUARDRAILS_SIGNAL = TRUE marks flagged requests.
| Feature | Cortex Guard | Cortex AI Guardrails |
|---|---|---|
| Level | Per request | Account wide |
| Set with | guardrails in model_parameters | AI_SETTINGS parameter |
| Protects against | Unsafe or harmful responses | Prompt injection and jailbreaks |
| Applies to | AI_COMPLETE | Agents, Snowflake Intelligence, Cortex Code |
Common mistakes
Assuming data is stored in the processing region. Only the home region stores data; the payload is transient.
Believing ORGADMIN controls the parameter. Only ACCOUNTADMIN can set CORTEX_ENABLED_CROSS_REGION.
Mixing up the two guardrails. Cortex Guard filters harmful output on one call; AI_SETTINGS guardrails detect prompt injection account wide.
Expecting Cortex Guard to stop wrong facts. It is a safety filter, not a factual accuracy check.
What to remember for the exam
CORTEX_ENABLED_CROSS_REGIONis account level, set by ACCOUNTADMIN;DISABLEDmeans home region only.- Data is stored at home only; payloads are encrypted and not persisted elsewhere; credits bill to the requesting region.
- Cortex Guard is
'guardrails': TRUEin AI_COMPLETE model_parameters, default FALSE, extra input token cost. - Cortex AI Guardrails use
AI_SETTINGSand need Enterprise Edition and cross-region inference.
Check yourself
A company must keep inference inside Europe. What do you set?
Set CORTEX_ENABLED_CROSS_REGION to an EU value such as AWS_EU or AZURE_EU as ACCOUNTADMIN, rather than relying on the default.
How do you filter harmful output from one AI_COMPLETE call?
Pass model_parameters with guardrails set to TRUE, which enables Cortex Guard at extra cost.
Which view records prompt injection scans?
SNOWFLAKE.ACCOUNT_USAGE.CORTEX_AI_GUARDRAILS_USAGE_HISTORY, with GUARDRAILS_SIGNAL marking flagged requests.
Topic 3 of 15 in Snowflake Gen AI Governance
Test yourself on Snowflake Gen AI Governance
The full Snowflake GES-C02 question bank has 585 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Snowflake. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.