Secure Storage, Databases, and Networking · Topic 3 of 3
Securing Azure Network Services
SC-500 network security: NSGs and ASGs, Virtual Network Manager rules, Virtual WAN, VPN, Entra Private Access, private endpoints, Azure Firewall and Network Watcher.
- 5 min
- Includes a diagram
- NSG rules are processed by priority, lowest number first; subnet and NIC NSGs both apply.
- ASGs group VMs by role; service tags group Azure IP ranges.
- Virtual Network Manager security admin rules are evaluated before NSGs.
What it is
Network security decides what traffic can reach your resources and what they can reach. SC-500 covers filtering with network security groups (NSGs) and application security groups (ASGs), central rules with Azure Virtual Network Manager, securing Virtual WAN and VPN connections, Microsoft Entra Private Access, private endpoints and Private Link, Azure Firewall, and checking rules with Network Watcher.
How it works
NSGs and ASGs
| Concept | Meaning |
|---|---|
| NSG rule | Priority, source, destination, port, protocol and Allow or Deny; lower priority numbers are processed first |
| Default rules | Allow traffic within the virtual network and from the load balancer; deny other inbound; allow outbound to the internet |
| Association | Attach an NSG to a subnet, a network interface, or both; traffic must pass both when both exist |
| Application security group | Groups VMs by role, such as WebServers, so rules can target the group instead of IP addresses |
| Service tags | Named groups of Azure IP ranges, such as Storage or AzureLoadBalancer |
Azure Virtual Network Manager
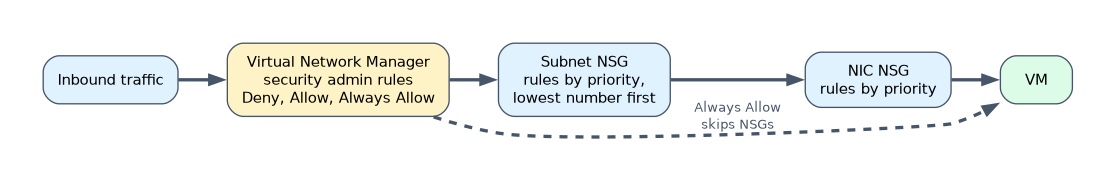 Virtual Network Manager applies security admin rules centrally across the virtual networks in a network group. Security admin rules are evaluated before NSG rules. Deny and Always Allow end evaluation, so local NSGs cannot override them; Allow lets the NSG rules still decide.
Virtual WAN, VPN and Entra Private Access
- Virtual WAN connects branches and virtual networks through hubs; a secured virtual hub adds Azure Firewall managed with Azure Firewall Manager.
- VPN gateways connect on-premises networks (site-to-site) and users (point-to-site). Use strong IKE/IPsec settings, and Microsoft Entra ID authentication for point-to-site where possible.
- Microsoft Entra Private Access gives users with the Global Secure Access client identity-based access to private apps without a traditional VPN. Private resources are published as Quick Access or per-app Global Secure Access apps (enterprise applications) through a private network connector, and Conditional Access applies to each app.
Private endpoints and Private Link
| Feature | What it does |
|---|---|
| Private endpoint | A network interface with a private IP in your virtual network that connects to a PaaS resource, such as Storage or SQL |
| Private Link service | Lets you expose your own service, behind a standard load balancer, privately to consumers in other networks |
| Private DNS zones | Resolve the service name to the private IP |
| Service endpoint | Older option: keeps traffic on the Azure backbone to a service's public endpoint, without a private IP |
Azure Firewall
| SKU | Notes |
|---|---|
| Basic | Small environments, up to 250 Mbps; threat intelligence in alert mode only |
| Standard | Network and application rules, threat intelligence filtering, DNS proxy, web categories |
| Premium | Adds TLS inspection, intrusion detection and prevention (IDPS) and URL filtering |
Rules are organized in a firewall policy with DNAT, network and application rule collections. Route traffic through the firewall with user-defined routes.
Network Watcher diagnostics
| Tool | Answers |
|---|---|
| IP flow verify | Is a specific packet allowed or denied, and by which rule? |
| NSG diagnostics | Which rules apply to a flow across NSGs |
| Effective security rules | The combined rules applied to a network interface |
| Next hop | Where traffic is routed next |
| Flow logs | Records of traffic for analysis; use virtual network flow logs, because NSG flow logs are retiring and new ones can't be created |
A worked example: a central team must block RDP from the internet to every VM in 50 subscriptions, even if workload teams add their own NSG rules. A Virtual Network Manager security admin rule denying inbound port 3389 is evaluated before the NSGs and cannot be overridden locally.
"A rule local teams cannot override" points to Virtual Network Manager security admin rules. "Which rule blocked this packet" points to IP flow verify or NSG diagnostics.
How the exam asks about this
- "Allow web servers to reach database servers without listing IP addresses." Use application security groups.
- "Inspect encrypted outbound traffic and detect intrusions." Azure Firewall Premium.
- "Reach Azure SQL over a private IP." A private endpoint with a private DNS zone.
What to remember for the exam
- NSG rules are processed by priority, lowest number first; subnet and NIC NSGs both apply.
- ASGs group VMs by role; service tags group Azure IP ranges.
- Virtual Network Manager security admin rules are evaluated before NSGs.
- Private endpoint: private IP for a PaaS resource. Private Link service: expose your own service privately.
- Azure Firewall Premium adds TLS inspection, IDPS and URL filtering.
- Network Watcher: IP flow verify, NSG diagnostics, effective security rules, next hop, flow logs.
A service endpoint does not give the resource a private IP address. If the requirement is a private IP, use a private endpoint.
Common mistakes
Assuming a high priority number wins. Lower numbers are processed first.
Forgetting private DNS. Without it, clients resolve the public address.
Choosing Standard firewall for TLS inspection. That needs Premium.
Check yourself
Which NSG rule is processed first: priority 100 or 200?
Priority 100, because lower numbers are processed first.
How do Virtual Network Manager security admin rules relate to NSGs?
They are evaluated before NSG rules, so local NSGs cannot override a central Deny or Always Allow.
Which Azure Firewall SKU provides TLS inspection and IDPS?
Azure Firewall Premium.
Topic 3 of 3 in Secure Storage, Databases, and Networking
Test yourself on Secure Storage, Databases, and Networking
The full Microsoft SC-500 question bank has 650 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.