Design security solutions for infrastructure · Topic 1 of 6
Security Posture Management with Defender for Cloud
SC-100 posture: Defender for Cloud secure score, foundational versus Defender CSPM, attack paths, workload protection plans and connectors.
- 6 min
- Includes a diagram
- Foundational CSPM is free: asset inventory, secure score, recommendations, MCSB. Defender CSPM adds attack paths, cloud security explorer, agentless scanning, governance rules, data security posture management and extra compliance standards.
- Defender for Cloud covers Azure, AWS, GCP and Arc connected servers. MCSB is the default standard.
- Select workload protection plans by workload: Servers, Containers, Storage, Databases, App Service, Key Vault, APIs, AI services.
What it is
Security posture is how well configured and hardened your environment is against attack. Cloud security posture management (CSPM) continuously finds misconfigurations and risks and tells you what to fix first. Cloud workload protection (CWP) detects and blocks active threats against specific workloads. Microsoft Defender for Cloud provides both, for Azure, AWS, Google Cloud and on premises resources.
How it works
Defender for Cloud posture capabilities
| Capability | What it does |
|---|---|
| Secure score | A percentage showing how many recommended controls are met. Recommendations are grouped into security controls with a maximum score contribution, so fixing a high value control raises the score most |
| Recommendations | Specific, prioritized fixes based on the Microsoft Cloud Security Benchmark (the default initiative) and any other standards you assign |
| Regulatory compliance | Assess against standards such as NIST, ISO and PCI DSS (see the compliance topic) |
| Inventory | Unified list of resources and their coverage |
| Workflow automation | Trigger Logic Apps from alerts and recommendations |
Two CSPM tiers:
| Tier | Contents |
|---|---|
| Foundational CSPM (free) | Secure score, recommendations, MCSB assessment, asset inventory |
| Defender CSPM (paid) | Everything in foundational plus attack path analysis, cloud security explorer (risk hunting across your environment), risk prioritization, internet exposure analysis, critical assets protection, agentless scanning of VMs and containers for vulnerabilities and secrets, governance rules (assign owners and due dates to recommendations), data security posture management (find sensitive data in storage and databases), regulatory compliance assessments beyond the default benchmark, custom recommendations, external attack surface management integration, code to cloud mapping through DevOps security, and AI and API security posture |
Attack path analysis is the key idea: it shows how an attacker could chain weaknesses, for example an internet exposed VM with a vulnerability, a managed identity with high privilege and a storage account holding sensitive data, so you fix the path rather than hundreds of isolated findings. The cloud security explorer queries relationships such as "VMs exposed to the internet with high severity vulnerabilities and access to sensitive data".
Microsoft Secure Score
Do not confuse Defender for Cloud's secure score with Microsoft Secure Score, which lives in the Microsoft Defender portal and measures posture across Microsoft 365 and connected apps: identity, devices, apps and data. It gives improvement actions with point values, tracks them as planned, implemented or accepted risk, and compares with similar organizations. Use it to evaluate productivity and collaboration workloads. The Microsoft Security Exposure Management service brings these scores and attack paths together (see the next topic).
Cloud workload protection plans
Turn on the plans that match your resources. They detect threats and add hardening features.
| Plan | Protects |
|---|---|
| Defender for Servers (Plan 1 and 2) | Windows and Linux servers in Azure, other clouds and on premises through Azure Arc. Integrates Defender for Endpoint, vulnerability assessment, just in time VM access, file integrity monitoring and agentless scanning in Plan 2 |
| Defender for Containers | Kubernetes clusters and registries: image scanning, runtime threat detection and admission control |
| Defender for Storage | Storage accounts: threat detection, malware scanning on upload, sensitive data threat detection |
| Defender for Databases | Azure SQL, SQL on machines, open source relational databases and Cosmos DB |
| Defender for App Service | Web apps: detects attacks on App Service |
| Defender for Key Vault | Unusual access to secrets and keys |
| Defender for Resource Manager | Suspicious management operations |
| Defender for APIs | API inventory and runtime threat detection for APIs published in API Management |
| Defender for AI services | Threat protection for Azure AI workloads |
| Defender for DevOps (in CSPM) | Posture of code repositories and pipelines in Azure DevOps, GitHub and GitLab |
Selecting plans is a requirements exercise: list the workload types, decide the risk, and enable the matching plan at subscription level. Plans bill per resource or usage, so enable them where the workloads are, not everywhere.
Evaluating posture in hybrid and multicloud
| Environment | Onboarding |
|---|---|
| Azure | Subscriptions are covered natively. Enable the plans |
| AWS | Connect an AWS account or organization with a connector (deployed using CloudFormation or Terraform) to get CSPM and workload protection, and the AWS standard assessments |
| Google Cloud | Connect a GCP project or organization with a connector |
| On premises and other clouds' servers | Azure Arc projects the servers into Azure so Defender for Servers and policy apply |
| Code and pipelines | DevOps connectors for Azure DevOps, GitHub and GitLab |
All of it appears in one secure score and one inventory, with recommendations tailored per cloud. Use governance rules and workflow automation to drive remediation, and send alerts to Defender XDR and Sentinel.
Designing the posture process
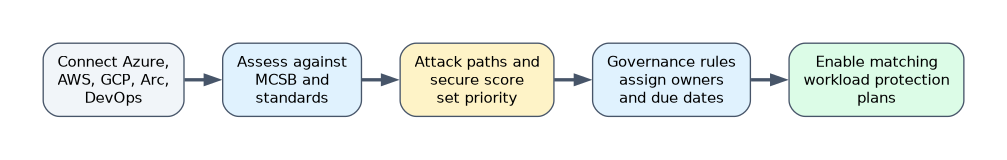
- Connect all environments and enable Defender CSPM where the budget allows.
- Assign the MCSB plus the regulatory standards you need.
- Prioritize by attack paths and secure score controls, not raw counts.
- Assign owners and due dates with governance rules and track progress.
- Enable the workload protection plans that match your workloads.
- Review regularly and automate fixes with Azure Policy DeployIfNotExists and Modify where safe.
A worked scenario
A company runs workloads in Azure and AWS and has too many recommendations to act on. The architect enables Defender CSPM and connects AWS. The attack path analysis reveals an internet facing VM that has a known vulnerability and can reach a database with customer data. The team fixes that path first, assigns owners using governance rules, and enables Defender for Servers Plan 2, Databases and Storage.
What to remember for the exam
- Foundational CSPM is free: asset inventory, secure score, recommendations, MCSB. Defender CSPM adds attack paths, cloud security explorer, agentless scanning, governance rules, data security posture management and extra compliance standards.
- Defender for Cloud covers Azure, AWS, GCP and Arc connected servers. MCSB is the default standard.
- Select workload protection plans by workload: Servers, Containers, Storage, Databases, App Service, Key Vault, APIs, AI services.
- Microsoft Secure Score (Defender portal) covers Microsoft 365 and apps. It is separate from Defender for Cloud's secure score.
- Fix attack paths first.
"Show how an attacker could reach sensitive data through a chain of weaknesses" is attack path analysis in Defender CSPM.
How the exam asks about this
- "Assign owners and due dates to security recommendations." Governance rules in Defender CSPM.
- "Query for VMs exposed to the internet with vulnerabilities." Cloud security explorer.
- "Include AWS accounts in posture management." A Defender for Cloud AWS connector.
- "Protect storage accounts from malware uploads." Defender for Storage malware scanning.
Common mistakes
Enabling every plan everywhere. Match plans to workloads and cost.
Chasing the number of recommendations. Prioritize attack paths and high score controls.
Confusing the two secure scores. One is Azure and multicloud, the other is Microsoft 365.
Ignoring ownership. Without owners, recommendations do not get fixed.
Check yourself
Which Defender for Cloud tier includes attack path analysis?
Defender CSPM.
Which plan protects Azure SQL, SQL on machines and Cosmos DB?
Defender for Databases.
How are servers outside Azure brought into Defender for Cloud?
Through Azure Arc, or for AWS and GCP through a connector.
Topic 1 of 6 in Design security solutions for infrastructure
Test yourself on Design security solutions for infrastructure
The full Microsoft SC-100 question bank has 770 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.