Design security solutions for infrastructure · Topic 6 of 6
Network Security and Security Service Edge
SC-100 networks: segmentation, Azure Firewall, WAF, DDoS and Private Link, plus Entra Internet Access, Internet Access for Microsoft services and Private Access.
- 6 min
- Includes a diagram
- Azure network security tools: NSGs, Azure Firewall (Premium has TLS inspection and IDPS), WAF, DDoS Protection, Private Link, Bastion.
- SSE in Microsoft: Entra Internet Access (secure web gateway), Internet Access for Microsoft services, Entra Private Access (ZTNA).
- Compliant network check, universal tenant restrictions and source IP restoration come from Global Secure Access.
What it is
Zero Trust does not mean the network does not matter. It means the network is one more signal and one more control, not the only one. Good network design segments workloads, inspects traffic, hides services from the internet and limits what can move laterally. Security Service Edge (SSE) moves much of that protection to the cloud edge, closer to users, so access to the internet, SaaS and private apps is controlled by identity rather than by a corporate VPN or perimeter.
How it works
Network design in Azure
| Requirement | Solution |
|---|---|
| Segment workloads | Separate virtual networks and subnets by trust level, hub and spoke or Virtual WAN designs, with the hub holding shared security services |
| Filter at layer 4 | Network security groups (NSGs) and application security groups for subnet and NIC rules |
| Central inspection | Azure Firewall in the hub with user defined routes forcing traffic through it. Premium adds TLS inspection, intrusion detection and prevention (IDPS) and URL filtering. Azure Firewall Manager manages policies across firewalls and secured virtual hubs |
| Protect web apps | Web Application Firewall on Application Gateway or Front Door |
| Protect from volumetric attacks | Azure DDoS Protection, enabled on virtual networks (network protection) or on individual public IPs (IP protection) |
| Remove public exposure | Private Link and private endpoints for PaaS services, with private DNS zones. Service endpoints are an older, less isolating option |
| Safe administration | Azure Bastion and JIT VM access instead of public RDP or SSH |
| Control outbound | Firewall rules, FQDN filtering and threat intelligence, forced tunneling where required |
| Hybrid connectivity | VPN Gateway or ExpressRoute, ideally with encryption, and Virtual WAN for branches |
| Visibility | NSG flow logs and virtual network flow logs with Traffic Analytics, firewall logs, Network Watcher tools |
Evaluating a network design means checking: is there segmentation, is east west traffic inspected where needed, do PaaS services use private endpoints, are management ports closed, is there egress control, and is traffic logged?
A common trap is a private endpoint whose traffic bypasses the firewall, because the endpoint's route is more specific than the user defined route. Network policies for private endpoints on the subnet and routes for the endpoint prefix bring the traffic through the firewall.
Security Service Edge with Microsoft Entra Global Secure Access
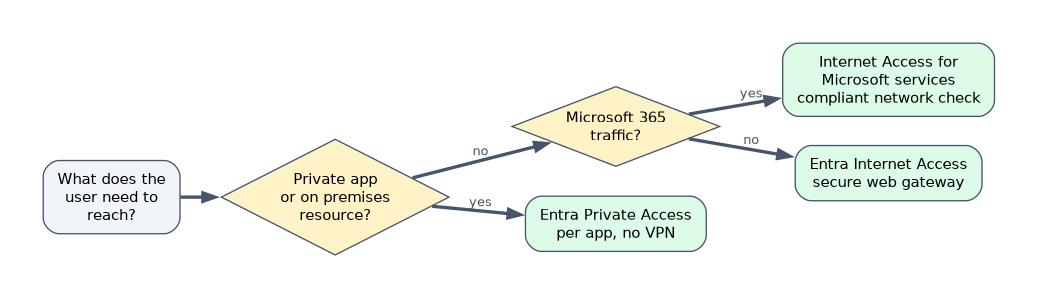 Global Secure Access is Microsoft's SSE solution, built on Entra ID. Users install the Global Secure Access client (Windows, macOS, Android, iOS) or connect through a remote network, and their traffic goes to Microsoft's global edge where policies are applied. It provides:
| Product | Purpose |
|---|---|
| Microsoft Entra Internet Access | A secure web gateway for the internet and SaaS. Web content filtering by category, URL or FQDN, threat protection, and identity aware policies |
| Microsoft Entra Internet Access for Microsoft services | Optimized and secured access to Microsoft 365 (Exchange Online, SharePoint Online, Teams, Microsoft Graph) with identity based controls and traffic logs |
| Microsoft Entra Private Access | Zero Trust network access (ZTNA) to private apps and resources, replacing a VPN, with per application access over TCP and UDP |
Traffic is steered by forwarding profiles (Microsoft 365, Internet, Private access) that you turn on and scope to users and devices.
Entra Internet Access for Microsoft services and cross tenant scenarios. Because Microsoft 365 traffic passes through the service, it adds:
- Compliant network check in Conditional Access: require that access to Microsoft 365 and other resources comes through your organization's Global Secure Access network. A stolen token used from elsewhere fails the check.
- Universal tenant restrictions (tenant restrictions v2 enforced at the network edge): control which external tenants your users may sign in to from your devices, to stop data moving to other tenants or personal accounts. Cross tenant access settings define which partners are allowed.
- Source IP restoration so Conditional Access, Identity Protection and sign in logs see the user's real source IP.
- Network traffic logs for investigation.
Entra Private Access uses lightweight private network connectors installed in the network where the private apps live (on premises or in a cloud). The connectors make outbound connections only. You then define:
- Quick Access for broad access to defined IP ranges and DNS suffixes with minimal setup, and
- Per app access with app segments (FQDN, IP and ports) and assignments, to which Conditional Access applies, including MFA.
Benefits over a VPN: least privilege per app instead of network wide access, Conditional Access on private resources, no inbound firewall rules, and no flat network to move laterally in.
Choosing quickly
| Requirement | Answer |
|---|---|
| Inspect and filter traffic between spokes and to the internet | Azure Firewall in the hub with UDRs |
| Block common web exploits on a regional app | Application Gateway WAF |
| Mitigate a volumetric attack | Azure DDoS Protection |
| Keep a database off the internet | Private endpoint |
| Replace VPN with per app, identity based access | Entra Private Access |
| Filter web access and apply policy on the user's device anywhere | Entra Internet Access |
| Prevent use of stolen tokens from outside corporate access | Compliant network check |
| Stop users signing in to personal or unknown tenants | Universal tenant restrictions |
A worked scenario
A company has a hub and spoke network with Azure Firewall Premium, but investigators find PaaS traffic going straight between spokes. The architect adds routes for the private endpoint prefixes to send traffic through the firewall. For remote workers, they replace the VPN with Entra Private Access for internal apps, add Entra Internet Access for web filtering, enable the compliant network check for Microsoft 365, and turn on universal tenant restrictions.
What to remember for the exam
- Azure network security tools: NSGs, Azure Firewall (Premium has TLS inspection and IDPS), WAF, DDoS Protection, Private Link, Bastion.
- SSE in Microsoft: Entra Internet Access (secure web gateway), Internet Access for Microsoft services, Entra Private Access (ZTNA).
- Compliant network check, universal tenant restrictions and source IP restoration come from Global Secure Access.
- Private Access uses outbound only connectors, per app segments and Conditional Access. It replaces VPN.
- Forwarding profiles control which traffic goes through the service.
"Replace VPN with identity aware, per app access to on premises apps" is Entra Private Access. "Filter outbound web traffic for remote users" is Entra Internet Access.
How the exam asks about this
- "Inspect TLS traffic and detect intrusions in Azure." Azure Firewall Premium.
- "Require that Microsoft 365 is reached only from the corporate network edge." Compliant network check in Conditional Access.
- "Restrict which external tenants employees can sign in to." Tenant restrictions enforced through Global Secure Access.
- "Give contractors access to one internal web app only." Entra Private Access per app segment.
Common mistakes
Network location as the only trust signal. Combine with identity and device.
Public endpoints plus IP allow lists for PaaS. Private endpoints are stronger.
Assuming private endpoints go through the firewall. Add the route.
Choosing a VPN for per app access. SSE gives per app control.
Check yourself
Which Azure Firewall tier supports TLS inspection and IDPS?
Premium.
Which Global Secure Access product provides zero trust network access to private apps?
Microsoft Entra Private Access.
What does the compliant network check do in Conditional Access?
Requires that access comes through the organization's Global Secure Access network.
Topic 6 of 6 in Design security solutions for infrastructure
Test yourself on Design security solutions for infrastructure
The full Microsoft SC-100 question bank has 770 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.