Design security solutions for applications and data · Topic 4 of 5
Data Discovery, Classification and Encryption
SC-100 data protection: discovery and classification with Purview, prioritizing data threats, and encryption at rest and in transit with customer keys.
- 6 min
- Includes a diagram
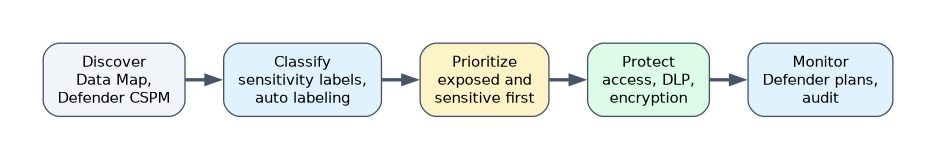
- Discover, classify, prioritize, protect. Labels can be automatic using sensitive information types, EDM and trainable classifiers.
- Purview Data Map scans sources. Defender CSPM data aware posture finds sensitive data in cloud stores. DSPM guides protection.
- SSE is on by default with Microsoft managed keys. CMK gives key control. Infrastructure encryption doubles encryption. Encryption at host covers temp disks.
What it is
You cannot protect data you do not know about. Data protection therefore follows an order: discover where data is, classify how sensitive it is, prioritize the threats to it, and then protect it with access control, labels, DLP and encryption. This topic covers the first three and the encryption controls; the next page covers specific Azure data services.
How it works
Data discovery and classification
| Solution | What it does |
|---|---|
| Microsoft Purview Information Protection | Sensitivity labels classify and protect documents and email. Labels can be applied manually, by default, or automatically based on sensitive information types (such as credit card numbers), exact data match (EDM), document fingerprints and trainable classifiers |
| Information Protection scanner | Scans on premises file shares and repositories and labels files |
| Microsoft Purview Data Map and Unified Catalog | Scan and map data sources across Azure, on premises, multicloud and SaaS (Azure SQL, Storage, Amazon S3, and more), apply classifications, build a catalog and glossary and show lineage |
| Defender for Cloud data aware security posture (in Defender CSPM) | Discovers sensitive data in Azure Storage and databases and in AWS, and reflects it in attack paths and recommendations |
| Azure SQL data discovery and classification | Finds and labels sensitive columns in SQL databases |
| Purview Data Security Posture Management (DSPM) | Shows where sensitive data lives, how it is used and which protections are missing, with recommended policies |
Sensitive information types are patterns (such as national ID numbers) with confidence levels, and trainable classifiers use machine learning to recognize categories like contracts. A common label scheme is Public, General, Confidential, Highly Confidential, each with different protection. Labels travel with the file and can enforce encryption, access rights, watermarks and DLP behavior.
Prioritizing threats to data
Rank the data by sensitivity and exposure, then mitigate the biggest risks first.
| Threat | Mitigation |
|---|---|
| Excessive access and oversharing | Least privilege, access reviews, Conditional Access, permissions clean up, CIEM |
| Exfiltration by insiders | Insider Risk Management, DLP on endpoints, Defender for Cloud Apps session controls |
| Exfiltration by attackers | Private endpoints, no public access, egress control, anomaly detection |
| Ransomware and destruction | Immutable backups, soft delete, versioning, privileged access protection |
| Unprotected sensitive stores | Data aware posture and attack paths find sensitive data reachable from the internet |
| Loss of device or media | Encryption, device compliance |
| Compliance violations | Retention, residency policies, audit |
| Data used by AI | Labels, DLP and permissions so AI cannot reach more than intended |
Prioritization uses business impact and likelihood: exposed and highly sensitive data first. Attack paths that end at sensitive data stores are the top candidates.
Encryption at rest
| Technique | Details |
|---|---|
| Service side encryption (SSE) | Enabled by default for Azure Storage, managed disks, SQL and most services, with Microsoft managed keys |
| Customer managed keys (CMK) | You control the key in Azure Key Vault or Managed HSM, with rotation and revocation. Needed when regulation demands key control. Services access the key with a managed identity |
| Infrastructure encryption (double encryption) | A second layer with a different algorithm and key for Storage and some other services, selected when you create the resource |
| Encryption at host | Encrypts temporary disks, caches and data flows to storage for VMs from the host |
| Azure Disk Encryption | BitLocker or dm-crypt inside the VM, with keys in Key Vault |
| Confidential disk encryption and confidential computing | Protects data in use in hardware based trusted execution environments |
| Transparent Data Encryption (TDE) | Encrypts SQL data files, on by default, with service managed or customer managed key |
| Always Encrypted | Client side encryption of specific columns, so the database engine never sees plaintext (secure enclaves allow some computation) |
| Column and file encryption | Application level encryption and double key encryption for the most sensitive Purview labeled content, where you hold a key |
Encryption in transit
- Require TLS 1.2 or higher and HTTPS only, set minimum TLS versions on storage, SQL and web apps, and use secure transfer required.
- VPN (IPsec), MACsec on ExpressRoute Direct, and application level TLS for hybrid links.
- TLS inspection at Azure Firewall Premium where policy requires visibility, balanced with privacy.
- Manage certificates in Key Vault with automatic renewal.
Key management
| Practice | Detail |
|---|---|
| Choose the right store | Key Vault (software and HSM backed), Managed HSM for FIPS 140 level 3 and sole control, Azure Cloud HSM for dedicated devices |
| Separate duties | Key administrators are not data administrators |
| Protect keys | Soft delete, purge protection, RBAC, private endpoints |
| Rotate and revoke | Rotation policies, with the ability to revoke a CMK to render data inaccessible |
| Bring your own key (BYOK) | Import keys from your own HSM |
A worked scenario
A hospital group discovers patient data in several storage accounts and file shares. The architect uses the Purview Data Map to scan stores, auto labels records with a sensitive information type for health identifiers, and applies Highly Confidential labels with encryption. Defender CSPM data aware posture shows one storage account with patient data reachable from the internet through an attack path, which is fixed first. Regulations require key control, so the architect uses customer managed keys in Managed HSM and infrastructure encryption, with TLS 1.2 enforced.
What to remember for the exam
- Discover, classify, prioritize, protect. Labels can be automatic using sensitive information types, EDM and trainable classifiers.
- Purview Data Map scans sources. Defender CSPM data aware posture finds sensitive data in cloud stores. DSPM guides protection.
- SSE is on by default with Microsoft managed keys. CMK gives key control. Infrastructure encryption doubles encryption. Encryption at host covers temp disks.
- TDE for SQL. Always Encrypted for client side column protection. Confidential computing protects data in use.
- Enforce TLS 1.2 or higher and HTTPS. Protect keys with soft delete, purge protection and RBAC.
"Database administrators must never see plaintext in specific columns" is Always Encrypted.
How the exam asks about this
- "Automatically label documents that contain credit card numbers." Sensitivity label auto labeling with a sensitive information type.
- "Scan on premises file shares for sensitive data." Information Protection scanner.
- "Meet a requirement to control and revoke the encryption key." Customer managed keys in Key Vault or Managed HSM.
- "Encrypt data on temporary disks and caches." Encryption at host.
Common mistakes
Encrypting without classifying. You cannot prioritize or apply the right controls.
Assuming encryption stops oversharing. Authorized users still see plaintext.
Weak key governance. A deleted key without purge protection can be unrecoverable or abused.
Leaving old TLS versions allowed. Set the minimum.
Check yourself
Which Purview solution scans and maps data sources across cloud and on premises?
The Microsoft Purview Data Map.
Which SQL feature keeps column plaintext hidden even from the database engine?
Always Encrypted.
What provides a second layer of encryption with a different key for Azure Storage?
Infrastructure encryption.
Topic 4 of 5 in Design security solutions for applications and data
Test yourself on Design security solutions for applications and data
The full Microsoft SC-100 question bank has 770 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.