Pipelines: infrastructure as code · Topic 1 of 2
Configuration Management and IaC Strategy
AZ-400 IaC: Bicep, ARM, Terraform, Ansible, Chef and Puppet compared, plus source control, what-if and plan testing, remote state and drift detection.
- 5 min
- Includes a diagram
- Bicep compiles to ARM and has no state file. Terraform uses a state file stored remotely with locking.
- Ansible is agentless over SSH or WinRM. Chef and Puppet use agents that pull.
- Preview with what-if or plan before applying. Test and lint IaC like application code.
What it is
Infrastructure as code (IaC) describes servers, networks and services in files that a tool applies. Because the description is code, you can store it in Git, review it in pull requests, test it and deploy it repeatedly with the same result.
Configuration management is the related job of setting up the software and settings inside machines. The exam asks you to recommend a technology and then define a strategy: how the code is stored, tested and deployed.
How it works
Provisioning tools
| Tool | Style | Notes |
|---|---|---|
| ARM templates | Declarative JSON | The native Azure format. Verbose. Everything else on Azure deploys through it |
| Bicep | Declarative DSL | Compiles to ARM. Cleaner syntax, modules, first day support for new Azure features, no state file to manage. az deployment group create applies it, and what-if previews changes |
| Terraform | Declarative HCL | Multi cloud, many providers. Keeps a state file that maps code to real resources. terraform plan previews and apply applies |
| Pulumi | Code in general languages | Declarative engine driven by languages such as C#, TypeScript and Python |
| Azure CLI / PowerShell scripts | Imperative | Flexible, but you must make them idempotent yourself |
Rule of thumb: an Azure only team that wants a native tool picks Bicep. A multi cloud organization or one already using it picks Terraform.
Configuration management tools
| Tool | How it works |
|---|---|
| Ansible | Agentless. Playbooks in YAML run over SSH (Linux) or WinRM (Windows). Push model |
| Chef | Agent on each node pulls configuration written in a Ruby based language ("cookbooks") from a server |
| Puppet | Agent pulls declarative "manifests" from a server and enforces them |
| PowerShell DSC / Azure Machine Configuration | Declarative state for Windows and Linux machines in Azure and on premises (next page) |
Mutable infrastructure is updated in place with a configuration tool. Immutable infrastructure is replaced: you build a new image or container and swap it in. Immutable avoids drift and is simpler to roll back.
A strategy for IaC
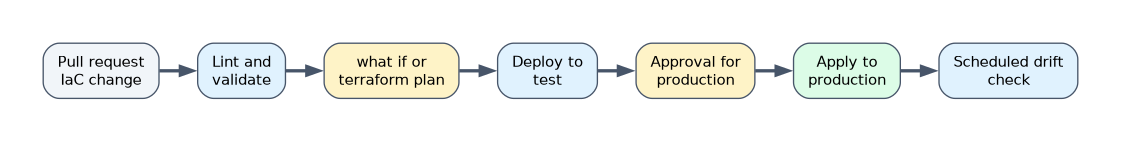 1. Source control. Keep infrastructure code in Git, in its own repository or beside the application. Use branches, pull requests and policies exactly as for code. Never keep secrets in it. Reference Key Vault secrets instead.
2. Structure for reuse. Use modules (Bicep modules, Terraform modules, template specs, Azure Verified Modules) and separate parameter files per environment (a .bicepparam file or .tfvars file) so the same code builds dev, test and production.
3. Automated testing.
| Check | Examples |
|---|---|
| Syntax and lint | bicep build, Bicep linter, terraform validate, terraform fmt -check |
| Preview | az deployment group what-if, terraform plan shown for review |
| Policy and security | Azure Policy, static analysis of templates for insecure settings |
| Integration | Deploy to a temporary environment and test it (for example with Pester or Terratest), then delete it |
4. Automated deployment. The pipeline deploys, not a person. Use environments with approvals. For production, run the preview, require approval, then apply the same plan.
5. Safe state handling.
- Terraform state must be stored remotely (an Azure Storage blob container is common), with locking so two runs cannot apply together. Do not commit state, which can hold secrets.
- ARM and Bicep have no state file, because Azure Resource Manager is the source of truth.
6. Drift detection. Drift is when real resources no longer match the code. Run what-if or terraform plan on a schedule, and block portal changes with policy or role assignments.
ARM and Bicep deployment details
| Setting | Meaning |
|---|---|
| Scopes | Resource group, subscription, management group or tenant |
| Incremental mode (default) | Adds and updates resources in the template and leaves others alone |
| Complete mode | Also deletes resources in the group that are not in the template. Use with care |
| Deployment stacks | Manage a set of resources as a unit, including cleanup and deny settings that protect them |
param location string = resourceGroup().location
resource sa 'Microsoft.Storage/storageAccounts@2023-05-01' = {
  name: 'stdemo${uniqueString(resourceGroup().id)}'
  location: location
  sku: { name: 'Standard_LRS' }
  kind: 'StorageV2'
}
In pipelines use AzureResourceManagerTemplateDeployment@3 or AzureCLI@2 with az deployment. In GitHub use the azure/arm-deploy action or run the CLI.
Choosing quickly
| Requirement | Answer |
|---|---|
| Native Azure IaC with no state to manage | Bicep |
| One tool for Azure, AWS and others | Terraform |
| Configure many servers without installing agents | Ansible |
| Preview changes before applying | what-if (Bicep and ARM) or plan (Terraform) |
| Prevent two applies running at once on shared state | Remote state backend with locking |
| Avoid manual changes drifting from code | Scheduled preview, policy and restricted access |
A worked scenario
A platform team manages networks and App Services in Azure. They write Bicep modules, keep a .bicepparam file per environment and run a pipeline that lints, runs what-if and posts the result on the pull request. After merge the pipeline deploys to test, then waits for approval before production. A nightly job runs what-if against production and alerts if it shows changes, which means somebody changed a resource by hand.
What to remember for the exam
- Bicep compiles to ARM and has no state file. Terraform uses a state file stored remotely with locking.
- Ansible is agentless over SSH or WinRM. Chef and Puppet use agents that pull.
- Preview with what-if or plan before applying. Test and lint IaC like application code.
- ARM Incremental mode keeps extra resources. Complete mode deletes them.
- Use modules and per environment parameter files, and Key Vault for secrets.
Terraform state can contain secrets. Store it in a protected remote backend, never in Git.
How the exam asks about this
- "Preview what a template deployment would change." what-if.
- "Share Terraform state safely across a team." A remote backend such as Azure Storage with locking.
- "Configure Linux servers without agents." Ansible.
- "Make sure resources not in the template are removed." Complete deployment mode, or a deployment stack.
Common mistakes
Running Complete mode by accident. It deletes anything the template does not list.
Local Terraform state. Teammates cannot see it and two applies can corrupt it.
Secrets in parameter files. Use Key Vault references.
Allowing portal edits. They cause drift that the next deployment may overwrite.
Check yourself
Which IaC language compiles to ARM templates and needs no state file?
Bicep.
Which deployment mode removes resources that are not in the template?
Complete mode.
Which configuration management tool is agentless and uses YAML playbooks?
Ansible.
Topic 1 of 2 in Pipelines: infrastructure as code
Test yourself on Pipelines: infrastructure as code
The full Microsoft AZ-400 question bank has 766 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.