Pipelines: design and implement pipelines · Topic 3 of 3
Reusable Pipeline Elements, Checks and Approvals
AZ-400 reuse and control: YAML templates and extends, variable groups, reusable workflows, environments, approvals and checks on protected resources.
- 5 min
- Includes a diagram
- Templates: include (
template:) andextends:. Extends forces a structure. Parameters are compile time. - Variable groups live in the Library and can be linked to Key Vault. Mark secrets and map them to scripts explicitly.
- Task groups are classic. YAML uses templates. GitHub uses reusable workflows and composite actions.
What it is
Copying the same steps into fifty pipelines means fifty places to fix. Reusable elements put the shared logic in one place. Checks and approvals put control over sensitive resources in one place too, outside the pipeline file, so authors cannot remove them.
How it works
YAML templates
A template is a YAML file included from another file. Templates can define steps, jobs, stages or variables, and accept parameters.
# templates/build-steps.yml
parameters:
- name: configuration
  type: string
  default: Release
steps:
- script: dotnet build -c ${{ parameters.configuration }}
# azure-pipelines.yml
steps:
- template: templates/build-steps.yml
parameters:
configuration: Debug| Pattern | Use |
|---|---|
Include template (template:) | Insert steps, jobs or stages into your pipeline |
Extends template (extends:) | Your pipeline must be built on a parent template that sets the structure, so a security team can force required steps |
| Template from another repository | Use resources: repositories: and template: file@alias to share across projects |
| Variable template | Share variable definitions |
Template expressions ${{ }} are evaluated at compile time. Macro syntax $(var) is replaced at runtime before a task runs. Runtime expressions $[ ] are evaluated at runtime and used in conditions and some mappings.
Variables and variable groups
| Element | Notes |
|---|---|
| Pipeline variables | Defined in YAML or the UI. Mark as secret to mask them in logs |
| Variable groups | Shared sets of variables in Pipelines > Library, used by many pipelines. Can be linked to Azure Key Vault to fetch secrets at run time |
| Parameters | Typed values, set when the pipeline is queued or by a template. Evaluated at compile time |
| Output variables | A step sets a value that later steps, jobs or stages read |
| Predefined variables | For example Build.BuildId, Build.SourceBranch, System.TeamProject |
Secrets are never exposed to a script automatically. You map them explicitly, for example env: MY_SECRET: $(mySecret).
Task groups and GitHub reuse
Task groups bundle a sequence of tasks into one reusable task in the classic editor. In YAML, use templates instead.
| Platform | Reuse mechanism |
|---|---|
| Azure Pipelines (YAML) | Templates, extends, variable groups |
| Azure Pipelines (classic) | Task groups, variable groups |
| GitHub Actions | Reusable workflows (on: workflow_call), composite actions that bundle steps, and shared actions in a repository or the Marketplace. Organization rulesets can require specific workflows to pass |
Environments
An environment is a named target such as staging or production. A deployment job points at it with environment:. Environments record deployment history, can include resources (Kubernetes namespaces, virtual machines), and are where approvals and checks usually live. GitHub has the same concept with environments, secrets and protection rules.
Approvals and checks
 Checks are set on protected resources by the resource owner, not in the YAML: environments, service connections, repositories, variable groups, secure files and agent pools can all have checks. Before a stage that uses the resource runs, all checks must pass.
| Check | What it does |
|---|---|
| Approvals | Named users or groups must approve. If a group is the approver, one member is enough. The approvals have a timeout, and if it passes without a decision the stage is skipped |
| Branch control | Only allowed branches (full name such as refs/heads/main) may use the resource, optionally requiring branch protection |
| Business hours | The stage waits for a time window |
| Invoke Azure Function / Invoke REST API | Call your own logic and read the response |
| Query Azure Monitor alerts | Passes only if no alert rules are firing |
| Required template | The pipeline must extend a named template, forcing mandatory steps |
| Evaluate artifact | Checks a container image against a policy |
| Exclusive lock | Only one run uses the resource at a time. lockBehavior: runLatest (default) lets only the latest run proceed, and sequential queues all runs |
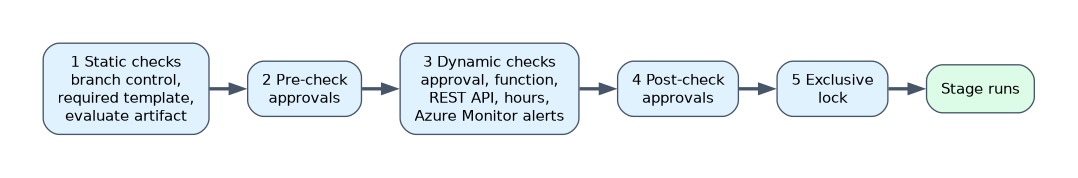
Evaluation order: static checks (branch control, required template, evaluate artifact), pre-check approvals, dynamic checks (approval, Azure Function, REST API, business hours, Azure Monitor alerts), post-check approvals, then the exclusive lock. An approver may also defer approval to a later time. Administrators of the resource can bypass some checks for a hotfix, and the bypass is logged.
A worked scenario
A security team needs every production deployment to run a mandatory scan. They create a secure-deploy.yml template with the scan and deploy steps, then add a Required template check to the production service connection, so any pipeline using it must extend that template. They add an approval by the release managers group and a branch control check for refs/heads/main. Pipeline authors can still use their own build steps but cannot remove the controls.
What to remember for the exam
- Templates: include (
template:) andextends:. Extends forces a structure. Parameters are compile time. - Variable groups live in the Library and can be linked to Key Vault. Mark secrets and map them to scripts explicitly.
- Task groups are classic. YAML uses templates. GitHub uses reusable workflows and composite actions.
- Checks sit on resources, not in YAML. Required template, branch control and approvals are common exam answers.
- Approval timeout skips the stage. One member of an approver group is enough.
Checks only apply to stages that use the protected resource. If a pipeline avoids the resource, the check never runs.
How the exam asks about this
- "Force every pipeline to include a vulnerability scan." Extends template with a required template check.
- "Reuse the same set of tasks in classic pipelines." A task group.
- "Share secrets from Key Vault with many pipelines." A variable group linked to Key Vault.
- "Only one deployment to production at a time." Exclusive lock.
Common mistakes
Copying steps between pipelines. Use templates.
Putting approvals in the YAML file. Approvals belong on the environment or resource.
Forgetting branch names must be fully qualified. Branch control needs refs/heads/main.
Thinking a template parameter changes at runtime. Template expressions resolve at compile time.
Check yourself
Which YAML keyword forces a pipeline to be based on a parent template?
extends.
On which kinds of resource can checks be configured?
Environments, service connections, repositories, variable groups, secure files and agent pools.
What happens to a stage when an approval times out?
The stage is skipped.
Topic 3 of 3 in Pipelines: design and implement pipelines
Test yourself on Pipelines: design and implement pipelines
The full Microsoft AZ-400 question bank has 766 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.