Develop a security and compliance plan · Topic 2 of 3
Managing Secrets and Secretless Authentication
AZ-400 secrets: Azure Key Vault in pipelines, variable groups, OIDC workload identity federation, secure files and preventing secret leaks.
- 6 min
- Includes a diagram
- Key Vault holds secrets, keys and certificates. Use RBAC roles, soft delete and purge protection.
AzureKeyVault@2and Key Vault linked variable groups bring secrets into Azure Pipelines. App Service uses Key Vault references.- OIDC federation removes stored secrets. GitHub needs
id-token: writeand a federated credential with an issuer and subject.
What it is
Pipelines need access to things that must stay private: passwords, API keys, certificates, signing keys. A secrets strategy decides where they live, how pipelines get them, who can read them and how to avoid leaks. The strongest strategy is secretless: nothing is stored, because the pipeline proves its identity with a short lived token instead.
How it works
Azure Key Vault
Azure Key Vault stores secrets, keys and certificates with access control and auditing.
| Feature | Notes |
|---|---|
| Access control | Azure RBAC is the recommended model, with roles such as Key Vault Secrets User (read secrets), Secrets Officer, Certificates Officer and Crypto User. Older access policies still exist |
| Protection | Soft delete and purge protection guard against accidental or malicious deletion |
| Network | Firewall rules and private endpoints |
| Rotation | Set expiry dates, and use Event Grid events such as near expiry to trigger rotation |
| Logging | Diagnostic logs go to Log Analytics for audit |
Ways pipelines use it:
- Azure Pipelines: the
AzureKeyVault@2task fetches chosen secrets into masked variables. A variable group linked to Key Vault does the same without a task. The service connection identity needs permission to get and list secrets. - GitHub Actions: sign in with
azure/login, then read the secret with the Azure CLI (az keyvault secret show), keeping it masked. - Applications at run time: App Service and Functions can use Key Vault references in app settings, written as
@Microsoft.KeyVault(SecretUri=...), and read through the app's managed identity. No secret is in the pipeline at all.
- task: AzureKeyVault@2
  inputs:
    azureSubscription: my-connection
    KeyVaultName: kv-prod-shop
    SecretsFilter: 'DbPassword,ApiKey'
    RunAsPreJob: false
Secretless authentication with OpenID Connect
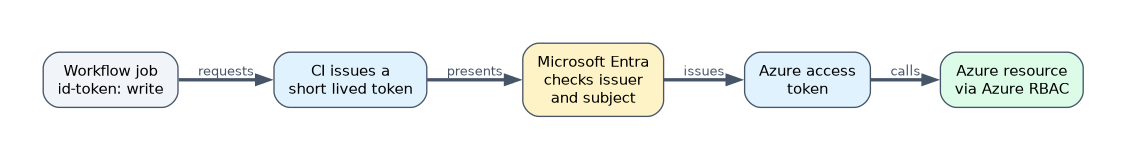 Workload identity federation lets a pipeline exchange the token issued by the CI system for an Azure access token. Azure trusts the CI system's issuer and checks the subject claim, so no client secret is stored.
| Platform | How it is set up |
|---|---|
| GitHub Actions | Create a federated credential on an app registration or a user-assigned managed identity. The issuer is https://token.actions.githubusercontent.com. The subject names the repository and the branch, tag, pull request or environment, such as repo:contoso/shop:environment:production. The workflow needs permissions: id-token: write and signs in with azure/login using the client ID, tenant ID and subscription ID only |
| Azure Pipelines | Create an Azure Resource Manager service connection with workload identity federation (automatic or manual). The subject identifies the organization, project and service connection |
permissions:
  id-token: write
  contents: read
steps:
- uses: azure/login@v2
  with:
    client-id: ${{ vars.AZURE_CLIENT_ID }}
    tenant-id: ${{ vars.AZURE_TENANT_ID }}
    subscription-id: ${{ vars.AZURE_SUBSCRIPTION_ID }}
Benefits: nothing to store, rotate or leak; tokens are short lived; and the subject lets you say "only the production environment of this repository" can sign in.
Secure files and sensitive files during deployment
Secure files in the Azure Pipelines Library store certificates, SSH keys and signing profiles encrypted. A pipeline downloads one with DownloadSecureFile@1, the file exists only for that job, and you can add approvals and checks and limit which pipelines may use it. In GitHub store small files as secrets (for example Base64 encoded) or, better, fetch them from Key Vault at deploy time. Delete the file when the job finishes and never write it into the artifact.
Preventing leakage
| Risk | Control |
|---|---|
| Secret printed in logs | Mark variables as secret so they are masked. Masking is not perfect, because transformed values (Base64, split strings) may not match, so do not echo secrets |
| Secret passed on a command line | Process lists and logs can show arguments. Pass secrets through environment variables or files |
| Secret exposed to untrusted code | Do not expose secrets to pull requests from forks. Be careful with triggers such as pull_request_target |
| Script injection | In GitHub, do not place untrusted text such as an issue title directly in a run: script. Pass it as an environment variable |
| Overpowered token | Set permissions: to the minimum and limit the job authorization scope in Azure DevOps |
| Third party actions or tasks | Pin to a full commit SHA (or a verified version), and allow only approved actions |
| Secrets committed to code | Secret scanning and push protection |
| Standing credentials | Short lived tokens, rotation and expiry dates |
Store secrets at the narrowest scope: environment secrets (available only to jobs that target that environment and pass its rules) are better than repository secrets, which are better than organization secrets. In Azure DevOps use variable groups with checks or Key Vault.
Choosing quickly
| Requirement | Answer |
|---|---|
| A pipeline deploys to Azure with no stored credential | Workload identity federation |
| Share secrets with many pipelines and rotate in one place | Variable group linked to Key Vault |
| App reads its secrets itself at run time | Key Vault reference and managed identity |
| Store a signing certificate for a build | Secure file, or Key Vault |
| Stop credentials being committed | Secret scanning with push protection |
A worked scenario
A GitHub workflow deploys to Azure with a client secret stored as a repository secret. Security wants it removed. The team creates a federated credential on a user-assigned managed identity with a subject for the production environment, gives the identity a narrow role on one resource group, sets id-token: write, and signs in with azure/login using only IDs. The app reads database passwords through Key Vault references, and the old secret is deleted.
What to remember for the exam
- Key Vault holds secrets, keys and certificates. Use RBAC roles, soft delete and purge protection.
AzureKeyVault@2and Key Vault linked variable groups bring secrets into Azure Pipelines. App Service uses Key Vault references.- OIDC federation removes stored secrets. GitHub needs
id-token: writeand a federated credential with an issuer and subject. - Secure files are encrypted in the Library and downloaded with
DownloadSecureFile@1. - Do not expose secrets to fork pull requests. Pin third party actions.
A masked value is still readable by anyone who can edit the pipeline and print a transformed version of it. Limit who can change pipelines that use secrets.
How the exam asks about this
- "Remove the client secret from the GitHub Actions deployment." Federated credential with OIDC.
- "Sign in only from the production environment." Federated credential subject that names the environment.
- "A web app should read secrets without them appearing in the pipeline." Key Vault references with a managed identity.
- "Store a certificate that the build needs." A secure file or Key Vault.
Common mistakes
Forgetting id-token: write. The OIDC sign in fails with no token.
Subject mismatch. The branch, environment or repository in the credential must match the workflow.
Printing secrets to debug. Masking is not a safety net.
Granting Key Vault access to everyone. Give each identity only the read role it needs.
Check yourself
Which GitHub workflow permission is required to request an OIDC token?
id-token: write.
Which Azure Pipelines task fetches Key Vault secrets into variables?
AzureKeyVault@2.
What lets an App Service app setting read a Key Vault secret without storing it?
A Key Vault reference, resolved through the app's managed identity.
Topic 2 of 3 in Develop a security and compliance plan
Test yourself on Develop a security and compliance plan
The full Microsoft AZ-400 question bank has 766 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Microsoft. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.