Trust and Security with Google Cloud · Topic 4 of 5
Threat Intelligence and Security Operations
Google Threat Intelligence and its sources, Security Command Center for posture and risk, and Google Security Operations for detection and response.
- 4 min
- Includes a diagram
- Google Threat Intelligence: proactive insight from Google's visibility, Mandiant expertise and VirusTotal's community.
- Security Command Center: discover, prioritize and remediate risks and misconfigurations in Google Cloud.
- Google Security Operations: unified SIEM and SOAR platform to ingest telemetry and accelerate detection and response.
What it is
Three Google offerings help organizations find and stop threats. Google Threat Intelligence tells you what attackers are doing. Security Command Center shows the risks and misconfigurations in your Google Cloud environment. Google Security Operations is a unified platform to collect security telemetry, detect threats and respond to them.
How it works
Google Threat Intelligence
Threat intelligence is knowledge about attackers, their tools and methods, and signs of attack. Google Threat Intelligence gives organizations proactive insights so they can prepare before an attack reaches them. The exam names its unique sources:
| Source | What it contributes |
|---|---|
| Google's vast global visibility | Insight from protecting billions of users and devices across Google's products |
| Mandiant's frontline incident response expertise | Knowledge from Mandiant experts who respond to major breaches around the world |
| VirusTotal's crowdsourced threat detection | A large community that submits and analyzes suspicious files and URLs |
The combination gives a broad and current picture of threats, such as which groups target your industry and which indicators to block.
When a question lists Mandiant and VirusTotal as sources, the answer is Google Threat Intelligence.
Security Command Center
Security Command Center is Google Cloud's security and risk management platform for Google Cloud environments. It helps organizations proactively discover, prioritize and remediate security risks.
| Capability | Business value |
|---|---|
| Asset discovery | See every Google Cloud resource and its security state in one place |
| Misconfiguration detection | Find risky settings such as public buckets or open firewall ports |
| Vulnerability detection | Find known software vulnerabilities in workloads |
| Threat detection | Detect active threats such as cryptomining or suspicious account activity |
| Prioritization | Rank risks, for example by showing how an attacker could reach high-value resources, so teams fix what matters first |
| Compliance monitoring | Check the environment against security standards |
| Remediation guidance | Clear steps to fix each finding |
Google Security Operations
Google Security Operations (Google SecOps) is a unified security operations platform. It brings together:
| Function | What it does |
|---|---|
| SIEM (security information and event management) | Ingests and stores large volumes of security telemetry (logs and events) from cloud, on premises and other sources, and searches it fast |
| Detection | Applies rules and threat intelligence to spot attacks |
| SOAR (security orchestration, automation and response) | Automates and coordinates response steps through playbooks |
| AI assistance | Gemini helps analysts search, summarize and investigate |
The business value: faster detection and response, less manual work for the security team, and one place to see threats across the organization instead of many separate tools.
How they work together
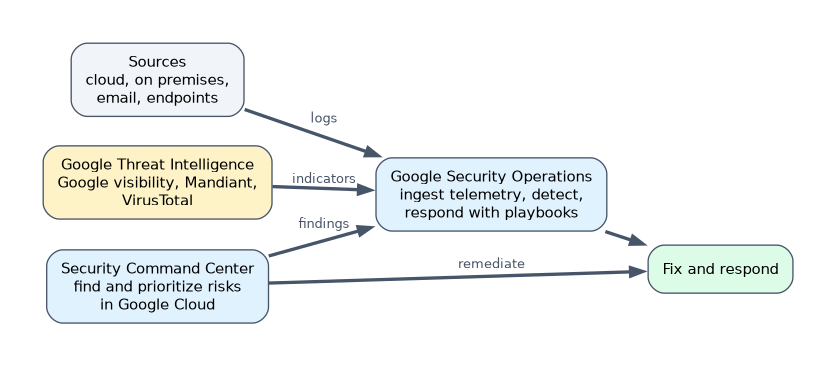
| Question | Offering |
|---|---|
| Who is attacking organizations like ours, and how? | Google Threat Intelligence |
| What is misconfigured or vulnerable in our Google Cloud environment? | Security Command Center |
| Is an attack happening across our systems now, and how do we respond? | Google Security Operations |
A worked scenario
A retailer learns from Google Threat Intelligence that a ransomware group is targeting retail companies using a specific phishing technique. Security Command Center shows that one of its Google Cloud projects has a VM with a known vulnerability exposed to the internet, so the team fixes it first. Google Security Operations ingests logs from its stores, cloud and email, detects a suspicious login linked to the group's indicators, and a playbook automatically disables the account.
How the exam asks about this
- "Proactive insight into threats, drawing on Mandiant and VirusTotal." Google Threat Intelligence.
- "Find and prioritize misconfigurations and vulnerabilities in Google Cloud." Security Command Center.
- "Ingest telemetry from many sources and speed up detection and response." Google Security Operations.
What to remember for the exam
- Google Threat Intelligence: proactive insight from Google's visibility, Mandiant expertise and VirusTotal's community.
- Security Command Center: discover, prioritize and remediate risks and misconfigurations in Google Cloud.
- Google Security Operations: unified SIEM and SOAR platform to ingest telemetry and accelerate detection and response.
- They answer different questions: who attacks, what is weak, what is happening now.
Security Command Center focuses on the Google Cloud environment's posture and threats. Organization-wide log analysis and response is Google Security Operations.
Common mistakes
Confusing Security Command Center with Google Security Operations. One manages cloud risk posture; the other runs detection and response across all telemetry.
Thinking threat intelligence blocks attacks by itself. It informs detection and defense; other tools act on it.
Forgetting VirusTotal's role. It is the crowdsourced source in Google Threat Intelligence.
Check yourself
Which three sources power Google Threat Intelligence?
Google's global visibility, Mandiant's frontline incident response expertise and VirusTotal's crowdsourced threat detection.
Which offering finds and prioritizes misconfigurations in Google Cloud?
Security Command Center.
What does Google Security Operations do?
It ingests security telemetry from many sources and speeds up threat detection and response in one platform.
Topic 4 of 5 in Trust and Security with Google Cloud
Test yourself on Trust and Security with Google Cloud
The full Google Cloud Digital Leader question bank has 512 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by Google Cloud. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.