Network Perimeter Protection · Topic 4 of 6
Firewall Concepts, Types, Topologies and Placement
Understand what firewalls can and cannot do, the main firewall technologies, topologies like bastion host and screened subnet, and host or network types.
- 5 min
- Includes a diagram
- Packet filtering is stateless, and stateful inspection tracks sessions.
- Application level gateways (proxies) inspect content at layer 7.
- A bastion host is a hardened, exposed server.
What it is
A firewall enforces a set of rules about which traffic may pass between networks of different trust. It sits at a boundary, such as between the internet and the company, and permits or blocks traffic by address, port, protocol, session state or content.
The exam asks what a firewall can and cannot stop, which technology fits a need, and how firewalls are arranged.
How it works
Capabilities, concerns and limitations
| Firewalls can | Firewalls cannot |
|---|---|
| Block unwanted ports, protocols and addresses | Stop an insider already inside the network |
| Hide internal addresses with NAT | Stop traffic that never crosses them, such as a rogue modem or Wi-Fi |
| Log and alert on connections | Inspect encrypted traffic unless they decrypt it |
| Separate zones such as the DMZ | Fix a flaw in an allowed application |
| Terminate VPNs and enforce policy | Stop malware that arrives over an allowed channel without scanning |
| Perform authentication of users | Protect against a bad rule set or misconfiguration |
Concerns include a single point of failure, performance limits under heavy load, rule complexity, and the false sense of safety that a firewall can give. A firewall is one layer, not the whole defense.
Firewall technologies
| Technology | OSI layer | How it decides | Notes |
|---|---|---|---|
| Packet filtering (stateless) | Network and transport (3 and 4) | Checks each packet against rules for address, port and protocol | Fast and simple. No memory of sessions. |
| Stateful inspection | 3 and 4 | Tracks connection state in a table and allows replies to permitted sessions | Common standard. Blocks unsolicited inbound replies. |
| Circuit level gateway | Session (5) | Checks that the TCP handshake and session are valid, then relays | Hides internal hosts. Does not read content. |
| Application level gateway (proxy firewall) | Application (7) | Acts as a proxy, understands the protocol and inspects content | Slower but deeper. One proxy per protocol. |
| Next generation firewall (NGFW) | Up to 7 | Adds application awareness, user identity, IPS and threat feeds | Controls by application, not just port |
| Web application firewall (WAF) | 7 | Inspects HTTP and HTTPS for attacks such as SQL injection | Protects web apps, complements a network firewall |
| Network address translation (NAT) device | 3 | Translates addresses between private and public | Hides internal structure but is not a full security control |
| VPN firewall | 3 and up | Terminates VPN tunnels and filters decrypted traffic | Used for remote access |
A stateful firewall is the typical answer when a scenario says "allow return traffic for connections started inside". A proxy is the typical answer for "inspect the content of a protocol and hide the clients".
Firewall topologies
| Topology | Description | Use |
|---|---|---|
| Bastion host | A hardened host exposed to the untrusted network, running only needed services | Public web or mail server |
| Screened host | A packet filtering router in front of a bastion host | Simple small network |
| Multi homed (dual homed) firewall | One firewall with two or more network interfaces | Separate internal, external and DMZ on one device |
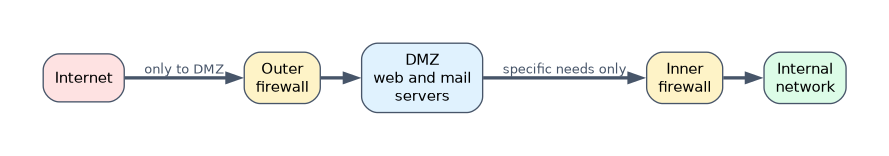
| Screened subnet (DMZ) | Two firewalls, or one with a third interface, with public servers in a buffer zone | Standard design for internet facing services |
| Back to back (two layer) | An outer firewall and an inner firewall, ideally from different vendors | Higher assurance |
In a screened subnet, the outer firewall allows the internet to reach only the DMZ servers, and the inner firewall allows the DMZ to reach the internal network only for specific needs. A compromised DMZ server still has no free path to the internal network.
Hardware, software, host, network, internal and external firewalls
| Pair | Meaning |
|---|---|
| Hardware firewall | A dedicated appliance with its own operating system. Fast and robust, protects a whole network. |
| Software firewall | A program on a general purpose computer or virtual machine. Flexible and cheaper. |
| Host based firewall | Runs on one endpoint and protects only that device, even on any network |
| Network based firewall | Sits at a network boundary and protects all hosts behind it |
| External (perimeter) firewall | Faces the internet and filters outside traffic in |
| Internal firewall | Sits between internal zones and limits movement inside, for example in front of a data center |
Use both: network firewalls protect groups of devices, and host firewalls protect a laptop when it leaves the office.
A worked example
A company hosts a customer web portal and also runs an internal database. The design uses an outer firewall that allows only HTTPS to the portal server in the DMZ. An inner firewall allows only the portal server to ask the database over its single database port.
If the portal is compromised, the attacker can reach only that database port, not the rest of the internal network. The internal firewall in front of the database zone also logs this attempt.
How the exam asks about this
- "Which firewall type tracks the state of connections in a table?" → Stateful inspection.
- "Which topology places public servers between two firewalls?" → A screened subnet, or DMZ.
- "Which firewall protects a roaming laptop on a hotel network?" → A host based firewall.
What to remember for the exam
- Packet filtering is stateless, and stateful inspection tracks sessions.
- Application level gateways (proxies) inspect content at layer 7.
- A bastion host is a hardened, exposed server.
- A screened subnet (DMZ) isolates public servers from the internal network.
- Firewalls cannot stop insiders, bypass paths or encrypted threats they cannot see.
NAT is not a firewall. It hides internal addresses, but without filtering rules it does not decide which traffic is allowed.
Common mistakes
Choosing packet filtering for content checks. A stateless filter sees only headers, so it cannot read an HTTP request for an attack.
Treating the DMZ as a part of the internal network. It is a separate zone with its own limited rules.
Using only a perimeter firewall. Insiders and laptops need internal and host firewalls.
Check yourself
What is the difference between stateless and stateful filtering?
Stateless checks each packet alone, while stateful remembers connection state and allows only valid replies.
What is a bastion host?
A hardened host exposed to an untrusted network, running only the services it needs.
Why use an internal firewall?
To limit movement between internal zones if one is compromised.
Topic 4 of 6 in Network Perimeter Protection
Test yourself on Network Perimeter Protection
The full EC-Council 312-38 question bank has 800 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.