Incident Prediction · Topic 2 of 4
Vulnerability Management, Assessment, Scanning and PIA
Learn the vulnerability management program, vulnerability assessment and scanning, CVSS scoring and the Privacy Impact Assessment for the CND 312-38 exam.
- 5 min
- Includes a diagram
- Vulnerability management is continuous: discover, scan, prioritize, fix, verify.
- Credentialed scans are more accurate than non credentialed scans.
- CVE names a flaw, CVSS scores it, and a scan finds it.
What it is
Vulnerability management is the continuous process of finding, ranking, fixing and verifying weaknesses before an attacker uses them. Vulnerability assessment is the activity of finding and rating weaknesses, usually with a scanner.
A Privacy Impact Assessment (PIA) is a different review: it studies how a project collects and uses personal information and what it means for the privacy of the people involved.
How it works
The vulnerability management program
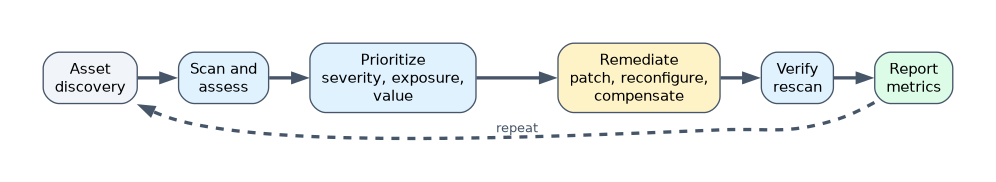
| Stage | Activity |
|---|---|
| Asset discovery | Know every system, because you cannot protect what you do not know |
| Scanning and assessment | Test systems for known weaknesses |
| Prioritization | Rank by severity, exposure and business value |
| Remediation | Patch, reconfigure, or apply a compensating control |
| Verification | Rescan to confirm the fix |
| Reporting and metrics | Show trends and time to fix |
| Continuous cycle | Repeat on a schedule and after changes |
Patch management is the part of remediation that applies vendor updates: test, deploy in stages, and verify. When a patch is not possible, use a compensating control such as isolating the system or adding a firewall rule.
Vulnerability assessment and scanning
A vulnerability scanner probes hosts, applications or containers and compares what it finds with a database of known flaws.
| Scan type | Description |
|---|---|
| Network scan | Finds open ports, services and weaknesses on hosts |
| Web application scan | Tests a web app for flaws such as injection and misconfiguration |
| Credentialed (authenticated) | Logs in to the target for accurate results, including missing patches |
| Non credentialed | Sees only what an outsider sees. Less accurate |
| Internal and external | From inside the network and from the internet |
| Agent based | Software on the host reports its state |
Credentialed scans give fewer false positives and a deeper view. A false positive is a finding that is not real, and a false negative is a real weakness the scanner missed.
Common reference systems:
| Item | Purpose |
|---|---|
| CVE | Unique ID for a publicly known vulnerability |
| CWE | List of types of software weakness |
| NVD | US database that adds CVSS scores to CVEs |
| CVSS | Scoring system for severity from 0.0 to 10.0 |
| CISA KEV | List of vulnerabilities known to be exploited |
| EPSS | Estimate of the chance a vulnerability will be exploited |
CVSS severity ratings:
| Score | Rating |
|---|---|
| 0.0 | None |
| 0.1 to 3.9 | Low |
| 4.0 to 6.9 | Medium |
| 7.0 to 8.9 | High |
| 9.0 to 10.0 | Critical |
A score alone is not enough. A medium score on an internet facing server holding sensitive data, or a flaw known to be exploited now, may come before a higher score on an isolated test machine.
A vulnerability assessment lists weaknesses. A penetration test goes further and tries to exploit them to show real impact.
Privacy Impact Assessment (PIA)
A PIA identifies how personal data (PII) flows through a system and what risks that creates for individuals. Under GDPR a similar duty is called a data protection impact assessment (DPIA) and is required when processing is likely to cause high risk to people. US federal agencies must perform PIAs for systems that collect personal information.
| PIA question | Why |
|---|---|
| What personal data is collected? | Limit collection to what is needed |
| Why, and under what legal basis? | Purpose must be clear and lawful |
| Where is it stored, who can access it, who receives it? | Find exposure |
| How long is it kept and how is it deleted? | Retention limits |
| What are the risks to individuals? | Identity theft, misuse, discrimination |
| What controls reduce them? | Encryption, access control, minimization, consent |
When to do one: before launching a new system or process that handles personal data, and when a major change occurs. The result is a report with risks and recommended controls that management accepts or fixes before go live.
A worked example
A weekly authenticated scan finds a critical flaw (CVSS 9.8) on an internet facing web server and a medium flaw on an internal print server. The defender patches the web server first, since it is exposed and the rating is critical, and schedules the print server for the next window.
After patching, a rescan confirms the flaw is gone. Separately, before launching a new customer app that stores birth dates, the team runs a PIA that recommends encrypting the field and shortening retention.
How the exam asks about this
- "Which scan logs in to the target to give more accurate results?" → A credentialed (authenticated) scan.
- "Which score range is rated Critical in CVSS?" → 9.0 to 10.0.
- "Which assessment studies the privacy risk of a system that handles personal data?" → A Privacy Impact Assessment.
What to remember for the exam
- Vulnerability management is continuous: discover, scan, prioritize, fix, verify.
- Credentialed scans are more accurate than non credentialed scans.
- CVE names a flaw, CVSS scores it, and a scan finds it.
- A vulnerability assessment finds weaknesses, a penetration test exploits them.
- A PIA looks at risk to individuals' privacy before a system goes live.
A scanner result is not proof. Confirm important findings, because false positives waste time and false negatives leave gaps.
Common mistakes
Prioritizing by CVSS score only. Exposure, asset value and active exploitation also matter.
Scanning once a year. New flaws appear daily, so scanning must be regular.
Confusing a PIA with a risk assessment of the systems. A PIA focuses on the privacy of the individuals whose data is processed.
Check yourself
What is the difference between a CVE and CVSS?
A CVE is the identifier of a known vulnerability, and CVSS is the score of its severity.
Why use a credentialed scan?
It sees the system from inside, finds missing patches and gives fewer false positives.
When should a PIA be performed?
Before a new system or process that handles personal data goes live, and after major changes.
Topic 2 of 4 in Incident Prediction
Test yourself on Incident Prediction
The full EC-Council 312-38 question bank has 800 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.