Procedures and Methodology · Topic 8 of 11
eDiscovery and Preparing Images for Examination
Learn the eDiscovery flow, the EDRM cycle, metrics and cost control, then prepare and view forensic images safely on Windows, Linux and Mac workstations.
- 5 min
- Includes a diagram
- EDRM order: information governance, identification, preservation, collection, processing, review, analysis, production, presentation.
- A legal hold stops deletion once a dispute is anticipated.
- Cost falls by early scoping, deduplication and culling before review.
What it is
Electronic discovery (eDiscovery) is the legal process of identifying, preserving, collecting, reviewing and producing electronically stored information (ESI) for a lawsuit or investigation. It differs from forensics in goal: forensics reconstructs events, while eDiscovery produces relevant documents to the other side.
Once an image is collected, it must be prepared so it can be examined without being altered. The exam asks for the EDRM stages in order, what each does, and how to open an image safely.
How it works
eDiscovery process flow
In outline: a dispute is anticipated, a legal hold tells people to keep relevant data, the data is found and collected, filtered, reviewed by lawyers for relevance and privilege, and produced in an agreed format. Both sides usually discuss scope early. In US federal courts the rules for ESI are in the Federal Rules of Civil Procedure.
The EDRM cycle
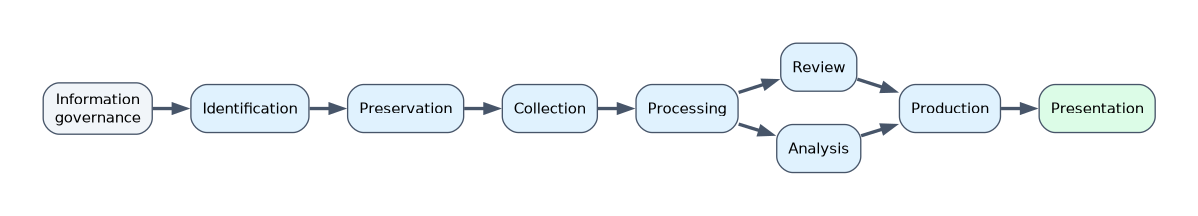 The Electronic Discovery Reference Model describes the stages.
| Stage | What happens |
|---|---|
| Information governance | Policies for retention and management of data before any dispute |
| Identification | Locate sources, custodians and data that may be relevant |
| Preservation | Issue the legal hold, stop deletion, protect from change |
| Collection | Gather the ESI in a forensically sound way |
| Processing | Extract text and metadata, remove duplicates, convert formats |
| Review | Examine documents for relevance, privilege and confidentiality |
| Analysis | Find patterns, key people and topics, evaluate content |
| Production | Deliver the documents in the agreed format |
| Presentation | Use the material at hearings, depositions or trial |
The volume of data gets smaller as stages progress, because each step filters.
Metrics and tracking
Accurate metrics keep cost and risk visible and defend the process if it is questioned.
- number of custodians and data sources, and data volume collected
- volume before and after processing and deduplication
- documents reviewed, responsive and privileged
- review speed and cost per document
- dates and people for each collection, with hash values
- a continuous chain of custody log
Collection methods
| Method | Description |
|---|---|
| Forensic collection | Bit stream image of media. Most complete, includes deleted data, higher cost. |
| Targeted collection | Specific files, mailboxes or folders chosen by custodian, date or keyword |
| Remote collection | Collected over the network by an agent or cloud connector |
| Self collection by custodian | Cheapest, but the least reliable because the custodian may alter metadata |
Pick the method to match the need. Self collection is risky because copying a file can change its dates.
Best practices to reduce cost and risk
- Issue the legal hold early and track acknowledgement.
- Limit scope by custodians, date range and keywords, and agree this with the other side.
- Deduplicate and cull before the expensive review stage.
- Use technology assisted review and analytics to prioritize documents.
- Keep the collection defensible: hashes, documented tools, chain of custody.
- Protect privileged material with a clawback agreement.
- Make good information governance a habit, so there is less to search.
Failure to preserve data can lead to sanctions, so risk grows when preservation is delayed.
Getting an image ready for examination
An image is prepared before analysis:
- Check the stored hash against a fresh hash of the image file.
- Make a working copy, and keep the master sealed.
- Open the image read only, or through a write blocker or software that mounts read only.
- Identify the partitions and the file systems.
- Record the tools used and the time.
For an image of a whole disk, find the partition start sector first. The Sleuth Kit command mmls image.dd lists the partition layout, and the offset is passed to later tools with -o.
Viewing an image on forensic workstations
| Platform | Typical approach |
|---|---|
| Windows | Mount in FTK Imager (read only), Arsenal Image Mounter, or open directly in the analysis suite |
| Linux | ewfmount for E01 files, then a read only loop mount such as mount -o ro,loop,noexec image.dd /mnt/evidence |
| Mac | hdiutil attach -readonly -nomount image.dmg for disk images, and tools such as Autopsy for raw images |
Mounting through the operating system can still have side effects, so use the ro option, plus noload on ext3 and ext4 so the journal is not replayed, and noexec to block execution. Better still, open the image in an analysis tool that never mounts it, since that avoids operating system side effects. Do not let the workstation auto mount or index the evidence.
A worked example
A company expects a lawsuit. Legal issues a hold to twelve custodians, and IT preserves mailboxes. A targeted collection pulls mail by date range. Processing removes duplicates and shrinks the set by half.
Reviewers mark privileged items. Separately, a disk image from an executive laptop is hash checked, mounted read only on a Linux workstation and examined with Autopsy.
How the exam asks about this
- "Which EDRM stage issues the legal hold?" → Preservation.
- "Why is custodian self collection risky?" → Copying can change metadata, and the process is not forensically sound.
- "How should an image be mounted for viewing?" → Read only.
What to remember for the exam
- EDRM order: information governance, identification, preservation, collection, processing, review, analysis, production, presentation.
- A legal hold stops deletion once a dispute is anticipated.
- Cost falls by early scoping, deduplication and culling before review.
- Verify the image hash before examining it, and work from a copy.
- Mount images read only, or use a tool that does not mount them.
Late preservation is a major eDiscovery risk. Lost data can lead to court sanctions even if the loss was not intentional.
Common mistakes
Mixing up forensics and eDiscovery goals. eDiscovery produces relevant documents for a legal process, not an event reconstruction.
Skipping the hash check. An image not verified before analysis cannot be shown to be unchanged.
Mounting read write by default. Even a simple mount can change timestamps or replay a journal.
Check yourself
What stage follows collection in the EDRM?
Processing.
What is a legal hold?
An instruction to preserve potentially relevant data and stop its routine deletion.
What does
mmlsshow?The partition layout of a disk image, including start sectors.
Topic 8 of 11 in Procedures and Methodology
Test yourself on Procedures and Methodology
The full EC-Council 312-49 question bank has 900 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.