Digital Evidence · Topic 2 of 8
Boot Processes and File Systems
Understand Windows, macOS and Linux boot, key Windows system files, NTFS, FAT, ext4 and APFS file systems, and macOS logs and directories for CHFI v11.
- 5 min
- Includes a diagram
- BIOS reads the MBR. UEFI reads the ESP, a FAT32 partition, on a GPT disk.
- Windows order: bootmgr, BCD, winload.exe, ntoskrnl.exe, smss.exe.
- pagefile.sys and hiberfil.sys can hold memory remnants.
What it is
The boot process loads an operating system from disk. The file system decides how files, metadata and deleted entries are stored. Both determine which artifacts exist and where, so an investigator needs to know them for every major platform.
The exam asks for the order of boot stages, the purpose of key system files, and the structures that distinguish NTFS, FAT, ext4 and APFS.
How it works
The general boot process
Power on starts the firmware. It runs the power on self test (POST), finds a boot device, and hands control to a boot loader. The loader starts the kernel, and the kernel starts the first user space processes.
Windows boot: BIOS with MBR
- BIOS runs POST and reads the first sector (the MBR) of the boot disk.
- MBR code finds the active partition and loads its boot sector.
- The boot sector loads bootmgr.
- Bootmgr reads the boot configuration data (BCD) store.
- winload.exe loads the kernel (ntoskrnl.exe), the hardware abstraction layer (hal.dll) and boot drivers.
- The kernel starts the session manager (smss.exe), which starts wininit.exe and winlogon.exe. Wininit starts services.exe and lsass.exe.
Windows boot: UEFI with GPT
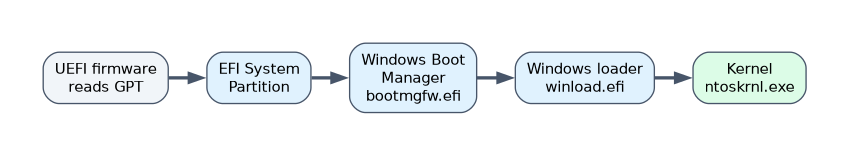 UEFI firmware reads the GPT and the EFI System Partition (ESP), a FAT32 partition. It runs the boot loader from there, typically \EFI\Microsoft\Boot\bootmgfw.efi, and the process continues with the BCD and winload as above. Secure Boot checks that loaders are signed.
Essential Windows system files
| File | Purpose and forensic value |
|---|---|
| bootmgr, BCD | Boot manager and its configuration |
| ntoskrnl.exe, hal.dll | Kernel and hardware abstraction |
| pagefile.sys | Virtual memory on disk. May hold fragments of RAM content. |
| hiberfil.sys | Hibernation image of RAM. A source of memory evidence. |
| swapfile.sys | Swap space for modern apps |
| Registry hives | SAM, SECURITY, SOFTWARE, SYSTEM and DEFAULT in Windows\System32\config, plus NTUSER.DAT per user |
| Event logs | Windows\System32\winevt\Logs |
macOS and Linux boot
| Stage | macOS (Intel) | macOS (Apple silicon) | Linux |
|---|---|---|---|
| 1 | Firmware (EFI) | Boot ROM | BIOS or UEFI |
| 2 | boot.efi loader | iBoot | GRUB loads from MBR or the ESP |
| 3 | XNU kernel | XNU kernel | Kernel image plus initramfs |
| 4 | launchd (PID 1) | launchd (PID 1) | systemd or init (PID 1) |
Linux GRUB configuration lives under /boot/grub or /boot/grub2. The kernel mounts the root file system and runs the init system, which brings up services by target or runlevel.
File systems
| File system | Key features for investigators |
|---|---|
| FAT12/16/32 | File allocation table, simple directory entries. FAT32 maximum file size is 4 GiB minus 1 byte. Deleted entries are marked by replacing the first filename character (0xE5), and the data usually remains until it is overwritten. |
| exFAT | Large files, used on flash media |
| NTFS | Master File Table ($MFT) with a record per file, resident data for tiny files, alternate data streams, $LogFile and $UsnJrnl journals, timestamps in both $STANDARD_INFORMATION and $FILE_NAME |
| ext2/3/4 | Inodes, superblock, block groups. ext3 and ext4 add a journal. ext4 uses extents and stores a creation time. |
| HFS+ | Older macOS file system, catalog file |
| APFS | Default on modern macOS and iOS. Containers, volumes sharing space, snapshots, clones, copy on write, native encryption, nanosecond timestamps. |
On ext3 and ext4, deleting a file clears block pointers in the inode, so recovery is harder than on ext2. Carving and journal analysis help.
macOS data, logs and directories
| Location | Content |
|---|---|
| /Users/name/Library | Per user preferences (plist files), caches, Mail, Messages and Safari data |
| /Library, /System | System wide settings and system files |
| /private/var/log | Traditional logs, such as system.log on older versions |
| /private/var/db/diagnostics | Unified logging data, read with the log command |
| /.fseventsd | File system events |
| Keychains | ~/Library/Keychains and /Library/Keychains |
| ~/.Trash | Deleted items |
| .DS_Store | Finder view settings that can reveal that a folder existed |
Property list files (plist) are XML or binary and are read with plutil. Time Machine backups and Spotlight metadata are also evidence sources.
A worked example
A Windows 11 PC does not boot after a suspected tampering. The investigator images the disk, sees a GPT with an ESP, and finds a modified file in the ESP boot folder.
Because UEFI loads from the ESP, a changed loader there can run before the operating system and its protections. The finding is recorded with hashes and timestamps.
How the exam asks about this
- "Which file holds the boot configuration of a modern Windows system?" → The BCD store.
- "Which Windows file contains a copy of RAM saved during hibernation?" → hiberfil.sys.
- "Which file system uses a Master File Table?" → NTFS.
What to remember for the exam
- BIOS reads the MBR. UEFI reads the ESP, a FAT32 partition, on a GPT disk.
- Windows order: bootmgr, BCD, winload.exe, ntoskrnl.exe, smss.exe.
- pagefile.sys and hiberfil.sys can hold memory remnants.
- NTFS keeps timestamps in $STANDARD_INFORMATION and $FILE_NAME and supports alternate data streams.
- APFS replaced HFS+ and adds snapshots, clones and native encryption.
hiberfil.sys exists only if hibernation or fast startup has written it. Do not assume it is present on every system.
Common mistakes
Swapping BIOS and UEFI components. The MBR code belongs to BIOS booting. The ESP and .efi files belong to UEFI.
Treating pagefile.sys as a log. It is memory overflow storage, useful for strings and fragments, not a record of events.
Assuming deleted ext4 files are as recoverable as FAT files. The inode pointers are cleared, so extra methods are needed.
Check yourself
Which Windows component reads the BCD?
The boot manager, bootmgr (bootmgfw.efi on UEFI systems).
What is the ESP?
The EFI System Partition, a FAT32 partition on a GPT disk that holds UEFI boot loaders.
Where does macOS keep its unified logging data?
In /private/var/db/diagnostics, read with the log command.
Topic 2 of 8 in Digital Evidence
Test yourself on Digital Evidence
The full EC-Council 312-49 question bank has 900 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.