Web Application Hacking · Topic 8 of 8
SQL Injection Tools, Evasion and Countermeasures
SQL injection tools such as sqlmap, how attackers try to evade filters and WAFs, and the countermeasures that actually stop SQL injection, in exam terms.
- 5 min
- Includes a diagram
- sqlmap is the main tool. Burp and ZAP help find injection points.
- Evasion: case variation, comments, encoding, concatenation, null bytes, parameter pollution.
- Blacklists and WAF rules are bypassable. Treat them as extra layers only.
What it is
SQL injection tools automate finding and using injection flaws. Evasion techniques try to slip input past filters, intrusion detection or a web application firewall (WAF). Countermeasures remove the flaw itself rather than trying to spot every bad input.
The key idea for the exam is that blacklists and filters can be evaded, while parameterized queries and least privilege cannot be argued with.
How it works
Tools
| Tool | What it does |
|---|---|
| sqlmap | Open source tool that automates detection and use of SQL injection, supports many databases and techniques |
| Havij | Older automated GUI tool, now historic |
| jSQL Injection | Java based tool for testing SQL injection |
| SQLNinja | Focuses on Microsoft SQL Server |
| Mole | Automated tool that detects and extracts through injection |
| Burp Suite and OWASP ZAP | Proxies with scanners that find injection points |
| Acunetix and similar scanners | Commercial web vulnerability scanners |
sqlmap is the one to know. It can detect which parameters are injectable, identify the database, list databases, tables and columns, and retrieve data. Its technique setting covers boolean based blind, error based, union query, stacked queries, time based blind and inline queries. It has "tamper" scripts that change how the payload is written, which relates to evasion. It must be used only against systems you are authorized to test.
Evasion techniques
Filters that look for known bad words or characters can be bypassed by changing the form of the input while keeping the same meaning to the database. The exam names the ideas.
| Technique | Idea |
|---|---|
| Case variation | Mixing upper and lower case so a case sensitive filter misses a keyword |
| Inline comments and whitespace changes | Using comments or alternative space characters inside the statement |
| URL, hex and Unicode encoding | Representing characters in another encoding that the application decodes later |
| String concatenation and building values | Assembling words from parts so no blocked word appears whole |
| Character functions | Using database functions that build text from character codes |
| Null bytes | Inserting a null byte to cut off a filter's view of the string |
| Obfuscated or encoded code | Hiding the query in a form the filter does not recognize |
| Parameter pollution | Sending the same parameter more than once so filter and application read different values |
| Splitting across inputs | Spreading the statement over several fields that are joined later |
| Slow or low volume testing | Staying below detection thresholds |
The lesson is that blacklisting is weak. A filter would have to anticipate every encoding, and an attacker needs only one that works.
Countermeasures
| Control | Why it helps |
|---|---|
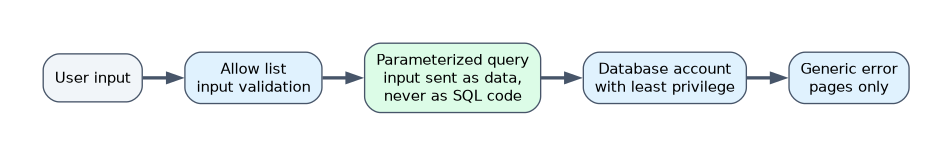
| Parameterized queries (prepared statements) | Keep data separate from SQL, which removes the root cause |
| Stored procedures, used safely | Reduce risk only when they themselves do not build SQL from strings |
| Input validation with an allow list | Accept only the expected type, length and format |
| Escaping, as a fallback | Helps in some legacy code but is easy to get wrong |
| Least privilege database accounts | The application account cannot drop tables or read unrelated data |
| Disable dangerous features | Turn off unneeded database functions such as command execution |
| Generic error messages | Hide database details from users |
| Web application firewall | Blocks known patterns as an extra layer |
| Object relational mapping (ORM) used correctly | Parameterizes by default |
| Testing and code review | SAST, DAST and scheduled penetration tests |
| Monitoring | Alert on database errors and unusual query patterns |
| Patching | Keep the database and drivers current |
Detection of attacks includes web server and WAF logs showing odd characters in parameters, repeated database errors, and long delays on certain requests. An intrusion detection system can add signatures but is not a cure.
A worked example
A security team adds a WAF rule that blocks a list of dangerous keywords, and the number of alerts falls. A tester then shows the same flaw is exploitable by using a different encoding of the input. The lasting fix is to change the code to use parameterized queries, and to reduce the database account to read access on the one table it needs.
How the exam asks about this
- "Which tool automates detection and exploitation of SQL injection across many databases?" -> sqlmap.
- "Mixing upper and lower case letters in keywords to bypass a filter is which evasion technique?" -> Case variation.
- "Which single measure best removes the root cause of SQL injection?" -> Parameterized queries (prepared statements).
What to remember for the exam
- sqlmap is the main tool. Burp and ZAP help find injection points.
- Evasion: case variation, comments, encoding, concatenation, null bytes, parameter pollution.
- Blacklists and WAF rules are bypassable. Treat them as extra layers only.
- Best fix: parameterized queries, allow list validation and least privilege.
- Hide database errors and monitor for patterns.
A WAF alone is not the right answer to "best way to prevent SQL injection". Choose parameterized queries.
Common mistakes
Trusting a keyword blacklist. Encoding and case changes defeat it.
Assuming stored procedures are always safe. They are safe only when they use parameters internally.
Running the application as database administrator. One flaw then gives full control.
Check yourself
Why is a blacklist weak against SQL injection?
Attackers can change case, encoding or structure, so a filter must anticipate every form while they need only one that passes.
Which sqlmap capability relates to evasion?
Tamper scripts that change how the injected input is written.
Which database account setting limits damage from a successful injection?
Least privilege, giving the application account only the rights it needs.
Topic 8 of 8 in Web Application Hacking
Test yourself on Web Application Hacking
The full EC-Council 312-50 question bank has 1,000 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.