Information Security and Ethical Hacking · Topic 2 of 3
Hacking Methodologies and Frameworks
Learn the Cyber Kill Chain, MITRE ATT&CK tactics, the Diamond Model, TTPs, indicators of compromise and the CEH hacking methodology in exam order.
- 5 min
- Includes a diagram
- The Kill Chain has seven stages, starting with Reconnaissance and ending with Actions on Objectives.
- Weaponization comes before Delivery, and Installation comes after Exploitation.
- ATT&CK separates tactics (goals) from techniques (methods).
What it is
A hacking methodology describes an attack as a series of stages. Defenders use these models to place what they see in the logs, decide where to break the attack, and speak a common language.
The exam focuses on four models: the CEH hacking methodology, the Lockheed Martin Cyber Kill Chain, the MITRE ATT&CK knowledge base and the Diamond Model of intrusion analysis.
How it works
The CEH hacking methodology
EC-Council arranges its course as a practical sequence. Each stage feeds the next.
This chapter's later pages follow the same order, so reconnaissance, scanning and enumeration come before vulnerability analysis and system hacking.
The Cyber Kill Chain
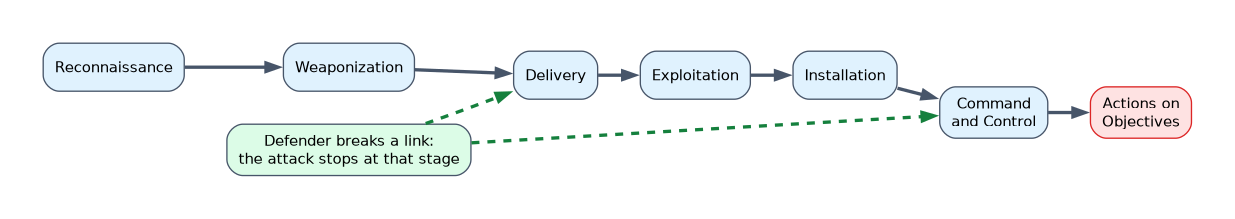 The Cyber Kill Chain, from Lockheed Martin, has seven stages. If a defender breaks a link, the attack can be stopped at that stage.
| Stage | What happens |
|---|---|
| Reconnaissance | The attacker researches the target |
| Weaponization | A deliverable, such as a document with malicious content, is prepared |
| Delivery | The package reaches the victim, for example by email or a web link |
| Exploitation | A vulnerability is triggered on the victim system |
| Installation | Malware or a backdoor is placed on the system |
| Command and Control | The attacker gets a remote channel to the compromised host |
| Actions on Objectives | The attacker achieves the goal, such as data theft |
MITRE ATT&CK
MITRE ATT&CK is a knowledge base of real-world adversary behavior. It is organized as tactics (the goal, the "why") and techniques (the way the goal is achieved, the "how"). Techniques can have sub-techniques.
The Enterprise matrix lists these tactics in order:
- Reconnaissance
- Resource Development
- Initial Access
- Execution
- Persistence
- Privilege Escalation
- Defense Evasion
- Credential Access
- Discovery
- Lateral Movement
- Collection
- Command and Control
- Exfiltration
- Impact
ATT&CK is not a strict sequence. An attacker may skip or repeat tactics, but the list is a handy reference for exam questions that name a tactic.
The Diamond Model
The Diamond Model describes every intrusion event with four features, drawn as the corners of a diamond.
| Feature | Meaning |
|---|---|
| Adversary | The actor behind the activity |
| Capability | The tools and techniques used |
| Infrastructure | The servers, domains and addresses used |
| Victim | The target |
Linking events through shared features lets analysts connect separate incidents to one adversary.
TTPs and indicators
TTPs are the tactics, techniques and procedures of an attacker. They describe behavior, which is harder for an attacker to change than a file name or an address.
Indicators of compromise (IoCs) are evidence that a breach happened or is happening, such as a file hash, a suspicious domain, an unusual outbound connection or a new account. Indicators of attack focus on the behavior and intent seen while an attack is underway.
Adversary behavior identification is the practice of spotting TTPs. Common behaviors defenders watch for include the following.
- Command and control over common protocols, such as web traffic or DNS.
- Use of web shells on servers.
- Unusual use of built-in tools such as scripting engines.
- Data staged in one place before it is sent out.
- Beaconing, a regular call back to the attacker.
A worked example
A user opens a spreadsheet from an email, a script runs, and a service is added so that it starts at each boot. Later the host calls out to an unfamiliar domain every minute. In the Kill Chain these map to Delivery, Exploitation, Installation and Command and Control. In ATT&CK they map to Initial Access, Execution, Persistence and Command and Control.
How the exam asks about this
- "Which Kill Chain stage creates the malicious document before it is sent?" -> Weaponization.
- "Which ATT&CK tactic describes keeping access after a reboot?" -> Persistence.
- "Which Diamond Model feature covers the attacker's servers and domains?" -> Infrastructure.
What to remember for the exam
- The Kill Chain has seven stages, starting with Reconnaissance and ending with Actions on Objectives.
- Weaponization comes before Delivery, and Installation comes after Exploitation.
- ATT&CK separates tactics (goals) from techniques (methods).
- The Diamond Model has adversary, capability, infrastructure and victim.
- TTPs describe behavior, while IoCs are artifacts of a compromise.
The Kill Chain stage is "Command and Control", while ATT&CK uses the same tactic name but has many more tactics, so check which model the question names.
Common mistakes
Mixing up tactics and techniques. A tactic is the goal, such as Persistence. A technique is how it is done, such as a scheduled task.
Placing Weaponization after Delivery. The attacker prepares the payload first and then sends it.
Treating the models as rival answers. They describe the same attack at different levels, and a question will name the model it wants.
Check yourself
Which Kill Chain stage follows Delivery?
Exploitation.
What are the four features of the Diamond Model?
Adversary, capability, infrastructure and victim.
What is the difference between an IoC and a TTP?
An IoC is a piece of evidence such as a hash or domain, while a TTP describes how the attacker behaves.
Topic 2 of 3 in Information Security and Ethical Hacking
Test yourself on Information Security and Ethical Hacking
The full EC-Council 312-50 question bank has 1,000 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.