Cryptography · Topic 2 of 3
PKI, Email Encryption and Disk Encryption
Understand PKI components such as CAs and certificates, email protection with PGP and S/MIME, and full disk encryption with BitLocker, VeraCrypt and LUKS.
- 5 min
- Includes a diagram
- A CA issues certificates, an RA verifies identity, a CRL or OCSP shows revocation.
- Certificates follow the X.509 standard.
- PGP uses a web of trust, and S/MIME uses CA issued certificates.
What it is
Public key infrastructure (PKI) is the system of people, software and rules that issues and manages digital certificates, so that public keys can be trusted. Email encryption protects messages in transit and at rest using certificates or keys. Disk encryption protects stored data if a device is lost or stolen.
The exam asks you to name PKI components, tell PGP from S/MIME, and match disk encryption tools to their platform.
How it works
PKI components
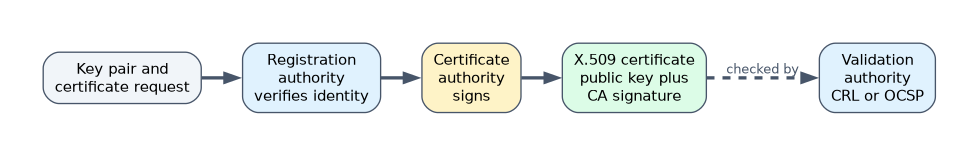
| Component | Role |
|---|---|
| Certificate authority (CA) | Issues and signs digital certificates. Trusted by clients. |
| Registration authority (RA) | Verifies the identity of the requester for the CA |
| Digital certificate | An X.509 document that binds a public key to an identity and carries a CA signature |
| Validation authority (VA) | Answers whether a certificate is still valid |
| Certificate revocation list (CRL) | A list of revoked certificates published by the CA |
| OCSP | Online Certificate Status Protocol. Real time checking of one certificate's status. |
| Certificate store | The place where trusted root certificates are kept |
| Key management and escrow | Generation, storage, rotation and recovery of keys |
A certificate contains the subject name, the public key, the issuer, validity dates, a serial number and the CA's digital signature. Trust flows from a root CA, through intermediate CAs, to the end entity. A self-signed certificate is signed by its own key, so no outside party vouches for it.
Trust models:
- Hierarchical: a root CA and subordinate CAs. Used by TLS on the web.
- Web of trust: individuals vouch for each other's keys. Used by PGP.
- Cross certification: two CAs trust each other.
When a browser opens an HTTPS site, it checks that the certificate chain leads to a trusted root, that the name matches, that it has not expired and that it is not revoked.
Email encryption
| Method | Trust model | Notes |
|---|---|---|
| PGP (Pretty Good Privacy) | Web of trust | Encrypts and signs messages and files. The open standard is OpenPGP. |
| GnuPG (GPG) | Web of trust | A free implementation of OpenPGP |
| S/MIME | Hierarchical, X.509 certificates from a CA | Built into many email clients, common in business |
Both use a hybrid approach: a random symmetric session key encrypts the message, and the recipient's public key encrypts that session key. A signature uses the sender's private key.
TLS between mail servers (STARTTLS) protects messages in transit between servers, but not on the servers themselves. End to end methods such as PGP and S/MIME protect the message content throughout.
Disk encryption
Full disk encryption (FDE) encrypts the whole volume, so data is unreadable without the key, even if the drive is removed.
| Tool | Platform | Notes |
|---|---|---|
| BitLocker | Windows | Often uses a Trusted Platform Module (TPM) to hold the key and check boot integrity |
| FileVault 2 | macOS | Full disk encryption |
| VeraCrypt | Cross platform | Open source successor to TrueCrypt. Creates encrypted volumes and encrypts partitions. |
| LUKS with dm-crypt | Linux | Standard disk encryption setup on Linux |
| Self encrypting drives | Hardware | The drive encrypts data itself |
Disk encryption protects data at rest only. When the system is running and unlocked, malware or a logged in attacker can read the data normally. A cold boot attack reads keys from memory shortly after power off, so physical access remains a risk.
A worked example
A laptop with confidential designs is stolen from a car. The disk was encrypted with BitLocker, the TPM was in use and a PIN was needed at boot.
The thief cannot read the drive by removing it, because the data is ciphertext. The company wipes the device remotely as a precaution and revokes the user's certificates. Without encryption, the same theft could be a reportable data breach.
How the exam asks about this
- "Which entity signs digital certificates?" → The certificate authority.
- "Which email standard uses a web of trust instead of a CA hierarchy?" → PGP.
- "Which tool encrypts a Linux disk through dm-crypt?" → LUKS.
What to remember for the exam
- A CA issues certificates, an RA verifies identity, a CRL or OCSP shows revocation.
- Certificates follow the X.509 standard.
- PGP uses a web of trust, and S/MIME uses CA issued certificates.
- BitLocker is Windows, FileVault is macOS, LUKS is Linux, VeraCrypt is cross platform.
- Disk encryption protects data at rest, not a running, unlocked system.
A CRL can be out of date. For current status, OCSP is the answer, and for a certificate that has expired, validity dates are checked.
Common mistakes
Confusing the RA and the CA. The RA checks identity. Only the CA signs the certificate.
Assuming encrypted disk equals safe laptop. An unlocked or sleeping machine may expose the key or data.
Treating STARTTLS as end to end encryption. It protects only the hop between servers.
Check yourself
What does a digital certificate bind together?
A public key and an identity, confirmed by the CA's signature.
How does PGP establish trust?
Through a web of trust, where users sign each other's keys.
What does full disk encryption protect against?
Reading data from a lost or stolen device, at rest.
Topic 2 of 3 in Cryptography
Test yourself on Cryptography
The full EC-Council 312-50 question bank has 1,000 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by EC-Council. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.