Networking and Content Delivery · Topic 3 of 6
Hybrid Connectivity with VPN and Direct Connect
Link on premises networks to AWS with Site to Site VPN and Direct Connect, learn virtual interfaces and gateways, and design resilient hybrid links.
- 5 min
- Includes a diagram
- A VPN connection has two tunnels for redundancy, and uses IPsec over the internet.
- The AWS side of a VPN is a virtual private gateway (one VPC) or a transit gateway (many VPCs).
- BGP gives dynamic routing, and route propagation updates VPC route tables.
What it is
Many companies keep part of their systems in their own data centers. Hybrid connectivity joins that network to a VPC so that both can talk using private addresses.
AWS offers two main ways. AWS Site to Site VPN builds encrypted tunnels over the internet, and AWS Direct Connect gives a dedicated private network link.
How it works
Site to Site VPN
A Site to Site VPN connection links a customer gateway (the router or firewall you own, or its representation in AWS) with an AWS gateway. The AWS side is either a virtual private gateway attached to one VPC, or a transit gateway for many VPCs.
Each connection has two tunnels, terminating in different Availability Zones, for redundancy. Traffic is encrypted with IPsec (Internet Protocol Security). Routing can be static or dynamic with BGP (Border Gateway Protocol), and dynamic is preferred because it adapts to failures.
For the VPC to learn routes from the VPN, enable route propagation on the subnet route tables, or add static routes.
A VPN can be created in minutes and costs little, but it uses the public internet, so performance varies.
AWS Direct Connect
Direct Connect is a dedicated network connection from your location to an AWS Direct Connect location. It gives more consistent latency and higher bandwidth than internet based links, and it can lower data transfer costs for large flows. Setting it up can take weeks, so it is not an emergency fix.
A connection carries one or more virtual interfaces (VIFs), which are VLANs.
| VIF type | Reaches |
|---|---|
| Private VIF | A VPC through a virtual private gateway or a Direct Connect gateway |
| Public VIF | AWS public services such as S3 over public IP addresses |
| Transit VIF | One or more transit gateways through a Direct Connect gateway |
A Direct Connect gateway lets one connection reach VPCs in several Regions and accounts. Direct Connect is not encrypted by default. To encrypt it, run an IPsec VPN over a public or transit VIF, or use MACsec on supported dedicated connections.
Comparing the options
| Question | VPN | Direct Connect |
|---|---|---|
| Path | Public internet | Private dedicated link |
| Encryption | IPsec built in | Not by default |
| Setup time | Minutes | Weeks |
| Performance | Variable | Consistent |
| Cost model | Low hourly plus data | Port hours plus data transfer |
Designing for resilience
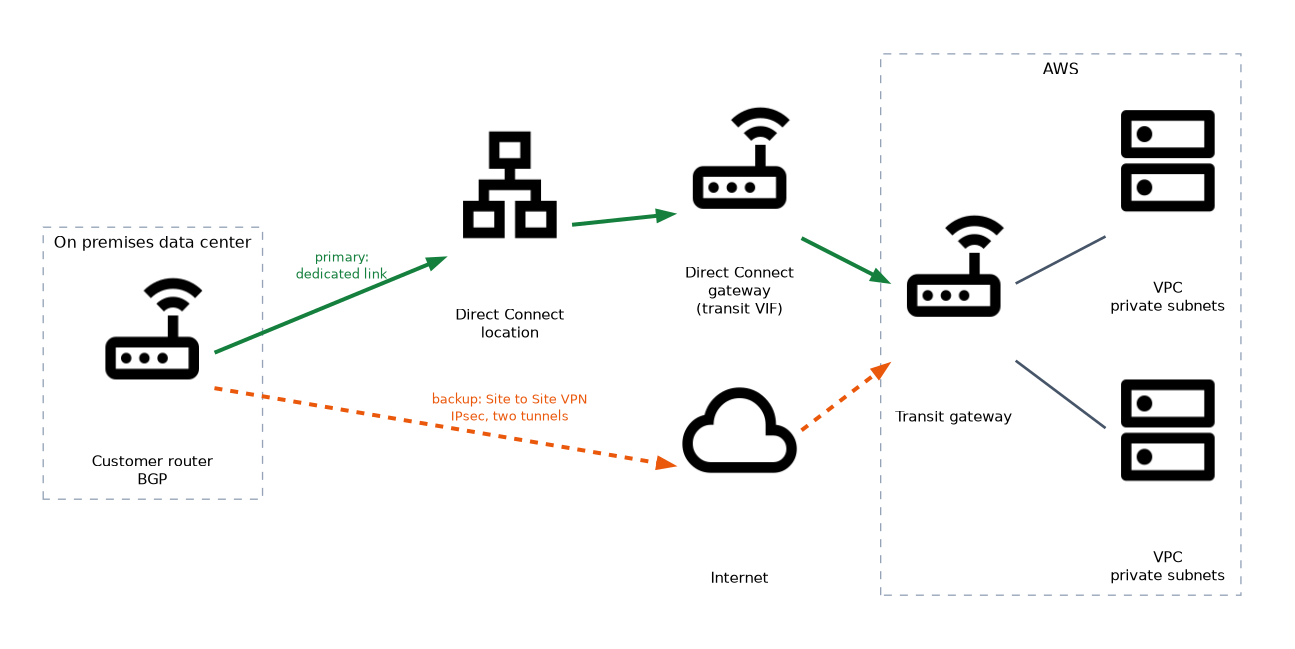 A single link is a single point of failure.
- For the highest resilience, use two Direct Connect connections at separate locations.
- A common lower cost design uses Direct Connect as the primary path and a Site to Site VPN as the backup. When both advertise the same prefix, AWS prefers Direct Connect.
- Use BGP so failover happens automatically.
Remote users
AWS Client VPN is a managed VPN service for individual users. It uses OpenVPN based clients and can authenticate with Active Directory, certificates or SAML, and it connects users to a VPC and, through it, to other networks.
Troubleshooting hybrid links
- VPN tunnel down: check the customer gateway settings, such as pre shared keys, IKE (Internet Key Exchange) parameters and the public IP address. Review VPN tunnel logs in CloudWatch.
- Tunnel up but no traffic: check route propagation or static routes on both sides, then security groups, network ACLs and on premises firewalls.
- BGP session down: check ASNs (autonomous system numbers), the neighbor IP and that the prefixes are advertised.
- Direct Connect VIF down: check the physical connection state, VLAN ID, and BGP settings with the provider.
# AWS CLI: view the state of VPN tunnels
aws ec2 describe-vpn-connections --vpn-connection-ids vpn-0123456789abcdef0"Quick, low cost, encrypted connection" is a Site to Site VPN. "Consistent performance, high bandwidth, private" is Direct Connect. "Direct Connect with a cheap backup" is a VPN.
What to remember for the exam
- A VPN connection has two tunnels for redundancy, and uses IPsec over the internet.
- The AWS side of a VPN is a virtual private gateway (one VPC) or a transit gateway (many VPCs).
- BGP gives dynamic routing, and route propagation updates VPC route tables.
- Direct Connect is a dedicated, private link with consistent performance and a long setup time.
- Direct Connect is not encrypted by default, so add IPsec VPN or MACsec when encryption is required.
- Private VIF reaches VPCs, public VIF reaches public AWS services, transit VIF reaches transit gateways.
- A Direct Connect gateway reaches VPCs across Regions.
- A VPN is the usual backup for Direct Connect.
- Client VPN serves individual remote users.
Common mistakes
Assuming Direct Connect is encrypted. It is private, not encrypted, unless you add encryption.
Planning Direct Connect for a deadline in days. Provisioning takes time. Use a VPN first.
Using only one tunnel. The second tunnel gives redundancy, and your device should be configured for both.
Forgetting route propagation. The tunnel is up, but the VPC has no routes toward the on premises network.
Overlapping on premises and VPC ranges. Routing cannot tell them apart.
Both VPN tunnels end on the same customer device in many designs, so that device is still a single point of failure. Use two devices for full resilience.
Check yourself
Quick questions.
A company needs an encrypted link in a day. What fits?
An AWS Site to Site VPN, which is encrypted with IPsec and can be created quickly.
Which VIF type reaches a VPC?
A private VIF, through a virtual private gateway or a Direct Connect gateway.
How can a Direct Connect link be backed up cheaply?
With a Site to Site VPN over the internet using BGP for failover.
Topic 3 of 6 in Networking and Content Delivery
Test yourself on Networking and Content Delivery
The full AWS SOA-C03 question bank has 850 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by AWS. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.