Design High Performing Architectures · Topic 5 of 7
VPC and Hybrid Connectivity
Connect VPCs and data centers with peering, Transit Gateway, PrivateLink, Site to Site VPN and Direct Connect, and pick the right option for each need.
- 5 min
- Includes a diagram
- VPC peering is one to one, not transitive, and needs non overlapping CIDR ranges.
- Transit Gateway is the scalable hub for many VPCs and hybrid links, with route tables for segmentation.
- PrivateLink exposes a service privately through interface endpoints, in one direction.
What it is
Real networks have many VPCs, accounts, Regions and an on premises data center. The exam asks how to connect them with the right balance of performance, security, scale and effort.
A Virtual Private Cloud (VPC) is a private network with a range of IP addresses in Classless Inter-Domain Routing (CIDR) notation. Plan the ranges early, because connecting networks with overlapping ranges is hard.
How it works
Connecting VPCs
| Option | How it works | Pick it when |
|---|---|---|
| VPC peering | A one to one link between two VPCs, in one or several Regions or accounts | A few VPCs need to talk, and cost and simplicity matter |
| AWS Transit Gateway | A regional hub that many VPCs and on premises links attach to | Many VPCs, hub and spoke design, central routing control |
| AWS PrivateLink | Exposes one service to consumers through an interface endpoint | Share a service with many VPCs or accounts without opening the whole network |
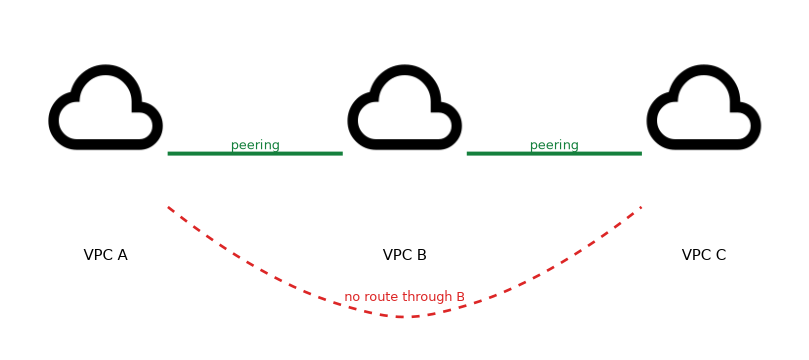
Peering is not transitive. If A peers with B and B peers with C, A cannot reach C through B. Peered VPCs also cannot have overlapping CIDR ranges. With many VPCs the number of peering links grows quickly, which is when Transit Gateway is the better answer.
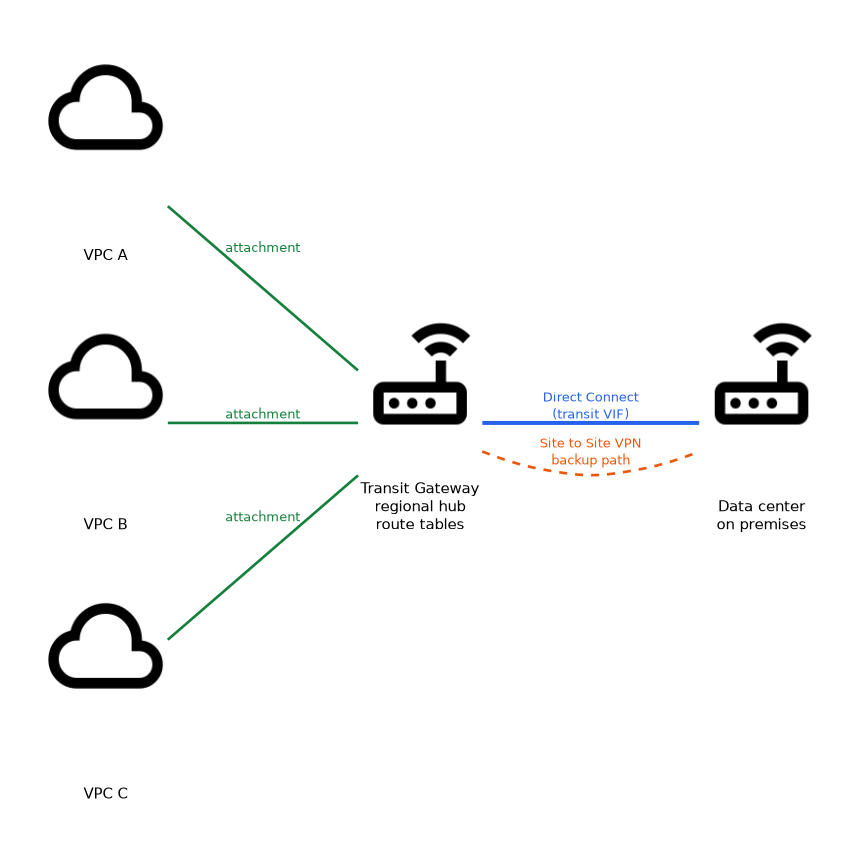
Transit Gateway supports route tables so you can separate, for example, production and test networks. It can connect VPCs, VPN connections and Direct Connect, and it can peer with Transit Gateways in other Regions.
PrivateLink works in one direction: consumers reach the service, and the provider cannot reach back into the consumer network. It is the standard way to offer a software as a service product to customers' VPCs, or to reach AWS services privately.
Connecting to AWS services privately
Gateway endpoints (S3 and DynamoDB) add a route and need no hourly fee. Interface endpoints use PrivateLink. Both keep traffic off the internet, which improves security and can avoid NAT gateway charges.
Hybrid connectivity
| Option | Path | Features |
|---|---|---|
| Site to Site VPN | Encrypted IPsec tunnels over the public internet | Fast to set up, two tunnels per connection for redundancy, variable internet performance |
| AWS Direct Connect | Dedicated private fiber link from your site to AWS | Consistent latency and higher bandwidth, but takes time to provision and is not encrypted by default |
| Direct Connect plus VPN | IPsec VPN running over Direct Connect | Private path with encryption |
| AWS Client VPN | OpenVPN based access for individual remote users | Remote workers reach VPC and on premises resources |
Direct Connect uses virtual interfaces: a private one reaches a VPC, a public one reaches public AWS services, and a transit one reaches a Transit Gateway. A Direct Connect gateway lets one connection reach VPCs in several Regions.
For high resilience, use two Direct Connect connections at different locations, or add a Site to Site VPN as a backup path. A quick start can use the VPN first and move to Direct Connect when it is delivered.
DNS across networks
Route 53 Resolver endpoints let on premises systems resolve AWS private names (inbound) and let VPC resources resolve names in your data center (outbound). Private hosted zones hold DNS records for names that only resolve inside chosen VPCs.
Network performance basics
Enhanced networking with the Elastic Network Adapter gives higher bandwidth and lower latency on supported instances. Placing instances in the same AZ, or in a cluster placement group, reduces latency between them. For traffic between AZs, remember that it adds a data transfer charge, which later pages cover.
"Many VPCs and on premises sites, simple central routing" means Transit Gateway. "Two VPCs only, lowest cost" means peering. "Consistent latency and bandwidth to the data center" means Direct Connect.
What to remember for the exam
- VPC peering is one to one, not transitive, and needs non overlapping CIDR ranges.
- Transit Gateway is the scalable hub for many VPCs and hybrid links, with route tables for segmentation.
- PrivateLink exposes a service privately through interface endpoints, in one direction.
- Site to Site VPN is encrypted, quick to deploy, and runs over the internet, with two tunnels per connection.
- Direct Connect is a dedicated link with consistent performance, takes time to provision and is not encrypted by default.
- Add a VPN over Direct Connect to encrypt traffic, or use a VPN as a backup path.
- A Direct Connect gateway reaches VPCs in multiple Regions.
- Route 53 Resolver endpoints connect DNS between VPCs and on premises networks.
Common mistakes
Expecting transitive routing through peering. Traffic cannot pass through a peered VPC to reach another one. Use Transit Gateway.
Choosing Direct Connect when speed to deploy matters. Provisioning takes time. A Site to Site VPN can be live quickly.
Assuming Direct Connect is encrypted. It is private but not encrypted unless you add IPsec VPN or another encryption layer.
Overlapping CIDR ranges. Two networks with the same range cannot be peered, and overlap complicates every other option.
A single VPN or a single Direct Connect link is a single point of failure. Questions about high availability expect a second link or a backup path.
Check yourself
Why can't VPC A reach VPC C through VPC B when A and C are both peered with B?
VPC peering is not transitive, so traffic does not pass through B.
Which option gives a private, consistent latency link to AWS but is not encrypted by default?
AWS Direct Connect.
Which service connects many VPCs and on premises networks through one hub?
AWS Transit Gateway.
Topic 5 of 7 in Design High Performing Architectures
Test yourself on Design High Performing Architectures
The full AWS SAA-C03 question bank has 823 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by AWS. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.