Configuration Management and IaC · Topic 4 of 5
Organizations, Control Tower and StackSets
Automate multi account and multi Region AWS setups with Organizations, service control policies, Control Tower Account Factory and StackSets.
- 5 min
- Includes a diagram
- SCPs limit; they never grant, and they do not apply to the management account.
- SCPs do apply to the root user of member accounts.
- Control Tower creates Log Archive and Audit accounts and uses SCPs, Config rules and Hooks for controls.
What it is
Large AWS estates use many accounts, because an account is the strongest isolation boundary for permissions, billing and blast radius. Doing that by hand does not scale, so the exam expects you to automate account creation, baseline setup and guardrails.
Three tools carry most of the load. AWS Organizations groups accounts, AWS Control Tower builds a governed landing zone on top of it, and CloudFormation StackSets push the same resources into many accounts and Regions.
How it works
AWS Organizations
An organization has a management account and member accounts arranged in organizational units (OUs). Policies attached to the root, an OU or an account are inherited downward.
| Policy type | Effect |
|---|---|
| Service control policy (SCP) | Sets the maximum permissions available in member accounts |
| Tag policy | Standardises tag keys and values |
| Backup policy | Applies AWS Backup plans across accounts |
| Resource control policy | Sets maximum permissions on resources in member accounts |
An SCP never grants anything on its own. An action is allowed only if the SCP and the identity or resource policy both allow it. SCPs affect every principal in member accounts, including the root user, but they do not affect the management account.
Many services support trusted access and a delegated administrator, so a security or tooling account manages the service for the organization and the management account stays out of daily work.
aws organizations create-account --email dev-team@example.com --account-name dev-teamAn account created this way gets a role named OrganizationAccountAccessRole by default, which the management account can assume.
AWS Control Tower
Control Tower sets up a landing zone, which is a multi account baseline that follows best practices. It creates a Log Archive account for central logs and an Audit account for security tooling, plus an organization wide CloudTrail trail and AWS Config recording. You pick a home Region and the governed Regions.
Controls (earlier called guardrails) are the rules that Control Tower applies.
| Control type | Mechanism | Example |
|---|---|---|
| Preventive | SCP | Deny disabling CloudTrail |
| Detective | AWS Config rule | Flag unencrypted volumes |
| Proactive | CloudFormation Hooks | Block a noncompliant resource before creation |
Account Factory provisions new accounts from a Service Catalog product with a standard baseline, and it can enroll existing accounts. Account Factory for Terraform (AFT) offers the same through a Terraform pipeline for teams that use Terraform. Customizations for Control Tower (CfCT) deploy extra SCPs and CloudFormation StackSets from a pipeline when a new account appears.
Landing zone drift occurs when someone moves accounts or edits managed resources, and Control Tower reports it for repair.
CloudFormation StackSets
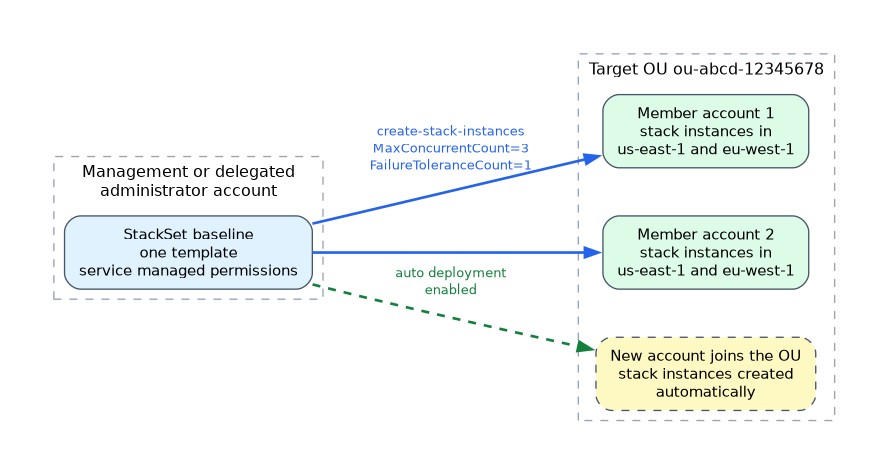 A StackSet deploys one template as stack instances across chosen accounts and Regions from a single administrator account.
| Permission model | Details |
|---|---|
| Service managed | Uses Organizations; targets OUs; can deploy automatically to new accounts in the OU |
| Self managed | You create an administration role and an execution role in each target account |
aws cloudformation create-stack-set --stack-set-name baseline \
  --template-body file://baseline.yaml --permission-model SERVICE_MANAGED \
  --auto-deployment Enabled=true,RetainStacksOnAccountRemoval=false \
  --capabilities CAPABILITY_NAMED_IAM
aws cloudformation create-stack-instances --stack-set-name baseline \
  --deployment-targets OrganizationalUnitIds=ou-abcd-12345678 \
  --regions us-east-1 eu-west-1 \
  --operation-preferences FailureToleranceCount=1,MaxConcurrentCount=3
Service managed StackSets need trusted access enabled once with aws cloudformation activate-organizations-access. A delegated administrator can run them so the management account does not have to, and then the commands use --call-as DELEGATED_ADMIN.
Operation preferences control the rollout: maximum concurrent accounts, failure tolerance, and the order of Regions. Use a small first batch so a bad template is caught early.
Multi Region patterns
Some services are Regional, so automation must repeat per Region. Examples are StackSets across Regions, ECR replication, multi Region KMS keys, Secrets Manager replication and a multi Region CloudTrail trail. Global services such as IAM need one deployment, usually in a single home Region.
Securing a new account
A typical baseline for every account contains an organization trail or Control Tower trail, AWS Config, GuardDuty and Security Hub enabled through their delegated administrators, a password and MFA policy, default EBS encryption, and SCPs that block risky actions such as leaving the organization.
What to remember for the exam
- SCPs limit; they never grant, and they do not apply to the management account.
- SCPs do apply to the root user of member accounts.
- Control Tower creates Log Archive and Audit accounts and uses SCPs, Config rules and Hooks for controls.
- Account Factory provisions accounts from a baseline; AFT and CfCT extend it.
- Service managed StackSets target OUs and can auto deploy to new accounts.
- Self managed StackSets need an administration role and execution roles.
- Use failure tolerance and concurrency to stage a StackSet rollout.
- Use a delegated administrator to keep day to day work out of the management account.
- Accounts made through Organizations have
OrganizationAccountAccessRole.
When a question asks for controls that apply automatically to every new account in an OU, think SCP on the OU plus an auto deploying service managed StackSet.
Common mistakes
Expecting an SCP to grant access. Without an IAM allow, the action is still denied.
Applying SCPs to the management account. They have no effect there, so keep workloads out of it.
Using self managed StackSets in an organization. Service managed mode removes the per account role setup.
Deploying everywhere at once. A faulty template then breaks every account together.
An SCP that denies too much can lock out your own automation roles, so test it on a sandbox OU first.
Check yourself
Can an SCP give a user permission to launch an instance?
No, an SCP only sets the ceiling, and an IAM policy must still allow the action.
Which Control Tower feature creates new governed accounts?
Account Factory, which provisions accounts with the standard baseline.
How does a StackSet reach new accounts automatically?
Service managed permissions with automatic deployment enabled on the target OU.
Topic 4 of 5 in Configuration Management and IaC
Test yourself on Configuration Management and IaC
The full AWS DOP-C02 question bank has 844 questions, with timed practice exams and an explanation for every answer.
This study guide is independent and is not affiliated with, endorsed by, or sponsored by AWS. Vendor names, certification names and exam codes are trademarks of their respective owners and are used for identification only.