MikroTik MTCUME Practice Exam
MikroTik Certified User Management Engineer (MTCUME)
The MikroTik Certified User Management Engineer (MTCUME) certification validates the ability to manage RouterOS networks at scale with centralized user authentication and secure remote access. It covers PPP profiles and secrets, PPTP/L2TP/PPPoE client and server setup, Layer 2 bridging over tunnels, IPsec VPN configuration, HotSpot deployment with multiple login methods, and RADIUS integration with User Manager.
Question bank updated : questions, answers, explanations and chapters.
Certification Overview
- Exam name: MTCUME
- Vendor: MikroTik
- Exam code: MTCUME
- Duration: 60 minutes
- Total questions: about 25
- Official passing score: 60% (source)
- Our practice exam pass mark: 60%
Who Should Take This Exam?
Network Engineer, Network Technician, Systems Administrator, Network Administrator, ISP Support Engineer, NOC Technician, Security Administrator, VPN Engineer
Prerequisites
Valid MTCNA certification or equivalent foundational RouterOS and networking knowledge.
Topics Covered
- PPP
- PPTP, L2TP
- PPPoE
- Bridging
- IPsec
- HotSpot
- RADIUS
Question Types
- Multiple Choice (Single Answer)
- Multiple Choice (Multiple Answers)
- True / False
- Scenario-Based
MTCUME Practice Questions
Our question bank contains 488+ practice questions for this certification. Sample questions from each exam chapter. Expand a question to see the answer choices. With full access, you get unlimited practice exams with randomised questions from our full question bank.
PPP
What is the primary purpose of a PPP Profile in MikroTik RouterOS?
- A. To monitor active PPP sessions in real time
- B. To configure PPP encryption algorithms
- C. To set default connection parameters such as local/remote addresses and DNS for PPP connections Correct answer
- D. To define firewall rules for PPP connections
Option C is correct because a PPP Profile in MikroTik RouterOS defines default connection parameters — including Local Address, Remote Address, DNS Server, Rate Limit, and session timeouts — that are applied to all PPP connections using that profile. Options A, B, and C describe other functions: session monitoring is under PPP Active, encryption is a profile sub-setting, and firewall rules are configured under /ip firewall.
Where are PPP client credentials (username and password) configured in MikroTik RouterOS?
- A. /system identity
- B. /ip address
- C. /ppp secret Correct answer
- D. /ip firewall filter
Option C is correct because /ppp secret is where PPP client credentials (username, password, service type, and optional per-user overrides) are configured. Options B, C, and D are unrelated menus — firewall filter handles packet filtering, system identity sets the router's hostname, and ip address manages interface IP assignments.
A PPP Secret's Remote Address setting overrides the PPP Profile's Remote Address.
- A. True Correct answer
- B. False
A PPP Secret's Remote Address takes precedence over the PPP Profile's Remote Address. MikroTik applies a hierarchy where Secret-level settings override Profile-level settings, allowing administrators to assign per-user static addresses while the Profile provides a default pool for other users.
Based on the topology shown, why does BR-A's PPP address stay the same after every reconnect while BR-B's can change?
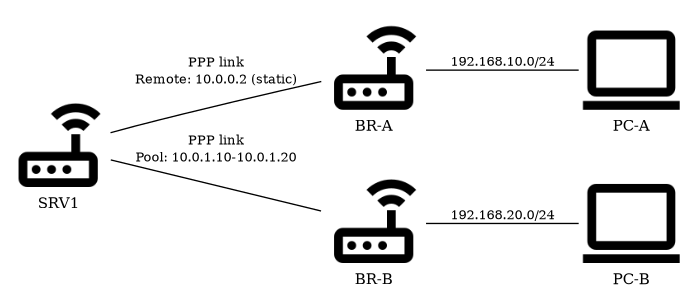
- A. BR-A's link uses IP Pool 10.0.1.10-10.0.1.20, while BR-B's Secret has a static Remote Address
- B. BR-A's PPP Secret has a static Remote Address (10.0.0.2), while BR-B's Profile draws from IP Pool 10.0.1.10-10.0.1.20 Correct answer
- C. The 192.168.10.0/24 network behind BR-A is statically routed, which fixes the PPP address
- D. Both BR-A and BR-B draw from the same IP Pool, but BR-A connects first
Option B is correct because BR-A's PPP Secret has a static Remote Address (10.0.0.2), so it receives the same address on every reconnect regardless of pool state. BR-B's Profile instead assigns from IP Pool 10.0.1.10-10.0.1.20, so its address can change between connections depending on which addresses are free. Options A and D reverse or misread which link uses the pool, and Option C is wrong because a statically routed LAN subnet has no effect on the PPP address assigned to the link itself.
PPTP, L2TP
Which transport protocol and port does PPTP use for its control connection?
- A. TCP port 1723 Correct answer
- B. UDP port 500
- C. TCP port 443
- D. UDP port 1701
Option A is correct because PPTP uses TCP port 1723 for its control connection to manage tunnel setup, maintenance, and teardown. UDP port 500 is used by IKE for IPsec, TCP port 443 is HTTPS/SSTP, and UDP port 1701 is used by L2TP.
Which transport protocol and port does L2TP use by default?
- A. TCP port 443
- B. UDP port 1701 Correct answer
- C. TCP port 1723
- D. UDP port 500
Option B is correct because L2TP uses UDP port 1701 by default for both its control and data channels. TCP port 1723 is used by PPTP, TCP port 443 is HTTPS/SSTP, and UDP port 500 is used by IKE for IPsec key exchange.
PPTP uses GRE for its data channel and TCP port 1723 for its control channel.
- A. True Correct answer
- B. False
PPTP uses two channels: a TCP connection on port 1723 for control messages (session setup, teardown, and management) and GRE (IP protocol 47) for encapsulating the actual PPP data frames. This dual-channel design is a defining characteristic of the PPTP protocol.
Using the topology shown, for BR-PC to reach 192.168.1.0/24 across the PPTP tunnel, what additional configuration is needed on BRANCH beyond the tunnel itself?
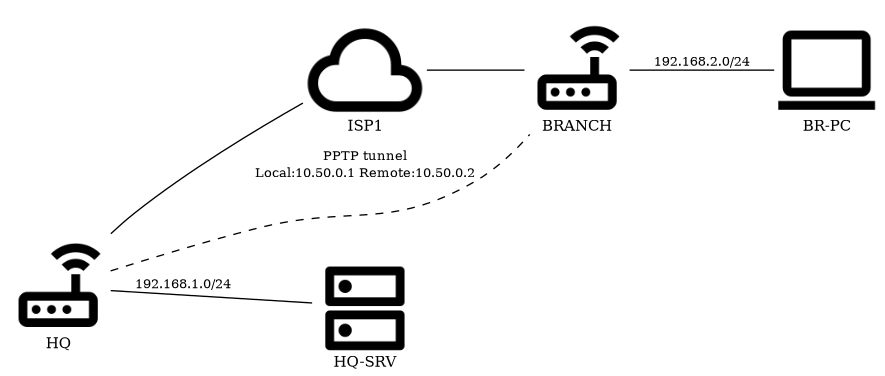
- A. A masquerade NAT rule on HQ for the tunnel interface
- B. A static route: dst-address=192.168.1.0/24 gateway=10.50.0.1 Correct answer
- C. Nothing further - the PPTP tunnel automatically advertises each side's LAN route
- D. A static route: dst-address=192.168.1.0/24 gateway=192.168.2.1
Option B is correct because a PPP-type tunnel only creates a route for the tunnel's own point-to-point addresses; reaching a LAN on the far side needs an explicit static route pointing at the remote tunnel address (10.50.0.1), which is HQ's side of the link. Option D is wrong because 192.168.2.1 is BRANCH's own LAN gateway, not a path toward HQ. Option C is wrong because PPTP tunnels never advertise routes automatically, and Option A (NAT) has nothing to do with basic reachability between the two LANs.
PPPoE
What does PPPoE stand for?
- A. Peer-to-Peer Protocol over Encryption
- B. Point-to-Point Protocol over EIGRP
- C. Point-to-Point Protocol over Ethernet Correct answer
- D. Point-to-Point Protocol over EoIP
Option C is correct because PPPoE stands for Point-to-Point Protocol over Ethernet, a protocol that encapsulates PPP frames within Ethernet frames. The other options contain fabricated expansions that do not represent any real protocol.
Which TWO messages are sent by the PPPoE client during the discovery phase? (Choose two)
- A. PADO (PPPoE Active Discovery Offer)
- B. PADS (PPPoE Active Discovery Session-confirmation)
- C. PADI (PPPoE Active Discovery Initiation) Correct answer
- D. PADR (PPPoE Active Discovery Request) Correct answer
Options C and D are correct because during PPPoE discovery the client sends the PADI broadcast to locate Access Concentrators and then sends the PADR unicast to select a specific server. PADO and PADS are sent by the server (Access Concentrator) in response.
Bridging
What is the primary purpose of EoIP (Ethernet over IP) tunneling in MikroTik RouterOS?
- A. To replace VLAN tagging on trunk ports
- B. To provide QoS prioritization for bridged traffic
- C. To encrypt Ethernet traffic between two routers
- D. To create a Layer 2 tunnel over an IP network Correct answer
Option D is correct because EoIP creates a Layer 2 (Ethernet) tunnel over an IP network, allowing Ethernet frames to be transported transparently between remote sites. This enables bridging of remote LAN segments across Layer 3 infrastructure. EoIP does not provide encryption, replace VLANs, or offer QoS prioritization.
Which TWO statements about MikroTik EoIP tunnels are correct? (Choose two)
- A. EoIP tunnels provide built-in encryption for all traffic
- B. EoIP operates at Layer 3 and can only carry IP packets
- C. EoIP is a MikroTik proprietary protocol that uses GRE Correct answer
- D. Each EoIP tunnel requires a unique Tunnel ID per endpoint pair Correct answer
Options C and D are correct because EoIP is a MikroTik proprietary protocol that encapsulates Ethernet frames using GRE, and each EoIP tunnel requires a unique Tunnel ID that must match between the two endpoints. EoIP does not provide built-in encryption (A), and it operates at Layer 2, carrying full Ethernet frames including non-IP protocols (B).
IPsec
In MikroTik RouterOS, under which menu is IPsec configuration found?
- A. /interface ipsec
- B. /ip ipsec Correct answer
- C. /system ipsec
- D. /routing ipsec
Option B is correct because all IPsec configuration in MikroTik RouterOS is found under the /ip ipsec menu, including peers, policies, proposals, and installed SAs. The other menu paths (/routing, /system, /interface) do not contain IPsec settings.
Which TWO components must be configured on both MikroTik routers for a basic site-to-site IPsec tunnel? (Choose two)
- A. An IPsec Peer with matching authentication settings Correct answer
- B. A bridge group for IPsec interfaces
- C. An IPsec Policy defining the traffic selectors and encryption action Correct answer
- D. A GRE tunnel interface
Options A and C are correct because a basic site-to-site IPsec tunnel requires an IPsec Peer with matching authentication settings (pre-shared key, exchange mode, DH group) on both routers, and an IPsec Policy on each side defining the traffic selectors and encrypt action. A GRE tunnel (D) is optional and separate from IPsec, and a bridge group (B) is not required for IPsec.
Using the topology shown, when configuring an IPsec Peer on HQ for a site-to-site tunnel to BRANCH, what value should the Peer's Address field use?
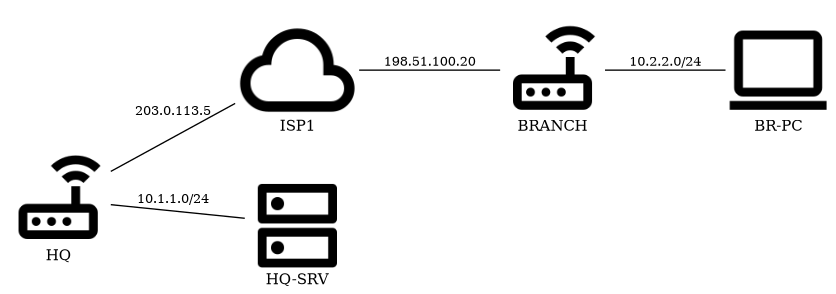
- A. 10.2.2.0/24 - the LAN behind BRANCH
- B. 198.51.100.20 - BRANCH's public address, the remote peer HQ negotiates with Correct answer
- C. 10.1.1.0/24 - the LAN behind HQ
- D. 203.0.113.5 - HQ's own public address
Option B is correct because an IPsec Peer's Address field identifies the remote peer HQ is negotiating with, which is BRANCH's public address, 198.51.100.20. Options A and C are wrong because those are LAN subnets behind each router, not peer addresses - those belong in the IPsec Policy's src/dst-address fields instead. Option D is wrong because a Peer entry needs the remote side's address, not HQ's own.
HotSpot
Which MikroTik menu is used to run the HotSpot Setup wizard?
- A. /system hotspot
- B. /tool hotspot
- C. /interface hotspot
- D. /ip hotspot Correct answer
Option D is correct because the HotSpot Setup wizard and all HotSpot configuration is found under /ip hotspot in MikroTik RouterOS. The other menu paths (/system hotspot, /interface hotspot, /tool hotspot) do not exist in RouterOS.
Which TWO login methods does MikroTik HotSpot support for user authentication? (Choose two)
- A. MAC address authentication Correct answer
- B. HTTP CHAP (challenge-response in the browser) Correct answer
- C. LDAP direct bind
- D. WPA2-Enterprise 802.1X
Options B and A are correct because MikroTik HotSpot supports HTTP CHAP, which uses a challenge-response mechanism in the browser to hash the password before sending, and MAC address authentication, which automatically authenticates devices based on their hardware address. WPA2-Enterprise 802.1X (D) is a wireless security feature separate from HotSpot, and LDAP direct bind (C) is not a native HotSpot login method.
Based on the output shown, what does the missing A flag on the second host (10.5.50.11) indicate?
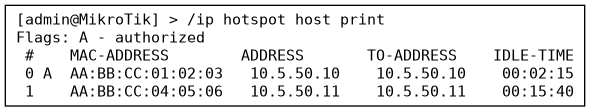
- A. That host belongs to a different HotSpot server, so the flag does not apply to it
- B. That host has not completed the HotSpot login, so it cannot pass traffic beyond the login page Correct answer
- C. That host is using a static IP-binding bypass entry, so no flag is needed
- D. That host's idle-time has exceeded the timeout, so it is about to be reassigned a new address
Option B is correct because the A flag specifically marks a host as authorized after completing the HotSpot login; a host without it, like 10.5.50.11, is still sitting at the login page and hasn't been granted access yet. Option C is wrong because a bypassed host would appear in the ip-binding list, not simply be missing a flag here. Options A and D invent explanations (a different server, an idle timeout) that the output gives no evidence for.
RADIUS
What is the primary function of a RADIUS server in a MikroTik network?
- A. To manage routing tables across multiple routers
- B. To encrypt all network traffic between clients and the server
- C. To centralize authentication, authorization, and accounting for network users Correct answer
- D. To assign IP addresses via DHCP
Option C is correct because RADIUS (Remote Authentication Dial-In User Service) provides centralized Authentication, Authorization, and Accounting (AAA) for network users, allowing a single server to manage access for multiple network access devices. It does not assign IP addresses via DHCP (B), encrypt traffic (C), or manage routing tables (D).
RADIUS uses TCP as its transport protocol.
- A. True
- B. False Correct answer
RADIUS uses UDP, not TCP, as its transport protocol. Standard RADIUS authentication uses UDP port 1812 and accounting uses UDP port 1813. UDP was chosen for RADIUS because it provides simpler, faster communication suitable for the request-response nature of authentication exchanges.
Free Study Guide
Read the free MikroTik MTCUME study guide: every exam topic explained in plain English, with diagrams, exam tips and the mistakes to avoid.
More MikroTik Practice Exams
Practise with realistic mock exams to prepare for your MikroTik certification.